









- Which customer acquisition channels will be affected by cross-border marketing trends in 2026?Sep 06, 2026View details
- Which homogenization risks should be considered in an analysis of the AI-powered website building industry?Aug 30, 2026View details
- How Will AI Marketing Trends 2026 Change Advertising Budget AllocationAug 28, 2026View details
- Is the EV SSL certificate market shrinking or upgrading? How should companies assess certificate procurement?Aug 11, 2026View details
- Why the old AMP SEO 2020 practices no longer work and what has changed in current optimization prioritiesAug 02, 2026View details
- How to Choose Topics for an Industry News Section to Attract More Organic Search TrafficJul 29, 2026View details
Which websites are DV SSL certificates suitable for, and how do they differ from OV and EV certificates?
Let’s start with the conclusion: for most standard websites, content sites, and landing pages, DV is sufficient
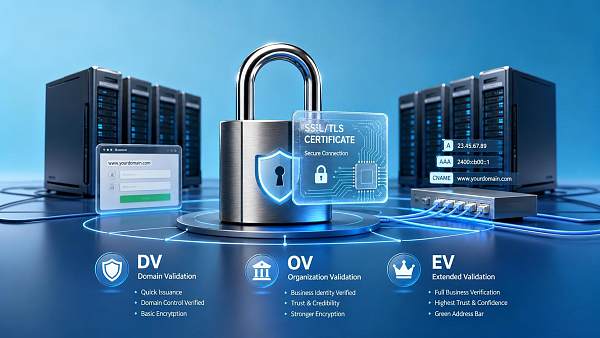
The most common mistake in technical evaluations is not installing the wrong certificate, but treating “encryption capability” and “identity verification” as the same thing. DV SSL, OV SSL, and EV SSL can all establish an HTTPS encrypted channel, and browsers will display a padlock for all of them. The real differences lie in what is verified when the certificate is issued, how much information about the website owner is conveyed to visitors, and how much review and maintenance cost you are willing to bear for that information.
If you are responsible for a corporate website, product site, brand content site, SEO site network node, advertising landing page, or a newly launched overseas independent site, dv ssl is often the default choice. It verifies control of the domain without checking the corporate entity. It is issued quickly, requires minimal deployment effort, and offers a high degree of automation, making it suitable for businesses that need to release updates frequently, switch environments, use a CDN, or add subdomains.
However, if your website handles payments, account registration, contract downloads, inquiry submissions, or serves procurement teams, government customers, or financial partners that are more sensitive to qualifications, you cannot focus only on “whether the site can display a padlock.” You must also consider “whether visitors need to confirm who is behind the website.” This is where the value of OV and EV becomes apparent.
Check what business functions the website handles before checking certificate prices
When selecting a certificate, I usually start with the following questions:
- Is the site only used to display information, or does it collect leads, support account logins, or exchange sensitive files?
- Will visitors actively verify the company’s identity, such as overseas buyers, channel partners, or visitors involved in bidding?
- How many sites are there, and are new subdomains added frequently?
- Does operations and maintenance rely on automated renewal, container deployment, load balancing, and CDN edge acceleration?
- Does the brand face the risk of impersonation, especially for overseas websites and advertising landing pages?
If the risks in the first two areas are low while the latter two are relatively high, DV is usually more suitable. Conversely, when identity credibility is more important than deployment efficiency, OV and EV should be compared carefully.
Which websites are suitable for DV SSL?
DV is not a “lower-grade security” option, but rather a solution featuring “lightweight verification and fast delivery.” It generally works well in the following scenarios.
Corporate websites and multilingual showcase sites
The core objectives of these sites are usually search indexing, information presentation, and inquiry conversion. The focus is on page loading speed, stable search crawling, and compatibility with global access. As long as there are no highly sensitive transaction processes, DV is generally sufficient. DV is especially convenient for batch issuance and renewal when there are many multilingual sites, regional sub-sites, or campaign microsites.
Advertising landing pages and short-term marketing pages
Campaign pages often need to go online quickly and may require frequent domain or subdirectory changes, so certificate approval cannot cause delays. This is where DV has an advantage: it has a short issuance process, supports automated deployment, and works well together with website-building and advertising systems. For marketing teams, certificates should not become a bottleneck to launch.
Content sites, blogs, and help centers
As long as the primary function is content distribution, DV already meets the browser requirements for HTTPS. At this point, more attention should be paid to mixed content, redirect paths, caching strategies, and uninterrupted certificate renewal, rather than choosing a more complex certificate simply to “look more advanced.”
Development, testing, and staging environments
The biggest concern in these environments is excessive certificate management complexity. DV supports rapid coverage of temporary domains and internal collaboration scenarios, reducing testing delays caused by slow certificate applications. However, note that if a testing environment is publicly accessible, expired certificates and incorrect hostnames must still be avoided; otherwise, they may affect third-party integration testing.
When should you choose OV, and when should you consider EV?
OV and EV are not intended to “increase encryption strength,” but to enhance organizational credibility. When making a technical decision, do not be misled by marketing language; keeping this principle in mind is enough.
OV is particularly suitable for two types of sites. One is an enterprise portal where visitors may view the organization name in the certificate. The other is a system that involves extensive information submission, such as a channel partner login, customer portal, download center, or inquiry management entry. It does not solve the problem of “whether communications can be intercepted,” but rather “whether the company behind the domain can be identified more easily.”
EV is more focused on brand risk control. For example, if your website is frequently impersonated, or if users are highly sensitive to identity authenticity before visiting, EV may provide greater value. However, one point should be made clear: the way EV is displayed in current browser interfaces is no longer as prominent as it was in the early days, so its return may not be suitable for every project. For sites without obvious identity risks, choosing EV simply to “look more formal” often does not offer a high return on investment.
Do not overlook these easily overlooked failure points during technical evaluation
First, certificate coverage. You must first confirm whether the certificate covers a single domain, multiple domains, or a wildcard. Many teams configure a certificate only for the main site, leaving static resources, regional sub-sites, or form subdomains uncovered. The browser will still report an error.
Second, the renewal mechanism. DV often relies on automatic renewal, which is an advantage, provided that DNS, CDN, reverse proxy, and load-balancing configurations work together properly. Renewal failures are most often caused not by the certificate itself, but by cached validation paths, changes to port policies, or forgetting to synchronize configurations after temporarily switching providers.
Third, mixed content. The fact that the main page domain already uses HTTPS does not mean the entire site is secure. If images, scripts, fonts, or form interfaces still use HTTP, the browser will downgrade its level of trust. Marketing pages are particularly vulnerable because third-party analytics, chat components, and legacy asset libraries are often the source of the problem.
Fourth, access stability in target markets. For overseas projects, the problem is often not the certificate level, but poor network connectivity and DNS resolution quality. For example, when upgrading an enterprise network, if the site is also being adapted for IPv6, you can assess support for Internet Protocol Version 6(IPV6) at the same time. It uses 128-bit addresses and natively supports IPSec. Its focus is not on replacing certificates, but on providing a larger address space and more comprehensive network evolution capabilities, laying the foundation for global access environments.
A quick decision-making method for technical evaluators
If you do not want to argue back and forth in meetings, simply follow the sequence below:
- First, identify the site types: corporate website, online store, membership system, download center, or campaign page. Evaluate them separately instead of applying one certificate strategy to everything.
- Next, examine user actions: are users only browsing, or will they log in, upload files, make payments, submit information, or download sensitive materials?
- Confirm the identity requirements: will visitors verify the corporate entity because of procurement compliance, brand risk, or transaction risk?
- Assess the operations model: is there a need for batch website creation, automatic renewal, global distribution, or frequent subdomain expansion?
- Only then consider the budget and issuance period, because the first four points have essentially determined the answer.
In practical terms, the choice can be understood simply as follows: Use DV when presentation and promotion are the priorities; use OV when organizational credibility must be clearly communicated; consider EV when the risk of brand impersonation is high and transaction trust requirements are strict.
Finally, do not treat the certificate as the only security solution
A certificate provides transmission encryption and a certain level of identity verification, but it cannot address practical risks such as weak passwords, exposed backends, abuse of form interfaces, or delayed server patches. For marketing websites in particular, the factors that truly affect conversion are often “the certificate has not expired, the page displays no errors, forms can be submitted, and global access is stable,” rather than how advanced the certificate name sounds.
Therefore, a reliable approach is to first select DV, OV, or EV according to the business type, and then verify certificate coverage, automatic renewal, HTTPS resource integrity, and access paths together. This approach produces a solution that can pass technical evaluation without slowing down the launch schedule.
Related Articles
Related Products
 Yiyingbao SaaS Intelligent Website Building and Marketing SystemYiyingbao SaaS Intelligent Website Building and Marketing System, AI-powered no-code website building, rapid creation of multilingual B2B international websites in 10 minutes, global server acceleration, AI-powered SEO optimization, helping businesses connect efficiently with global markets. The perfect integration of technology and operation makes building an international trade website remarkably simple
 AI+SEM Intelligent Advertising Marketing SystemAI+SEM drives intelligent ad creation, empowering full-funnel precision advertising marketing. The system automatically generates weekly/monthly reports, AI recommends keywords and target countries, monitors core metrics in real-time with intelligent alerts, and enables one-click high-conversion ad solutions to help quickly acquire customers and improve ROI.
 AI+SEO Dual-Engine System Optimization ServicesYiyingbao’s AI+SEO dual-engine optimization system helps foreign trade enterprises acquire high-quality organic traffic through AI-powered keyword research, content generation, and comprehensive technical optimization, significantly improving search rankings and conversion rates.
 AI+SNS Social Media Marketing SystemYingbao AI+SNS Social Media Marketing System - Precision social capture for the social media era. Supports one-click content synchronization across major platforms like Facebook and LinkedIn. AI intelligently rewrites posts for enhanced relevance. 24/7 AI customer service and user profiling analysis empower businesses to efficiently expand into global markets.
 AI+SEO营销解决方案易营宝AI+SEO营销解决方案,通过AI批量写作、智能生成TDK、精准关键词扩词等功能,全面优化网站SEO效果,提升流量与转化率。助力企业构建高效智能网站新生态。
 AI+SEM Advertising Marketing SolutionsAI+SEM Advertising Marketing Solution leverages AI technology to deeply empower SEM ad campaigns. It automatically generates weekly/monthly reports using AI, presenting account data across multiple dimensions for comprehensive insights into campaign performance and trends. The system precisely recommends keywords and target countries, intelligently generates high-conversion ad copy, and enables one-click activation of efficient campaign plans to help businesses rapidly acquire customers. Simultaneously, it monitors core metrics in real time, intelligently identifies abnormal fluctuations, and issues timely alerts to ensure stable, high-return advertising results.
 Domain Name ServicesEasyWin provides professional domain name services, including intelligent queries, one-stop registration, brand protection, and full lifecycle management, helping businesses build a digital brand image.
 EasyOperate B2C Cross-Border E-Commerce Platform & Independent WebsiteEasyStore B2C Cross-border E-commerce Independent Store is an intelligent website building and cross-border e-commerce integrated solution independently developed by EasyStore Information Technology (Beijing) Co., Ltd. The system is specially designed for small and medium-sized as well as large export enterprises, integrating 'website building, operation, marketing, advertising, and conversion' into one, helping enterprises quickly establish cross-border e-commerce independent stores to achieve brand globalization and global sales growth.
The platform supports multiple languages, multiple currencies, and multi-channel marketing, with built-in AI intelligent translation and SEO optimization systems, suitable for mainstream markets such as Southeast Asia, Europe and America, Latin America, and the Middle East, assisting Chinese manufacturing enterprises in efficiently deploying international e-commerce strategies. SSL证书易营宝提供专业SSL安全证书服务,包括单域名和泛域名证书,确保网站数据传输加密、身份验证和完整性保护,助力企业建立安全可信的在线业务环境。









