









- Which customer acquisition channels will be affected by cross-border marketing trends in 2026?Sep 06, 2026View details
- Which homogenization risks should be considered in an analysis of the AI-powered website building industry?Aug 30, 2026View details
- How Will AI Marketing Trends 2026 Change Advertising Budget AllocationAug 28, 2026View details
- Is the EV SSL certificate market shrinking or upgrading? How should companies assess certificate procurement?Aug 11, 2026View details
- Why the old AMP SEO 2020 practices no longer work and what has changed in current optimization prioritiesAug 02, 2026View details
- How to Choose Topics for an Industry News Section to Attract More Organic Search TrafficJul 29, 2026View details
How Can Website WAF Protection Reduce False Positives for Malicious Requests?
Early-morning alerts are often the most challenging for security managers: WAF interception volumes rise significantly, seemingly blocking attacks; however, the business team soon reports that overseas customers cannot submit inquiries, distributors cannot log in, and even advertising landing page conversions suddenly decline. At this point, the greatest danger is not only missed interceptions, but also legitimate traffic being mistakenly blocked due to inaccurate policies.
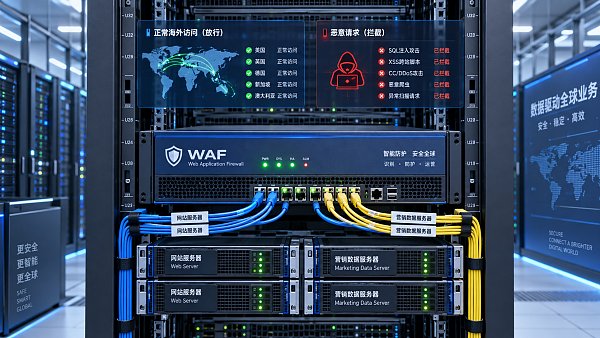
The value of website WAF protection lies in identifying and blocking attack requests such as SQL injection, cross-site scripting, malicious scanning, vulnerability exploitation, abnormal crawlers, and DDoS attacks. However, a WAF is essentially a security control layer that makes judgments based on rules, signatures, behavior, and risk scoring. The more complex a website's business is—with more form fields, URL parameters, multilingual content, third-party callbacks, and API interfaces—the more likely legitimate requests will be classified as risky simply by increasing interception intensity.
For websites responsible for overseas customer acquisition, advertising campaigns, and multilingual presentation, false positives are not merely a technical failure; they may also mean that an inquiry, an order, or a brand interaction is silently turned away. The key to reducing false positives is not simply to “relax the rules,” but to enable website WAF protection to truly understand business boundaries.
First, distinguish which “abnormal requests” are actually normal business activity
Many false positives stem from a misconception: treating unusual request characteristics as directly equivalent to malicious requests. In fact, many normal scenarios on cross-border business websites inherently have a high-risk appearance. For example, purchasers may enter product models, chemical names, or technical parameters containing special characters in inquiry forms; users may paste requirement descriptions containing links into messages; overseas customers may access the site through VPNs, corporate proxies, or shared outbound IPs; and redirect parameters from advertising platforms such as Google and Meta may be long and complexly encoded.
In addition, common functions on B2B marketing websites—such as file uploads, quotation downloads, ERP or CRM interface callbacks, multilingual searches, and on-site filtering—may also trigger general WAF rules. Without understanding specific business paths and merely increasing sensitivity from the perspective of an attack signature library, the security system may treat genuine customers as attackers.
Therefore, when reviewing interception logs, quality control and security personnel should not focus only on “how many requests were blocked,” but should also ask three questions: What resource did the request access? Which rule did it trigger? After the request occurred, was it accompanied by genuine user activity, such as page views, form submissions, logins, or order operations? These three questions determine whether to optimize a rule, add an exception, or maintain the interception.
Shift from “one standard for the entire site” to layered protection
To reduce false positives, the most effective approach is usually to apply layers based on asset value and business risk, rather than imposing the same strict policy on the entire domain. High-risk areas such as management backends, login portals, payment interfaces, and file management directories should maintain a high protection level; pages such as display pages, product detail pages, and public help centers can adopt policies that focus more on behavioral identification and access-frequency control.
For paths that are likely to carry complex parameters, such as form submissions, on-site searches, and API callbacks, separate policy groups can be established. The focus is not to disable detection entirely, but to validate requests based on interface expectations: which request methods, parameter names, content types, file formats, and file size ranges are allowed; requests that do not conform to the interface design can then be strictly blocked. This is more prudent than broadly disabling SQL injection or XSS protection.
For example, allowing an inquiry interface to accept English, Arabic, Russian, and text containing model symbols does not mean it should accept executable scripts of arbitrary fields and arbitrary lengths. Parameter allowlists, length limits, encoding standards, and secondary server-side validation can preserve both business flexibility and security boundaries.
Rule tuning must consider the “match context,” not just the rule name
The appearance of “suspected SQL injection” or “suspected XSS” in WAF logs does not necessarily mean that the rule is incorrect. Security personnel need to review the request in conjunction with its context, including source IP reputation, country or region of access, User-Agent, request frequency, Referer source, request parameters, response status code, and the behavioral sequence before and after the same session.
A form submission request originating from an advertising landing page after multiple normal page views, and a request that traverses hundreds of URLs in a short period while continuously varying injection statements, should not have the same risk level even if they trigger similar rules. Mature website WAF protection should make full use of risk scoring rather than relying on a “match means block” approach for individual rules.
It is recommended to divide rule optimization into three actions:
- Observe: For newly deployed or uncertain rules, first run them in alert or observation mode, collect samples of real traffic, and then decide whether to block.
- Narrow: If a rule generates false positives only for specific parameters or URLs, limit its scope of effect rather than disabling it site-wide.
- Escalate: For confirmed malicious request combinations, add rate limits, CAPTCHA challenges, IP reputation actions, or temporary blocking to avoid repeatedly relying on a single signature rule.
Among these, “observation mode” is especially suitable when a website is being redesigned, new multilingual pages are added, marketing automation tools are integrated, or new interfaces are launched. Reviewing traffic before reaching conclusions is usually more manageable than performing an emergency rollback after an incident occurs.
An allowlist is not a release list, but a controlled exception
Allowlists are necessary tools for resolving false positives, but they are also among the most easily abused tools. Common incorrect practices include directly allowlisting an entire office network segment, permanently allowing a certain country or region, or bypassing an entire category of security rules to solve a single issue. Although these actions may produce quick results, they can also allow attackers to enter through trusted paths.
More appropriate allowlist management should follow the principles of “minimum scope, clear duration, and traceable review.” Prioritize exceptions for specific URLs, request methods, parameter combinations, or verified third-party callback signatures; if IP-based access must be allowed, record the purpose, responsible person, and expiration time, and review it regularly. For partner systems, payment platforms, CRM synchronization interfaces, and similar services, signature verification, Token validation, or mutual authentication should be used whenever possible, rather than relying solely on source IPs.
Geographic blocking should also be used cautiously in overseas access scenarios. A high proportion of attacks from certain regions does not mean that there are no genuine buyers in those regions. For foreign trade companies, an indiscriminate country-level block may directly result in the loss of potential markets. By comparison, restricting abnormal access frequency, known malicious IPs, spoofed crawlers, and high-risk request chains is often more aligned with actual business needs.
Incorporate business changes into the WAF change management process
False positives often occur after a website launches new functions: adding product filter criteria, replacing form plugins, integrating payments, adjusting URL structures, launching new advertising channels, or migrating to a multilingual website architecture. Development, marketing, and security teams each complete their own work without synchronizing WAF policies, and real users ultimately become “compatibility testers.”
It is recommended to establish a lightweight but clearly defined change management loop. Before launch, the business or development team should describe new paths, parameters, and third-party services; security personnel should check rule matches based on the test environment or canary traffic; and within 24 to 72 hours after launch, they should closely monitor the 403 rate, form success rate, login failure rate, API error rate, and fluctuations in advertising conversions. When anomalies occur, it should be possible to quickly identify whether they are caused by the WAF, application, CDN, or third-party service, rather than blindly disabling protection.
This process is particularly important for enterprises using intelligent website building, multilingual websites, and cross-border online stores. For platforms such as Yiyingbao that cover website building, SEO, advertising landing pages, and overseas marketing scenarios, project configurations should also focus on matching page access flows with security policies: whether advertising parameters are retained, whether forms in different languages can be submitted properly, whether search engine crawlers receive appropriate access permissions, and whether marketing tool callbacks are misclassified. Security and growth are not opposites, provided that they share the same set of verifiable traffic rules.
Use several metrics to determine whether a WAF is “blocking accurately”
The effectiveness of website WAF protection cannot be evaluated solely by the number of blocked attacks. A very high interception volume may sometimes indicate that policies are overly broad. Metrics that are more worthwhile to track continuously include: the proportion of manually confirmed false positives among requests rejected by the WAF; the proportion of 403 responses for key forms and login interfaces; the number of allowlist entries and their long-term retention; the recurrence rate of attacks after rule adjustments; and changes in business conversions during abnormal periods.
Searchable logs and change records should also be retained. If a false positive does not leave behind a rule ID, request sample, handler, and recovery time, the same mistakes are likely to recur during the next redesign. For security managers, the ideal state is not “never receiving alerts,” but ensuring that every alert can be explained, every exception can be reviewed, and every allowed request does not expand unknown risks.
Ultimately, reducing false positives with website WAF protection does not rely on lowering security thresholds, but on more precise business identification, a narrower policy scope, and more continuous monitoring and review. When protection rules can keep pace with changes in website functions, overseas traffic, and marketing flows, the WAF can become a guardrail for stable business operations rather than a wall standing in front of customers.
Related Articles



Related Products
 Yiyingbao SaaS Intelligent Website Building and Marketing SystemYiyingbao SaaS Intelligent Website Building and Marketing System, AI-powered no-code website building, rapid creation of multilingual B2B international websites in 10 minutes, global server acceleration, AI-powered SEO optimization, helping businesses connect efficiently with global markets. The perfect integration of technology and operation makes building an international trade website remarkably simple
 AI+SEM Intelligent Advertising Marketing SystemAI+SEM drives intelligent ad creation, empowering full-funnel precision advertising marketing. The system automatically generates weekly/monthly reports, AI recommends keywords and target countries, monitors core metrics in real-time with intelligent alerts, and enables one-click high-conversion ad solutions to help quickly acquire customers and improve ROI.
 AI+SEO Dual-Engine System Optimization ServicesYiyingbao’s AI+SEO dual-engine optimization system helps foreign trade enterprises acquire high-quality organic traffic through AI-powered keyword research, content generation, and comprehensive technical optimization, significantly improving search rankings and conversion rates.
 AI+SNS Social Media Marketing SystemYingbao AI+SNS Social Media Marketing System - Precision social capture for the social media era. Supports one-click content synchronization across major platforms like Facebook and LinkedIn. AI intelligently rewrites posts for enhanced relevance. 24/7 AI customer service and user profiling analysis empower businesses to efficiently expand into global markets.
 AI+SEO营销解决方案易营宝AI+SEO营销解决方案,通过AI批量写作、智能生成TDK、精准关键词扩词等功能,全面优化网站SEO效果,提升流量与转化率。助力企业构建高效智能网站新生态。
 AI+SEM Advertising Marketing SolutionsAI+SEM Advertising Marketing Solution leverages AI technology to deeply empower SEM ad campaigns. It automatically generates weekly/monthly reports using AI, presenting account data across multiple dimensions for comprehensive insights into campaign performance and trends. The system precisely recommends keywords and target countries, intelligently generates high-conversion ad copy, and enables one-click activation of efficient campaign plans to help businesses rapidly acquire customers. Simultaneously, it monitors core metrics in real time, intelligently identifies abnormal fluctuations, and issues timely alerts to ensure stable, high-return advertising results.
 Domain Name ServicesEasyWin provides professional domain name services, including intelligent queries, one-stop registration, brand protection, and full lifecycle management, helping businesses build a digital brand image.
 EasyOperate B2C Cross-Border E-Commerce Platform & Independent WebsiteEasyStore B2C Cross-border E-commerce Independent Store is an intelligent website building and cross-border e-commerce integrated solution independently developed by EasyStore Information Technology (Beijing) Co., Ltd. The system is specially designed for small and medium-sized as well as large export enterprises, integrating 'website building, operation, marketing, advertising, and conversion' into one, helping enterprises quickly establish cross-border e-commerce independent stores to achieve brand globalization and global sales growth.
The platform supports multiple languages, multiple currencies, and multi-channel marketing, with built-in AI intelligent translation and SEO optimization systems, suitable for mainstream markets such as Southeast Asia, Europe and America, Latin America, and the Middle East, assisting Chinese manufacturing enterprises in efficiently deploying international e-commerce strategies. SSL证书易营宝提供专业SSL安全证书服务,包括单域名和泛域名证书,确保网站数据传输加密、身份验证和完整性保护,助力企业建立安全可信的在线业务环境。









