









- Which customer acquisition channels will be affected by cross-border marketing trends in 2026?Sep 06, 2026View details
- Which homogenization risks should be considered in an analysis of the AI-powered website building industry?Aug 30, 2026View details
- How Will AI Marketing Trends 2026 Change Advertising Budget AllocationAug 28, 2026View details
- Is the EV SSL certificate market shrinking or upgrading? How should companies assess certificate procurement?Aug 11, 2026View details
- Why the old AMP SEO 2020 practices no longer work and what has changed in current optimization prioritiesAug 02, 2026View details
- How to Choose Topics for an Industry News Section to Attract More Organic Search TrafficJul 29, 2026View details
Why does an expired SSL certificate on a multilingual website cause inaccessibility in certain regions?
Why Can an Expired SSL Certificate on a Multilingual Website Make It Inaccessible in Some Regions?
When an SSL certificate for a multilingual website expires, it may appear to be merely a routine operational oversight. In practice, however, it often manifests as “the site cannot be opened in certain countries, some language versions malfunction, while some users can still access it.” This can easily lead maintenance personnel to mistakenly attribute the issue to network fluctuations, CDN failures, or local access restrictions. More accurately, certificate expiration is the trigger, while CDN edge nodes, domain resolution paths, browser validation policies, and site deployment structures in different regions determine the scope in which the failure becomes visible.
For websites responsible for acquiring overseas customers, this is not simply a technical alert. If a Google Ads landing page cannot establish a secure connection, it may directly affect ad review and access; users arriving through organic search who see a certificate risk warning will often not proceed to submit an inquiry; links already deployed through social media and email marketing may also suddenly fail in a specific target region. SSL certificate management for multilingual websites should therefore be handled together with domains, CDNs, marketing pages, and monitoring systems.
What Exactly Does the Browser Block After a Certificate Expires?
When an HTTPS connection is established, the server provides the browser with a digital certificate based on the X.509 framework. The browser checks the certificate validity period, issuance chain, domain matching, trusted status of the issuing authority, and related revocation information. Once the “Not After” time in the certificate has passed, the client will generally consider the server identity no longer verifiable as trusted, displaying messages such as connection not private, certificate expired, or secure connection failed.
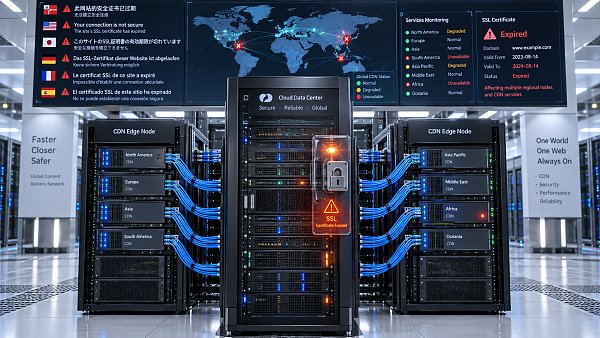
Strictly speaking, if the leaf certificate for the same domain and the same access path has expired, all clients with normal validation capabilities may be affected. The so-called “inaccessible in some regions” does not mean that the expired certificate becomes invalid only in a particular country; rather, users in different regions may not actually connect to exactly the same service node and may not receive the same certificate configuration.
Multilingual sites are especially prone to this complexity. Language versions may be distinguished by subdomains, such as de.example.com and ja.example.com; they may also use directory paths; and some companies deploy their online stores, main sites, and advertising landing pages on different platforms. If the certificate SAN domain list is incomplete, or if a subdomain is still bound to an old certificate, situations may occur where the English site works normally while the Japanese site is blocked, or the homepage opens but the inquiry page cannot submit.
Why Does the Same Expiration Produce Inconsistent Results Across Different Regions?
The most common reason is that certificates have not been synchronized across CDN edge nodes. A global CDN assigns requests to different nodes based on user location, network quality, and routing rules. After renewal is completed, if the origin server, load balancer, and CDN console are not updated consistently, or if the new certificate has not yet been distributed to all edge nodes, users in North America may receive the new certificate while users in Europe or Southeast Asia still reach nodes retaining the old certificate. In this case, testing only from the company network and finding that “the website has recovered” does not mean that recovery has occurred globally.
The second type of issue comes from DNS and traffic routing. Multilingual websites often use intelligent DNS resolution, regional resolution, or multiple CNAME records, so different countries may receive different IP addresses. If the maintenance team updates the entry point corresponding to the primary domain but misses a regional route, an old IPv6 address, or a backup load-balancing address, users will connect to a server still running an expired certificate. Cases where IPv4 works normally while IPv6 fails are not uncommon during troubleshooting.
Another source of variation is the client itself. Newer browsers and operating systems typically handle invalid certificates more strictly; older devices, enterprise intranet proxies, managed browsers, or devices with different cache states may display warnings differently. When an intermediate certificate chain is missing or the chain order is configured incorrectly, some environments may complete the chain through cached certificates, while others will terminate the handshake directly. The fact that a small number of devices “can still open the site” should not be used to conclude that there is no issue with the certificate chain.
First Distinguish Between “Certificate Expiration” and “Renewal Not Yet Taking Effect”
During incident handling, one of the easiest ways to waste time is to look only at the certificate management console showing “issued.” Certificate issuance, server installation, CDN binding, and edge node deployment are separate steps. Having obtained a new certificate does not mean external users are currently using it. TLS handshake checks should be initiated from the affected regions, carriers, or cloud servers to confirm the certificate serial number, validity period, subject alternative names, and certificate chain actually returned, rather than checking only local files.
Troubleshooting can proceed along the access path: first confirm which IPv4 and IPv6 addresses the affected URL ultimately resolves to; then check the certificates returned by each address on port 443; next verify the certificate binding relationships for the CDN domain, origin domain, load balancer listener, and origin web service; and finally test whether the correct SNI hostname is included. Without SNI, the server may return the default site certificate, which can conceal or create domain mismatch issues.
Certificate Management for Multilingual Sites Cannot Focus Only on the Primary Domain
The maintenance checklist should at minimum cover the production domain, versions with and without www, all language subdomains, store domains, static resource domains, advertising short-link redirect domains, and any testing or migration entry points that may still be in use. Directory-based language sites may not require separate certificates, but as long as pages reference other HTTPS resources, the resource domains must also be included in monitoring. Otherwise, the page itself may open normally, while images, scripts, payment components, or form interfaces may be blocked by the browser.
Automated renewal is worth adopting, but it is not a “set it and forget it” solution. Automation can address only part of the certificate application or renewal process. Whether DNS validation permissions remain valid, whether deployment scripts cover all nodes, whether the CDN correctly references the new certificate, and whether external validation is completed after changes still require clear ownership. It is recommended to set multiple reminders before expiration and retain certificate fingerprints, binding locations, renewal methods, responsible persons, and rollback plans. For sites with peak marketing campaigns, the expiration window should also avoid periods of concentrated advertising, trade show promotion, and new product launches.
Moving from Restored Access to Continuously Verifiable Maintenance
For integrated website and marketing services, the value in handling such issues is not simply managing certificates on behalf of clients, but linking technical status with traffic entry points. Since 2013, Yingyingbao Information Technology (Beijing) Co., Ltd. has provided digital services for companies expanding overseas. Its business scenarios in intelligent website building, multilingual websites, cross-border e-commerce stores, SEO, advertising, and social media typically involve domain access, page campaigns, and ongoing maintenance across different markets. For such platform-based projects, certificate monitoring should be incorporated into site publishing and marketing campaign checks rather than handled only after user complaints arise.
When feedback indicates that “the site cannot be opened in some regions,” first record the user’s country, accessed domain, device and browser, error screenshot, and approximate time. Then verify these details against regional DNS resolution and node logs, which is often more effective than repeatedly refreshing the page. After the fix is completed, the homepage, language entry points, forms, store checkout pages, and advertising landing pages should also be retested through actual access paths in target markets. Restoring the certificate is only the starting point; a maintenance cycle is truly complete only after confirming that overseas users can consistently access the site and complete conversions.
Related Articles



Related Products
 Yiyingbao SaaS Intelligent Website Building and Marketing SystemYiyingbao SaaS Intelligent Website Building and Marketing System, AI-powered no-code website building, rapid creation of multilingual B2B international websites in 10 minutes, global server acceleration, AI-powered SEO optimization, helping businesses connect efficiently with global markets. The perfect integration of technology and operation makes building an international trade website remarkably simple
 AI+SEM Intelligent Advertising Marketing SystemAI+SEM drives intelligent ad creation, empowering full-funnel precision advertising marketing. The system automatically generates weekly/monthly reports, AI recommends keywords and target countries, monitors core metrics in real-time with intelligent alerts, and enables one-click high-conversion ad solutions to help quickly acquire customers and improve ROI.
 AI+SEO Dual-Engine System Optimization ServicesYiyingbao’s AI+SEO dual-engine optimization system helps foreign trade enterprises acquire high-quality organic traffic through AI-powered keyword research, content generation, and comprehensive technical optimization, significantly improving search rankings and conversion rates.
 AI+SNS Social Media Marketing SystemYingbao AI+SNS Social Media Marketing System - Precision social capture for the social media era. Supports one-click content synchronization across major platforms like Facebook and LinkedIn. AI intelligently rewrites posts for enhanced relevance. 24/7 AI customer service and user profiling analysis empower businesses to efficiently expand into global markets.
 AI+SEO营销解决方案易营宝AI+SEO营销解决方案,通过AI批量写作、智能生成TDK、精准关键词扩词等功能,全面优化网站SEO效果,提升流量与转化率。助力企业构建高效智能网站新生态。
 AI+SEM Advertising Marketing SolutionsAI+SEM Advertising Marketing Solution leverages AI technology to deeply empower SEM ad campaigns. It automatically generates weekly/monthly reports using AI, presenting account data across multiple dimensions for comprehensive insights into campaign performance and trends. The system precisely recommends keywords and target countries, intelligently generates high-conversion ad copy, and enables one-click activation of efficient campaign plans to help businesses rapidly acquire customers. Simultaneously, it monitors core metrics in real time, intelligently identifies abnormal fluctuations, and issues timely alerts to ensure stable, high-return advertising results.
 Domain Name ServicesEasyWin provides professional domain name services, including intelligent queries, one-stop registration, brand protection, and full lifecycle management, helping businesses build a digital brand image.
 EasyOperate B2C Cross-Border E-Commerce Platform & Independent WebsiteEasyStore B2C Cross-border E-commerce Independent Store is an intelligent website building and cross-border e-commerce integrated solution independently developed by EasyStore Information Technology (Beijing) Co., Ltd. The system is specially designed for small and medium-sized as well as large export enterprises, integrating 'website building, operation, marketing, advertising, and conversion' into one, helping enterprises quickly establish cross-border e-commerce independent stores to achieve brand globalization and global sales growth.
The platform supports multiple languages, multiple currencies, and multi-channel marketing, with built-in AI intelligent translation and SEO optimization systems, suitable for mainstream markets such as Southeast Asia, Europe and America, Latin America, and the Middle East, assisting Chinese manufacturing enterprises in efficiently deploying international e-commerce strategies. SSL证书易营宝提供专业SSL安全证书服务,包括单域名和泛域名证书,确保网站数据传输加密、身份验证和完整性保护,助力企业建立安全可信的在线业务环境。









