









- Which customer acquisition channels will be affected by cross-border marketing trends in 2026?Sep 06, 2026View details
- Which homogenization risks should be considered in an analysis of the AI-powered website building industry?Aug 30, 2026View details
- How Will AI Marketing Trends 2026 Change Advertising Budget AllocationAug 28, 2026View details
- Is the EV SSL certificate market shrinking or upgrading? How should companies assess certificate procurement?Aug 11, 2026View details
- Why the old AMP SEO 2020 practices no longer work and what has changed in current optimization prioritiesAug 02, 2026View details
- How to Choose Topics for an Industry News Section to Attract More Organic Search TrafficJul 29, 2026View details
How can encrypted storage for data privacy be implemented? Key implementation points from access control to backup strategy
Why Data Privacy Encrypted Storage Cannot Be Judged by “Encryption” Alone
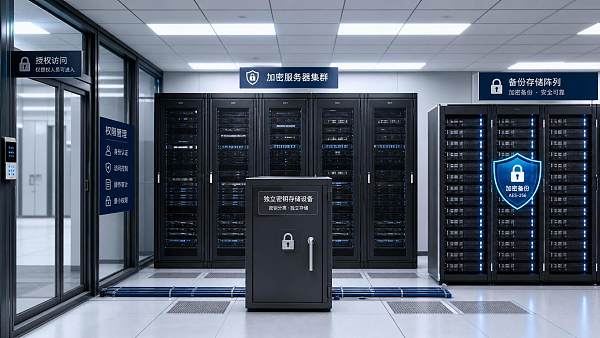
Data privacy encrypted storage is often understood as simply applying an encryption algorithm. However, in real business operations, what truly determines the outcome is often not the algorithm itself, but whether permissions, keys, logs, backups, and recovery are implemented together.
Judging from recent changes, regulatory requirements have become more detailed, and attack methods have become more covert. Many data leaks do not occur because there is no encryption, but because account permissions are excessive, key management is disorganized, or backup copies remain exposed for a long time.
This also means that data privacy encrypted storage is not a one-time purchase, nor does it end when a feature goes live. It is more like a continuously operating control system that requires policies, processes, and technologies to work together.
For integrated website and marketing service businesses, the data scope usually covers customer information, form leads, advertising account information, order records, access logs, and multilingual website content. Data is dispersed and team collaboration is frequent, which is exactly where risks are easily amplified.
Define Boundaries First: Which Data Must Be Included in Encrypted Storage
For data privacy encrypted storage, the first step is not buying tools, but classifying data first. Only by knowing which data is most sensitive can subsequent permission and backup strategies have a clear basis.
A common practice is to classify data across four dimensions: identity identification, transaction impact, consequences of business interruption, and compliance requirements. The clearer the classification, the easier the controls are to enforce.
- Personal information such as customer names, phone numbers, email addresses, and addresses should be prioritized for data privacy encrypted storage.
- Inquiry content, quotation documents, contract materials, and payment records are recommended to be handled as highly sensitive data.
- Backend access logs, operation logs, API tokens, and Cookie identifiers should not be ignored either.
- Marketing materials themselves may not necessarily be sensitive, but campaign strategies, audience segments, and conversion data usually need protection.
If an enterprise operates an independent website, a cross-border online store, and an advertising system at the same time, it should also add a data flow map. Where data is collected from, which systems it passes through, who can access it, and where it is backed up should all be clearly marked.
Many projects move slowly not because the technology is difficult, but because the boundaries were not clarified thoroughly at the beginning. As a result, high-risk data and ordinary data are placed together, and the data privacy encrypted storage strategy naturally loses focus.
The Key to Implementing Permission Management Is Not the Number of Accounts, but Least Privilege
For data privacy encrypted storage to be truly effective, permission management must be tightened first. This is because most leaks do not happen when encryption is broken, but when attackers obtain an account that already has access.
In actual implementation, it is recommended to design permissions around job roles rather than granting temporary permissions around individuals. When role-based permissions are fixed, personnel changes are less likely to leave historical access gaps.
- Authorize viewing, exporting, modifying, deleting, and approval separately.
- Highly sensitive data should be invisible by default and temporarily enabled through application and approval.
- Set expiration times for outsourced personnel and temporary project members, and automatically revoke permissions.
- Separate administrator accounts from business accounts to avoid shared super privileges.
A more obvious signal is that many teams already have enough permission rules; what they lack is continuous review. Checking high-privilege accounts once a month and conducting an over-privilege scan once a quarter is often more effective than writing more policies.
If the business involves overseas marketing collaboration, cross-region access must also be considered. Abnormal login locations, bulk exports late at night, and concurrent logins from multiple locations using the same account should all be included in alert rules.
Key Control Is the Real Foundation of Data Privacy Encrypted Storage
Many enterprises have already implemented database encryption, file encryption, and even disk encryption, but their keys are still stored locally on application servers. In this case, once the host is compromised, the value of encrypted storage is greatly reduced.
Therefore, whether data privacy encrypted storage can be effectively implemented depends mainly on whether keys are independent, whether they are rotated, and whether they are auditable. Key management must be upgraded from “usable” to “controllable”.
- Store keys separately from business data, avoiding the same machine and the same database.
- Set a key rotation cycle, with priority systems preferably rotating keys quarterly.
- Key usage must leave records, and who used which key at what time must be traceable.
- Prohibit transmitting keys in plaintext through documents, chat tools, or spreadsheets.
In actual business operations, transmission encryption and storage encryption must also be distinguished. The former addresses link security, while the latter addresses read-access risks after data is stored. Both are indispensable, but they cannot replace each other.
If the system is relatively large in scale, it is recommended to connect key management to a unified platform. The benefits are straightforward: unified policies, unified permissions, unified auditing, and easier issue location when problems occur.
If the Backup Strategy Is Poor, Encrypted Storage May Still Fall Short
Many teams focus entirely on the production database while neglecting the backup database. In reality, backups are often retained for longer periods and checked less frequently. Once they are unencrypted or permissions become uncontrolled, the risk may be even greater.
Therefore, data privacy encrypted storage must cover backup copies. Whether it is local backup, off-site backup, or object storage archiving, as long as sensitive data can be restored from it, it should be included under the same protection standards.
A relatively reliable strategy usually includes the following points:
- Encrypt backup files by default and prohibit generating plaintext copies.
- Manage backup accounts independently and do not mix them with production accounts.
- Retain at least one offline or immutable backup.
- Conduct recovery drills regularly to verify that backups are truly usable.
The most easily overlooked part here is recovery testing. Many enterprises have backups but have never performed a complete recovery. Once they encounter accidental deletion, ransomware, or system damage, they discover that keys do not match, versions are incompatible, and the recovery window far exceeds what the business can tolerate.
Turn Standards into Actions: Four Types of Checks Are Most Worth Normalizing
After the technical solution is built, what truly creates the gap is daily execution. Whether data privacy encrypted storage remains stable does not depend on the thickness of documentation, but on whether inspection actions can be sustained.
These checks do not need to be overly complex; the key is to form a closed loop. After problems are found, it must be possible to identify the person responsible, the remediation deadline, and the review results. Otherwise, inspections will only remain superficial.
Implement Strategies Together with Business Systems So They Can Truly Operate
For enterprises running website development, SEO optimization, advertising campaigns, and social media operations in parallel, data privacy encrypted storage cannot be implemented in only one system. A unified standard must be applied across the official website, online store, forms, CRM, advertising platforms, and analytics platforms.
AI-driven enterprise-level SaaS intelligent website building and overseas marketing platforms like 易营宝 often carry multilingual websites, inquiry data, advertising leads, and conversion analytics. At this point, it becomes even more necessary to place the website building system, marketing system, and data management system under the same governance framework.
A practical implementation path can follow three steps. First, complete data inventory and classification; then launch permission and key rules; finally, complete backup recovery and audit linkage. This pace is more stable and also more conducive to cross-department execution.
Ultimately, data privacy encrypted storage is not for display, but for reducing real risks. As long as the four matters of minimizing permissions, separating keys, ensuring backups are recoverable, and making logs auditable are implemented solidly, the entire system can move from “looking secure” to “truly controllable”.
Related Articles



Related Products
 Yiyingbao SaaS Intelligent Website Building and Marketing SystemYiyingbao SaaS Intelligent Website Building and Marketing System, AI-powered no-code website building, rapid creation of multilingual B2B international websites in 10 minutes, global server acceleration, AI-powered SEO optimization, helping businesses connect efficiently with global markets. The perfect integration of technology and operation makes building an international trade website remarkably simple
 AI+SEM Intelligent Advertising Marketing SystemAI+SEM drives intelligent ad creation, empowering full-funnel precision advertising marketing. The system automatically generates weekly/monthly reports, AI recommends keywords and target countries, monitors core metrics in real-time with intelligent alerts, and enables one-click high-conversion ad solutions to help quickly acquire customers and improve ROI.
 AI+SEO Dual-Engine System Optimization ServicesYiyingbao’s AI+SEO dual-engine optimization system helps foreign trade enterprises acquire high-quality organic traffic through AI-powered keyword research, content generation, and comprehensive technical optimization, significantly improving search rankings and conversion rates.
 AI+SNS Social Media Marketing SystemYingbao AI+SNS Social Media Marketing System - Precision social capture for the social media era. Supports one-click content synchronization across major platforms like Facebook and LinkedIn. AI intelligently rewrites posts for enhanced relevance. 24/7 AI customer service and user profiling analysis empower businesses to efficiently expand into global markets.
 AI+SEO营销解决方案易营宝AI+SEO营销解决方案,通过AI批量写作、智能生成TDK、精准关键词扩词等功能,全面优化网站SEO效果,提升流量与转化率。助力企业构建高效智能网站新生态。
 AI+SEM Advertising Marketing SolutionsAI+SEM Advertising Marketing Solution leverages AI technology to deeply empower SEM ad campaigns. It automatically generates weekly/monthly reports using AI, presenting account data across multiple dimensions for comprehensive insights into campaign performance and trends. The system precisely recommends keywords and target countries, intelligently generates high-conversion ad copy, and enables one-click activation of efficient campaign plans to help businesses rapidly acquire customers. Simultaneously, it monitors core metrics in real time, intelligently identifies abnormal fluctuations, and issues timely alerts to ensure stable, high-return advertising results.
 Domain Name ServicesEasyWin provides professional domain name services, including intelligent queries, one-stop registration, brand protection, and full lifecycle management, helping businesses build a digital brand image.
 EasyOperate B2C Cross-Border E-Commerce Platform & Independent WebsiteEasyStore B2C Cross-border E-commerce Independent Store is an intelligent website building and cross-border e-commerce integrated solution independently developed by EasyStore Information Technology (Beijing) Co., Ltd. The system is specially designed for small and medium-sized as well as large export enterprises, integrating 'website building, operation, marketing, advertising, and conversion' into one, helping enterprises quickly establish cross-border e-commerce independent stores to achieve brand globalization and global sales growth.
The platform supports multiple languages, multiple currencies, and multi-channel marketing, with built-in AI intelligent translation and SEO optimization systems, suitable for mainstream markets such as Southeast Asia, Europe and America, Latin America, and the Middle East, assisting Chinese manufacturing enterprises in efficiently deploying international e-commerce strategies. SSL证书易营宝提供专业SSL安全证书服务,包括单域名和泛域名证书,确保网站数据传输加密、身份验证和完整性保护,助力企业建立安全可信的在线业务环境。









