









- The U.S. has ended the $800 de minimis exemption for non-postal shipments; express courier packages must be formally declared.Nov 16, 2026View details
- ASEAN Signs Digital Economy Framework Agreement, Moving Toward Harmonized Cross-Border E-Commerce RulesNov 15, 2026View details
- Shenzhen Becomes the First City in Mainland China to Exceed RMB 5 Trillion in Foreign TradeNov 15, 2026View details
- Fujian Announces the First Batch of Provincial-Level Cross-Border E-Commerce Industrial Parks and Key Brands for CultivationNov 14, 2026View details
- Amazon Global Store Announces the Launch of the 2026 Black Friday Global Shopping SeasonNov 14, 2026View details
- CCTV.com Examines APEC’s Role in China’s Foreign TradeNov 12, 2026View details
How to Handle Privacy Policies and Cookie Consent in German Website Development
German website development must not only balance conversion and local user experience, but also properly address privacy policies and Cookie consent to reduce compliance risks and safeguard user data security and brand trust.
The key consideration for German website development: first determine whether actual data processing activities exist
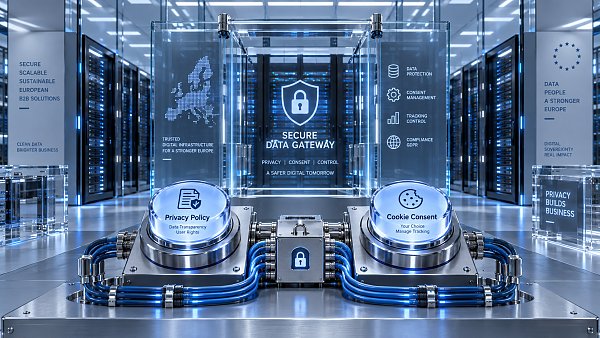
For websites targeting the German, Austrian and Swiss markets, privacy compliance cannot be addressed simply by adding a statement at the bottom of the page. As long as a website collects, transmits, stores or analyzes visitor data, it must establish a demonstrable processing mechanism in accordance with the GDPR and local German rules.
Quality control and security management personnel should first focus on which services the website actually uses. Inquiry forms, online chat, web analytics, embedded maps, remarketing pixels, YouTube videos, font libraries and third-party payment tools may all transmit personal data externally.
When assessing risks, it is not enough to consider whether users are asked to provide their names or email addresses. IP addresses, device identifiers, Cookie IDs, browsing behavior and advertising audience labels may also constitute identifiable or linkable personal data in most circumstances.
Therefore, compliance for German website development should focus on five questions: “Where does the data come from, where does it go, why is it processed, how long is it retained, and who can access it?” If a company cannot clearly answer these questions, even the most complete privacy policy and Cookie banner will struggle to withstand scrutiny.
Privacy policies should not use templates; they must correspond to website functions item by item
The German version of a privacy policy is generally presented as a Datenschutzerklärung. Its purpose is not only to inform users, but also to publicly explain the company’s data processing activities. Its content must be consistent with the website’s actual functions and must not be directly translated from a Chinese website or copied from competitor websites.
A usable policy should clearly identify the data controller’s name, contact address, privacy contact or data protection officer, and explain the legal basis for each category of data processing. Common bases include user consent, contract performance, legal obligations and the company’s legitimate interests.
Form modules need to specify the fields collected, purpose of use, processing basis, retention period and recipients. If inquiries enter a CRM, email marketing system or overseas sales team, the relevant systems, internal permissions and cross-border transfer arrangements should also be explained.
For security management personnel, it is particularly important to verify the actual deployment locations of service providers. When using U.S. analytics tools, cloud storage, marketing automation platforms or customer service systems, they should assess whether transfers outside the EU exist and retain data processing agreements and relevant safeguards.
The privacy policy should also state how users can exercise their rights of access, rectification, erasure, restriction of processing, data portability and withdrawal of consent. Companies should establish internal response procedures accordingly, avoiding situations where public website commitments are unsupported by personnel, timelines and records.
The key to Cookie consent is not the banner, but whether tracking actually stops after refusal
German users are generally sensitive to Cookie banners, and the regulatory focus is clear: except for technical Cookies necessary for website operation, analytics, advertising, personalization and third-party media Cookies should generally be loaded only after users provide explicit consent.
A compliant Cookie consent management platform should provide equally visible options such as “Accept,” “Reject” and “Customize Settings.” Hiding the rejection option on a secondary page, using misleading colors, or requiring users to click repeatedly to close the banner may all increase the risk of complaints and enforcement action.
More importantly, after users click reject, Google Analytics, Google Ads, Meta Pixel, Hotjar and remarketing code must not continue to write Cookies or initiate tracking requests. Many websites appear to have a banner, but their scripts actually execute when the page loads, which is a common issue.
It is recommended to use browser developer tools or scanning tools during launch acceptance testing to check four states separately: “No selection,” “Reject,” “Accept analytics only” and “Accept all.” Focus on whether third-party requests, Cookie writing and tag manager trigger rules are consistent.
The Cookie settings page should display the name, provider, duration and purpose by category, and allow users to modify their choices at any time. After users withdraw consent, subsequent tracking should stop; data already generated should be handled according to established retention and deletion policies.
Website development, marketing and data security need to be designed together at the beginning of the project
Many companies only carry out compliance remediation after German website development has been completed, often discovering that forms, advertising attribution, embedded content and data interfaces all require rework. A more prudent approach is to incorporate privacy requirements into requirement reviews, development testing and launch acceptance checklists.
At project initiation, a data map can first be created: through which pages visitors enter, at which points they submit data, which third-party scripts participate in processing, and which systems the data ultimately enters. This map can support privacy policy drafting while also helping identify security weaknesses.
At the technical level, the principle of data minimization should be prioritized. Inquiry forms should retain only the fields needed for initial communication and should not collect personal information unrelated to the transaction by default; backend accounts should implement least privilege, strong passwords, multi-factor authentication and operation log management.
For B2B companies in laser equipment, industrial manufacturing and similar sectors, product material downloads, quotation requests and after-sales contact are often key lead-generation channels. When using the laser engraving machine industry solution for international presentation, form fields, lead routing and user authorization status should also be included in unified management.
Marketing teams often want to track conversions as comprehensively as possible, but quality control personnel need to control data boundaries. Methods such as server-side analytics, anonymized aggregation and consent mode can balance analysis requirements with user choices, rather than endlessly expanding the scope of data collection in pursuit of attribution accuracy.
How to conduct an actionable compliance acceptance review before launch
The first step of acceptance is to verify the page list. The homepage, product pages, download pages, contact pages, recruitment pages, store checkout pages and landing pages should all provide access to the privacy policy and Cookie settings; advertising-specific pages in particular must not omit compliance access points in pursuit of conversion.
The second step is to verify the script list. Tag managers, analytics tools, advertising pixels, CAPTCHA, maps, videos, online customer service and font services should be listed, with the provider, data type, trigger conditions, purpose and responsible person clearly specified for each tool.
The third step is to simulate user actions. When visitors make no selection, non-essential Cookies must not run; after rejection, core page functions should remain available; corresponding scripts may be triggered only after consent; once users modify their options, system status and page behavior should be updated promptly.
The fourth step is to verify documentation and responsibilities. Companies should retain vendor data processing agreements, cross-border transfer assessment materials, versioned privacy policies, Cookie configuration records and internal handling procedures. In the event of a complaint or security incident, these records are important evidence of ongoing management.
Finally, a review mechanism should also be established. Adding advertising channels, replacing a CRM, installing chat plugins, integrating AI customer service or revising forms may all change data processing activities. It is recommended to review them at least once every six months, while major technical changes should be reassessed before launch.
Conclusion: Make compliance a verifiable operational capability
Privacy policies and Cookie consent in German website development are essentially a reflection of a company’s data governance capabilities on the front end. A truly reliable solution is not a legal text or a pop-up window, but consistency among page functions, script configurations, vendor management and internal processes.
For quality control and security management personnel, the most effective criteria are whether users are given a genuine right to choose, whether the company knows where data goes, whether tracking actually stops after rejection, and whether the relevant records can be clearly demonstrated when needed. When these conditions are met, a website can establish a more solid foundation between growth and trust.
Related Articles
 New SWIFT rules take effect on November 14: payment messages with fully unstructured addresses will be rejected
 1Password Launches Secure Agent Access Feature: 1Password for Agents
 DebugBear confirms service has been restored following a DNS hijacking incident

Related Products
 Yiyingbao SaaS Intelligent Website Building and Marketing SystemYiyingbao SaaS Intelligent Website Building and Marketing System, AI-powered no-code website building, rapid creation of multilingual B2B international websites in 10 minutes, global server acceleration, AI-powered SEO optimization, helping businesses connect efficiently with global markets. The perfect integration of technology and operation makes building an international trade website remarkably simple
 AI+SEM Intelligent Advertising Marketing SystemAI+SEM drives intelligent ad creation, empowering full-funnel precision advertising marketing. The system automatically generates weekly/monthly reports, AI recommends keywords and target countries, monitors core metrics in real-time with intelligent alerts, and enables one-click high-conversion ad solutions to help quickly acquire customers and improve ROI.
 AI+SEO Dual-Engine System Optimization ServicesYiyingbao’s AI+SEO dual-engine optimization system helps foreign trade enterprises acquire high-quality organic traffic through AI-powered keyword research, content generation, and comprehensive technical optimization, significantly improving search rankings and conversion rates.
 AI+SNS Social Media Marketing SystemYingbao AI+SNS Social Media Marketing System - Precision social capture for the social media era. Supports one-click content synchronization across major platforms like Facebook and LinkedIn. AI intelligently rewrites posts for enhanced relevance. 24/7 AI customer service and user profiling analysis empower businesses to efficiently expand into global markets.
 AI+SEO营销解决方案易营宝AI+SEO营销解决方案,通过AI批量写作、智能生成TDK、精准关键词扩词等功能,全面优化网站SEO效果,提升流量与转化率。助力企业构建高效智能网站新生态。
 AI+SEM Advertising Marketing SolutionsAI+SEM Advertising Marketing Solution leverages AI technology to deeply empower SEM ad campaigns. It automatically generates weekly/monthly reports using AI, presenting account data across multiple dimensions for comprehensive insights into campaign performance and trends. The system precisely recommends keywords and target countries, intelligently generates high-conversion ad copy, and enables one-click activation of efficient campaign plans to help businesses rapidly acquire customers. Simultaneously, it monitors core metrics in real time, intelligently identifies abnormal fluctuations, and issues timely alerts to ensure stable, high-return advertising results.
 Domain Name ServicesEasyWin provides professional domain name services, including intelligent queries, one-stop registration, brand protection, and full lifecycle management, helping businesses build a digital brand image.
 EasyOperate B2C Cross-Border E-Commerce Platform & Independent WebsiteEasyStore B2C Cross-border E-commerce Independent Store is an intelligent website building and cross-border e-commerce integrated solution independently developed by EasyStore Information Technology (Beijing) Co., Ltd. The system is specially designed for small and medium-sized as well as large export enterprises, integrating 'website building, operation, marketing, advertising, and conversion' into one, helping enterprises quickly establish cross-border e-commerce independent stores to achieve brand globalization and global sales growth.
The platform supports multiple languages, multiple currencies, and multi-channel marketing, with built-in AI intelligent translation and SEO optimization systems, suitable for mainstream markets such as Southeast Asia, Europe and America, Latin America, and the Middle East, assisting Chinese manufacturing enterprises in efficiently deploying international e-commerce strategies. SSL证书易营宝提供专业SSL安全证书服务,包括单域名和泛域名证书,确保网站数据传输加密、身份验证和完整性保护,助力企业建立安全可信的在线业务环境。









