









- Which customer acquisition channels will be affected by cross-border marketing trends in 2026?Sep 06, 2026View details
- Which homogenization risks should be considered in an analysis of the AI-powered website building industry?Aug 30, 2026View details
- How Will AI Marketing Trends 2026 Change Advertising Budget AllocationAug 28, 2026View details
- Is the EV SSL certificate market shrinking or upgrading? How should companies assess certificate procurement?Aug 11, 2026View details
- Why the old AMP SEO 2020 practices no longer work and what has changed in current optimization prioritiesAug 02, 2026View details
- How to Choose Topics for an Industry News Section to Attract More Organic Search TrafficJul 29, 2026View details
DV vs. EV SSL Certificates: Which One Should Your Corporate Website Choose?
When selecting security options for a corporate website, dv vs ev ssl is not simply a comparison between “low-cost certificates and expensive certificates.” Both can establish HTTPS-encrypted connections, but they differ in validation subject, procurement cycle, applicable business scenarios, and their impact on brand trust. For technical evaluators, the real question is: does the website serve general content access, overseas inquiries, online transactions, or highly sensitive identity and financial operations?
Many teams only address SSL certificates at the last minute before a project goes live, often ending up at one of two extremes: either they purchase an unsuitable EV certificate for presentation purposes, or they deploy only a DV certificate without completing controls for payments, permissions, data transmission, and website security operations. Certificate selection should be assessed within the overall website architecture and business risk context.
First, clarify: DV and EV have no difference in encryption capability
DV (Domain Validation) SSL certificates validate the applicant’s control over a domain name. This is typically completed through DNS records, email verification, or file verification. Once validated, modern TLS encryption protocols can likewise be used between the browser and server to protect login information, form content, inquiry data, and data in transit from being easily stolen.
EV (Extended Validation) SSL certificates, in addition to domain control, conduct more rigorous reviews of the applicant company’s legal registration information, operating status, address, telephone number, and other details. Their focus is not “stronger encryption,” but rather establishing a clearer connection between the website domain and a verified corporate entity.
This is one of the most easily misunderstood points in an evaluation: DV and EV do not have any inherent difference in encryption strength. Connection security also depends on the TLS protocol version, cipher suite configuration, private key protection, certificate renewal, server patches, WAF protection, and vulnerability management of the application itself. Simply purchasing EV cannot replace this foundational work.
Browsers no longer prominently display EV—why should it still be considered?
In the past, some browsers displayed the company name in an EV certificate using a prominent green address bar. Today, mainstream browsers have reduced such visual indicators, and visitors typically see only a lock icon or HTTPS status. In other words, EV should no longer be treated as an “address bar advertising space” with the expectation that it will automatically and significantly improve conversions.
However, this does not mean EV has no value. For financial services, payment platforms, insurance, healthcare, government cooperation projects, brand websites, and B2B platforms involving high-value transactions, rigorous entity validation still has practical significance: it can help buyers, partners, or security review personnel verify the operating entity and provide more complete identity signals for compliance reviews, supply chain access, and brand risk control.
Conversely, if a website is primarily used for product display, content marketing, overseas SEO landing pages, or standard inquiry forms, and user decisions depend more on page content, brand endorsement, response speed, and communication efficiency, DV can often already meet the requirements for HTTPS encryption and basic trusted access.
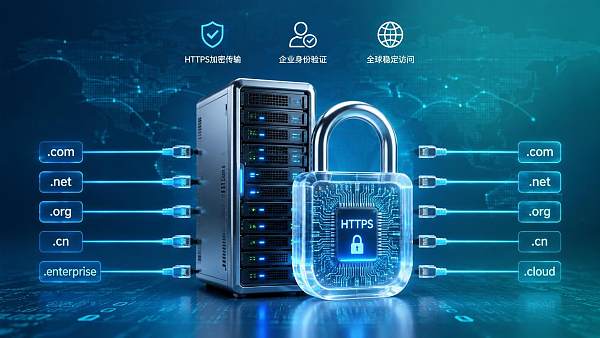
DV vs EV SSL: Start with business scenarios rather than certificate names
For foreign trade manufacturers and global expansion brand teams, the choice is usually more practical: if the main role of the corporate website is to acquire overseas inquiries, showcase factory capabilities, receive Google SEO traffic, and advance subsequent transactions through CRM or email, deploying a DV certificate issued by a trusted CA, together with sitewide HTTPS, form protection, and stable global access capabilities, is usually a reasonable starting point.
If the website directly handles online payments, financial services, distributor account systems, or corporate clients explicitly require strict identity verification of supplier entities, the validation value of EV becomes more prominent. For scenarios between these two, where the company organization’s identity needs to be verified but the highest level of validation is not required, OV (Organization Validation) certificates can also be included in procurement comparisons rather than limiting the choice to DV and EV.
During technical evaluation, do not only ask “which type of certificate to use”
After the certificate type is determined, it is still recommended to review deployment details. First, confirm whether it covers www and non-www domains, business subdomains, and multilingual sites. Multilingual corporate websites often use different country or language paths and may also use separate subdomains; if the certificate coverage does not align with domain planning, browser security warnings can easily occur after launch.
Second, check the certificate auto-renewal and expiration alert mechanisms. Access blocking caused by an expired certificate may seem like a minor issue, but it can directly interrupt leads during peak advertising periods or trade show lead-generation periods. Third, pay attention to the private key storage location, server permission tiers, HSTS configuration, and TLS 1.2/1.3 support. For websites with account systems, HTTPS should also be evaluated together with MFA, login rate limiting, vulnerability scanning, and backup and recovery strategies.
Fourth, avoid assuming that “having a lock means absolute security.” SSL protects the transmission channel, but it cannot identify impersonated content, prevent phishing pages, or fix website application vulnerabilities. Technical teams should continuously inspect third-party scripts, form collection fields, redirect rules, and CDN configurations, especially after integrating ad tracking, online customer service, and overseas marketing tools.
Practical choices for overseas websites: speed, availability, and security must be considered together
In overseas access scenarios, certificate deployment is only the first step. If visitors in North America, Europe, or Southeast Asia frequently experience timeouts when opening the website, it is difficult to establish trust even with EV. Certificate handshakes, CDN nodes, origin server performance, and page resource loading jointly affect the first-visit experience; search engine indexing and user conversion can also be indirectly affected by HTTPS integrity and page stability.
For example, Yingyingbao Foreign Trade Marketing (Super) Website provides global server acceleration, enterprise-grade security protection, and SEO configuration capabilities for website development targeting multilingual and global promotion. For teams that need to maintain sites across multiple regions, mobile pages, and marketing landing pages at the same time, it is more suitable to define a unified management approach for domains, certificates, CDNs, and form data during the website development stage, avoiding site-by-site remediation later.
An actionable decision conclusion
If a corporate website mainly focuses on display, content distribution, SEO lead generation, and standard inquiries, choosing DV SSL issued by a reliable CA and investing the budget in website performance, content quality, form security, and ongoing operations and maintenance is often a solution with a better return on investment.
If the website handles highly sensitive information exchanges, online financial transactions, strict corporate identity verification, or if the industry or client admission rules clearly require higher-level validation, EV SSL should be assessed, and the suitability of OV certificates should be reviewed at the same time where necessary.
The core of dv vs ev ssl is not which is “more advanced,” but which better fits the business risk. For technical evaluators, the most reliable choice is not to look only at the certificate label, but to create a closed loop among identity validation level, domain architecture, global access performance, and security operations capabilities. Only then can deployed HTTPS truly support the long-term operation of a corporate website.
Related Articles
Related Products
 Yiyingbao SaaS Intelligent Website Building and Marketing SystemYiyingbao SaaS Intelligent Website Building and Marketing System, AI-powered no-code website building, rapid creation of multilingual B2B international websites in 10 minutes, global server acceleration, AI-powered SEO optimization, helping businesses connect efficiently with global markets. The perfect integration of technology and operation makes building an international trade website remarkably simple
 AI+SEM Intelligent Advertising Marketing SystemAI+SEM drives intelligent ad creation, empowering full-funnel precision advertising marketing. The system automatically generates weekly/monthly reports, AI recommends keywords and target countries, monitors core metrics in real-time with intelligent alerts, and enables one-click high-conversion ad solutions to help quickly acquire customers and improve ROI.
 AI+SEO Dual-Engine System Optimization ServicesYiyingbao’s AI+SEO dual-engine optimization system helps foreign trade enterprises acquire high-quality organic traffic through AI-powered keyword research, content generation, and comprehensive technical optimization, significantly improving search rankings and conversion rates.
 AI+SNS Social Media Marketing SystemYingbao AI+SNS Social Media Marketing System - Precision social capture for the social media era. Supports one-click content synchronization across major platforms like Facebook and LinkedIn. AI intelligently rewrites posts for enhanced relevance. 24/7 AI customer service and user profiling analysis empower businesses to efficiently expand into global markets.
 AI+SEO营销解决方案易营宝AI+SEO营销解决方案,通过AI批量写作、智能生成TDK、精准关键词扩词等功能,全面优化网站SEO效果,提升流量与转化率。助力企业构建高效智能网站新生态。
 AI+SEM Advertising Marketing SolutionsAI+SEM Advertising Marketing Solution leverages AI technology to deeply empower SEM ad campaigns. It automatically generates weekly/monthly reports using AI, presenting account data across multiple dimensions for comprehensive insights into campaign performance and trends. The system precisely recommends keywords and target countries, intelligently generates high-conversion ad copy, and enables one-click activation of efficient campaign plans to help businesses rapidly acquire customers. Simultaneously, it monitors core metrics in real time, intelligently identifies abnormal fluctuations, and issues timely alerts to ensure stable, high-return advertising results.
 Domain Name ServicesEasyWin provides professional domain name services, including intelligent queries, one-stop registration, brand protection, and full lifecycle management, helping businesses build a digital brand image.
 EasyOperate B2C Cross-Border E-Commerce Platform & Independent WebsiteEasyStore B2C Cross-border E-commerce Independent Store is an intelligent website building and cross-border e-commerce integrated solution independently developed by EasyStore Information Technology (Beijing) Co., Ltd. The system is specially designed for small and medium-sized as well as large export enterprises, integrating 'website building, operation, marketing, advertising, and conversion' into one, helping enterprises quickly establish cross-border e-commerce independent stores to achieve brand globalization and global sales growth.
The platform supports multiple languages, multiple currencies, and multi-channel marketing, with built-in AI intelligent translation and SEO optimization systems, suitable for mainstream markets such as Southeast Asia, Europe and America, Latin America, and the Middle East, assisting Chinese manufacturing enterprises in efficiently deploying international e-commerce strategies. SSL证书易营宝提供专业SSL安全证书服务,包括单域名和泛域名证书,确保网站数据传输加密、身份验证和完整性保护,助力企业建立安全可信的在线业务环境。









