- Amazon Raises Fulfillment Fees Twice, Yet the Median Platform Fee Remains Around 40%Oct 22, 2026View details
- AliExpress and YouTube Partner to Expand Marketing Opportunities for Chinese Brands Going GlobalOct 22, 2026View details
- Publicis says AI marketing is developing at two speeds, with agentic AI helping win clientsOct 21, 2026View details
- Salesforce Plans to Acquire Braze for $5.66 Billion to Enhance AI Marketing CapabilitiesOct 21, 2026View details
- Levanta’s Inaugural China Summit Held in Shenzhen, Focusing on AI and Cross-Border Brand GrowthOct 20, 2026View details
- The October Edition of the 2026 GGE Shenzhen Cross-Border E-Commerce Expo OpensOct 20, 2026View details
Which SSL Certificate Should You Buy for a Multilingual Website Using Subdomains?
If a multilingual website uses same-level subdomains such as en.example.com, de.example.com, and fr.example.com, and more language sites may be added later, a wildcard certificate is usually easier to maintain. Before purchasing, however, confirm that the certificate also includes the apex domain example.com and that the website platform, CDN, or server supports deploying the certificate.
If there are only a few fixed language sites, a multi-domain certificate or separate single-domain certificates can also meet the requirements. The deciding factors are not the number of languages itself, but the full set of hostnames that need protection, the domain levels, and where the HTTPS connection terminates.
List All the Domains That Need Protection
An SSL certificate validates the hostname in the address being accessed, not the page language, website directory, or server IP. Therefore, example.com/en/ and example.com/de/ share the same hostname, so different languages do not require additional certificate coverage; en.example.com and de.example.com are two separate hostnames.
When compiling the domain list, include not only the homepages for each language, but also the apex domain, the www address, and any separate subdomains actually used for the online store, inquiry forms, and other services. Even an address used only for redirects needs a valid certificate: when an HTTPS address is accessed, the browser completes the TLS handshake before receiving the redirect instruction, so a redirect cannot fix a certificate name mismatch.
A Wildcard Covers Only the Specified Level, Not the Entire Domain Tree
*.example.com can match en.example.com, de.example.com, and www.example.com, but it cannot match example.com or shop.en.example.com.
Some wildcard products include the apex domain as well, but this is a domain configuration specified when the certificate is issued, not an inherent feature of wildcard certificates. Check the certificate's Subject Alternative Name (SAN) list rather than relying solely on the word “wildcard” in the product name.
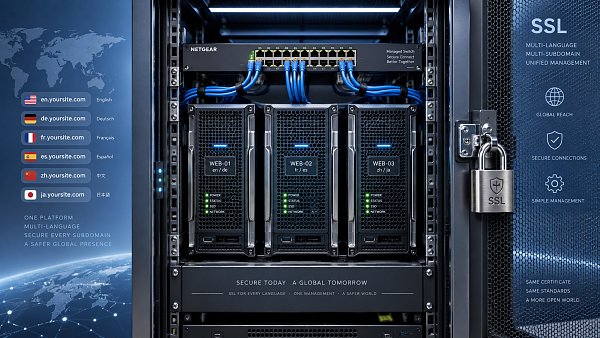
If the website uses en.example.com and the online store uses shop.en.example.com, both domain levels need to be covered. For a small number of fixed store addresses, simply add each full hostname; there is no need to purchase a wildcard certificate for every level.
Are the Language Sites Fixed, or Will More Be Added?
For just a few fixed subdomains, you can add the apex domain, www, and the language subdomains to one multi-domain certificate. It lists the permitted hostnames individually in the SAN, making the coverage clearly defined. However, when adding a language site, you will need to update the domain list, reissue the certificate, and deploy it again.
If language sites will continue to be added and all are under the same domain level, a wildcard certificate requires less maintenance. When adding es.example.com, you do not need to reissue the certificate for that hostname, as long as the DNS, site configuration, and certificate deployment are set up correctly. However, a wildcard certificate does not automatically create subdomains or enable HTTPS for new sites.
If different languages use separate domains such as example.de and example.fr, a single *.example.com certificate cannot cover them. In this case, you can use a multi-domain certificate or issue separate certificates for each site. The choice should take deployment locations and maintenance responsibilities into account, rather than simply aiming to minimize the number of certificates.
Before Purchasing, Check Whether the Platform Already Provides a Certificate
A hosted website platform or CDN may already support automatic certificate issuance and renewal. If the service covers all language subdomains, purchasing an additional certificate may not be necessary; some platforms also do not allow you to upload certificates purchased independently. First confirm which domains are supported, whether wildcard certificates are supported, and whether certificate services are included in your current plan.
When using a CDN, distinguish between the connection from the browser to the CDN and the connection from the CDN to the origin server. A valid certificate at the CDN edge does not mean the origin server's certificate is also configured correctly. The certificate used by the origin server must meet the CDN's encryption and certificate validation requirements. An origin certificate intended only for CDN-to-origin connections cannot be used directly as a public certificate trusted by browsers.
If language sites are hosted on different servers, sharing a wildcard certificate means distributing the associated private key. A private key leak in one place could affect other sites using the same key. For sites managed by different teams or service providers, separate certificates help isolate risk and reduce the coordination required for renewals across teams.
Do Not Confuse Validation Level with Coverage
DV, OV, and EV refer to validation methods, while single-domain, multi-domain, and wildcard describe domain coverage. These are two different dimensions. Purchasing an OV certificate does not automatically increase the number of language subdomains that can be protected; with the same TLS configuration, encryption strength cannot be determined solely by the validation level.
If the only goal is to enable HTTPS for language sites, a DV certificate trusted by browsers and matching the domain names can meet basic needs. Whether to use OV or EV should depend on corporate identity verification, contractual, or internal management requirements—not on an assumption that a website targeting overseas markets must have a higher validation level.
Free certificates can also meet HTTPS requirements, but a reliable renewal mechanism is essential. For example, Let's Encrypt requires DNS validation for wildcard certificates. To automate renewals, confirm that the DNS service supports the required automation and properly restrict permissions for DNS API credentials.
Check Each Address During Launch Acceptance
Before ordering a certificate or enabling one provided by the platform, confirm the actual hostname list, SAN coverage, deployment location, and renewal responsibilities. It is not enough to confirm that “SSL is supported” without clarifying who will handle issuance failures, expiration alerts, and redeployment.
After launch, visit the apex domain, www, and each language subdomain individually. Check hostname matching, the certificate chain, and HTTPS redirects, and also look for resources on the pages that are still loaded over HTTP. The absence of certificate warnings does not mean that the page has been fully and securely loaded over HTTPS.
For a structure consisting of an apex domain and same-level language subdomains, a wildcard certificate that includes the apex domain is an option that makes expansion easier. For a small number of fixed sites or sites hosted in separate locations, a multi-domain certificate or separate certificates may be more suitable. Purchase a certificate only after confirming the domain list and deployment requirements, rather than buying one first and then changing the website to fit it.
Related Articles
 How Can You Prevent a Video News Module from Slowing Down Page Loading?
 When choosing a website development company in Xiamen, how should you agree on source code delivery?
 How can you identify what to optimize when the first screen of your B2B website loads slowly?
Related Products
 Yiyingbao SaaS Intelligent Website Building and Marketing SystemYiyingbao SaaS Intelligent Website Building and Marketing System, AI-powered no-code website building, rapid creation of multilingual B2B international websites in 10 minutes, global server acceleration, AI-powered SEO optimization, helping businesses connect efficiently with global markets. The perfect integration of technology and operation makes building an international trade website remarkably simple
 AI+SEM Intelligent Advertising Marketing SystemAI+SEM drives intelligent ad creation, empowering full-funnel precision advertising marketing. The system automatically generates weekly/monthly reports, AI recommends keywords and target countries, monitors core metrics in real-time with intelligent alerts, and enables one-click high-conversion ad solutions to help quickly acquire customers and improve ROI.
 AI+SEO Dual-Engine System Optimization ServicesYiyingbao’s AI+SEO dual-engine optimization system helps foreign trade enterprises acquire high-quality organic traffic through AI-powered keyword research, content generation, and comprehensive technical optimization, significantly improving search rankings and conversion rates.
 AI+SNS Social Media Marketing SystemYingbao AI+SNS Social Media Marketing System - Precision social capture for the social media era. Supports one-click content synchronization across major platforms like Facebook and LinkedIn. AI intelligently rewrites posts for enhanced relevance. 24/7 AI customer service and user profiling analysis empower businesses to efficiently expand into global markets.
 AI+SEO营销解决方案易营宝AI+SEO营销解决方案,通过AI批量写作、智能生成TDK、精准关键词扩词等功能,全面优化网站SEO效果,提升流量与转化率。助力企业构建高效智能网站新生态。
 AI+SEM Advertising Marketing SolutionsAI+SEM Advertising Marketing Solution leverages AI technology to deeply empower SEM ad campaigns. It automatically generates weekly/monthly reports using AI, presenting account data across multiple dimensions for comprehensive insights into campaign performance and trends. The system precisely recommends keywords and target countries, intelligently generates high-conversion ad copy, and enables one-click activation of efficient campaign plans to help businesses rapidly acquire customers. Simultaneously, it monitors core metrics in real time, intelligently identifies abnormal fluctuations, and issues timely alerts to ensure stable, high-return advertising results.
 Domain Name ServicesEasyWin provides professional domain name services, including intelligent queries, one-stop registration, brand protection, and full lifecycle management, helping businesses build a digital brand image.
 EasyOperate B2C Cross-Border E-Commerce Platform & Independent WebsiteEasyStore B2C Cross-border E-commerce Independent Store is an intelligent website building and cross-border e-commerce integrated solution independently developed by EasyStore Information Technology (Beijing) Co., Ltd. The system is specially designed for small and medium-sized as well as large export enterprises, integrating 'website building, operation, marketing, advertising, and conversion' into one, helping enterprises quickly establish cross-border e-commerce independent stores to achieve brand globalization and global sales growth.
The platform supports multiple languages, multiple currencies, and multi-channel marketing, with built-in AI intelligent translation and SEO optimization systems, suitable for mainstream markets such as Southeast Asia, Europe and America, Latin America, and the Middle East, assisting Chinese manufacturing enterprises in efficiently deploying international e-commerce strategies. SSL证书易营宝提供专业SSL安全证书服务,包括单域名和泛域名证书,确保网站数据传输加密、身份验证和完整性保护,助力企业建立安全可信的在线业务环境。