- Hengqin Cooperation Zone Shares Cross-Border E-Commerce Developments, Focusing on Macao-Hengqin Collaboration and International MarketsOct 24, 2026View details
- A Shenyang study highlights the development of the “cross-border e-commerce + industrial cluster” modelOct 24, 2026View details
- Three China Advertising Association GEO group standards take effect on October 23Oct 24, 2026View details
- Amazon Raises Fulfillment Fees Twice, Yet the Median Platform Fee Remains Around 40%Oct 22, 2026View details
- AliExpress and YouTube Partner to Expand Marketing Opportunities for Chinese Brands Going GlobalOct 22, 2026View details
- Publicis says AI marketing is developing at two speeds, with agentic AI helping win clientsOct 21, 2026View details
Ads stopped running because the website certificate expired. How can you resume them?
When a website certificate expires, ads may stop running. To resume advertising, three things need to be done: restore secure HTTPS access to the ad landing page, confirm that the advertising platform can crawl the page, and then address the review status of affected ads. Renewing the certificate is only the first step. Even after the website is back online, ads that have already been disapproved may still need to be submitted for review.
First, check the specific notice in the advertising account. If it reports an issue with the landing page, such as “Destination URL not reachable,” you can follow the steps below. If the issue involves account suspension, payment problems, or other policy matters, fixing the certificate alone will not resolve it. Businesses generating overseas trade inquiries or orders through their own websites should first pause ads that still direct traffic to the affected pages, and record the affected ads, URLs, and reasons for pausing them so they can be restored one by one.
First, fix the certificate actually serving your website
Copy the full landing page URL entered in the advertising account into a browser, then check the certificate’s validity period, covered domains, and the page’s redirect path. Don’t check only the website homepage: an ad may point to a www domain, a dedicated subdomain, a multilingual page, or a URL that redirects through a tracking link. Every HTTPS step can affect access.
When renewing the certificate, confirm that the new certificate has been deployed to the location actually handling incoming traffic. A website may use a server, CDN, load balancer, or website-building platform at the same time. A “renewal successful” message in the control panel does not mean that every entry point has been updated. If the browser still shows the old expiration date, continue checking certificate deployment, active configuration, and relevant nodes. Do not proceed directly to ad review.
- Self-managed server: Check that the new certificate, corresponding private key, and full certificate chain are configured correctly, and reload the service as required.
- CDN: Check both the certificate on the edge nodes that visitors connect to and the certificate used by the CDN to connect to the origin server.
- SaaS website-building platform: Confirm the certificate status for the bound domain, the automatic renewal result, and HTTPS access status. If the platform needs to intervene, provide the specific URL with the issue.
If the new certificate is within its validity period but access still fails, also check for issues such as a domain mismatch or a missing certificate chain. These problems can also prevent the advertising platform from accessing the landing page. Do not switch to HTTP or ask visitors to ignore browser warnings to resume sending traffic; this creates access and conversion risks.
After the page opens, check the full path users take from the ad
A successful visit in a local browser only confirms that one access attempt worked. For websites targeting overseas markets, check the ad URL from networks in the target markets, especially for sites using a CDN, regional access restrictions, or security rules.
During the check, follow the full path: “ad link—redirect URL—final landing page—submission or purchase entry point.” A certificate issue may affect only one subdomain or may occur at an intermediate redirect URL. If the homepage works but a product page does not, or the page loads but an inquiry cannot be submitted, resuming ads will not serve its intended purpose.
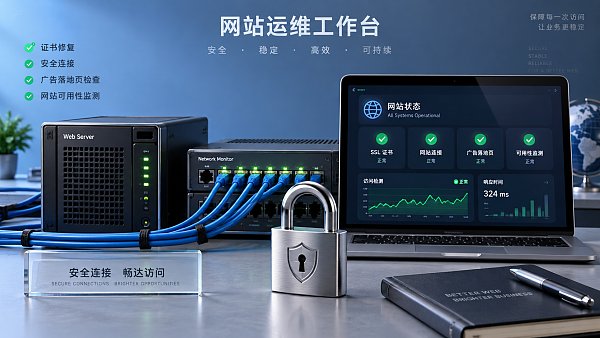
At a minimum, confirm the following:
- The complete ad URL is accessible and redirects to the expected page, with no redirect loops or error pages.
- Certificates are valid and match the domains at every HTTPS step, and the page’s main resources load correctly.
- Access from the target region is not blocked by a firewall, CAPTCHA, or regional restriction, and security rules are not mistakenly blocking ad review crawlers.
- Inquiry forms on B2B websites can be submitted, and the shopping cart and checkout process on B2C websites can be completed.
- Conversion tags are triggered. Where necessary, cross-check against lead or order records in the relevant systems rather than relying only on a “submission successful” message on the page.
If results still vary by region, resolve node or access-rule issues first. Clearing the browser cache can help with diagnosis, but it cannot replace checking access from external networks. If the advertising platform encounters any entry point that still has an issue when it crawls the site again, the ads may be disapproved again.
Request a review based on the ad status; there is no need to rush into rebuilding ads
After checking the website, return to the advertising account and review the affected items. An expired certificate may have caused some ads to be disapproved, affected links in the ad creative, or simply led the media buyer to pause ads manually to limit losses. The appropriate action depends on the status and reason shown in the account.
For platforms such as Google Ads and Meta, check the available actions in the relevant ad or issue-resolution section. If the destination URL issue has been fixed, follow the on-screen instructions to request a review or have the ad reviewed again. If the ad was only paused manually, confirm that the page is back online and the ad is eligible before reactivating it. Platform interfaces and review processes may change, so avoid relying on a fixed sequence of button clicks.
When submitting a review request, briefly explain which domain was affected, that the certificate has been updated, that the landing page is accessible again, and that redirects and forms have been checked. If the platform allows supporting materials, attach relevant evidence. Do not repeatedly create identical ads or frequently change URLs to see what works. This makes troubleshooting more difficult and does not guarantee that the original issue will be bypassed.
There is no single guaranteed review timeframe. If an ad is disapproved again during the review period, check the new reason and consult server access logs to see whether the crawler still encountered connection failures, error responses, or blocks. If the account shows that the ad is eligible but it receives no traffic, check the budget, bids, schedule, account balance, and other delivery restrictions.
Before restoring the budget, make sure you can handle the inquiries and orders
Once the ads are eligible to run again, start with a manageable budget and monitor traffic and conversions before returning to the previous pace. Focus on whether the landing page is stable in the target regions, inquiries are reaching the relevant system or inbox, orders are being recorded correctly, and conversion tracking matches business outcomes. Data from the period when the certificate was unavailable may be incomplete, so avoid making major bid adjustments based only on the conversion rate on the day service is restored.
This type of issue also exposes gaps in responsibility between website management and ad operations: who manages the domain and certificate, who receives expiration reminders, who verifies the ad pages, and who submits review requests should all be clearly assigned. An integrated service can shorten the resolution process, but the scope of checks still needs to be agreed on and should cover the main domain, ad subdomains, CDN, and actual conversion entry points.
Ongoing safeguards should include expiration reminders, alerts for automatic renewal failures, and external HTTPS availability monitoring. After the next renewal, acceptance should be based on real access results: the ad link is securely accessible, users in the target markets can open it, and the inquiry or purchase process can be completed.
Related Articles
 How Can You Exclude Existing Customers from Facebook Ad Retargeting?
 How can you evaluate a landing page agency's conversion tracking capabilities?
 How much does it cost to run Google paid ads in Japan?
Related Products
 Yiyingbao SaaS Intelligent Website Building and Marketing SystemYiyingbao SaaS Intelligent Website Building and Marketing System, AI-powered no-code website building, rapid creation of multilingual B2B international websites in 10 minutes, global server acceleration, AI-powered SEO optimization, helping businesses connect efficiently with global markets. The perfect integration of technology and operation makes building an international trade website remarkably simple
 AI+SEM Intelligent Advertising Marketing SystemAI+SEM drives intelligent ad creation, empowering full-funnel precision advertising marketing. The system automatically generates weekly/monthly reports, AI recommends keywords and target countries, monitors core metrics in real-time with intelligent alerts, and enables one-click high-conversion ad solutions to help quickly acquire customers and improve ROI.
 AI+SEO Dual-Engine System Optimization ServicesYiyingbao’s AI+SEO dual-engine optimization system helps foreign trade enterprises acquire high-quality organic traffic through AI-powered keyword research, content generation, and comprehensive technical optimization, significantly improving search rankings and conversion rates.
 AI+SNS Social Media Marketing SystemYingbao AI+SNS Social Media Marketing System - Precision social capture for the social media era. Supports one-click content synchronization across major platforms like Facebook and LinkedIn. AI intelligently rewrites posts for enhanced relevance. 24/7 AI customer service and user profiling analysis empower businesses to efficiently expand into global markets.
 AI+SEO营销解决方案易营宝AI+SEO营销解决方案,通过AI批量写作、智能生成TDK、精准关键词扩词等功能,全面优化网站SEO效果,提升流量与转化率。助力企业构建高效智能网站新生态。
 AI+SEM Advertising Marketing SolutionsAI+SEM Advertising Marketing Solution leverages AI technology to deeply empower SEM ad campaigns. It automatically generates weekly/monthly reports using AI, presenting account data across multiple dimensions for comprehensive insights into campaign performance and trends. The system precisely recommends keywords and target countries, intelligently generates high-conversion ad copy, and enables one-click activation of efficient campaign plans to help businesses rapidly acquire customers. Simultaneously, it monitors core metrics in real time, intelligently identifies abnormal fluctuations, and issues timely alerts to ensure stable, high-return advertising results.
 Domain Name ServicesEasyWin provides professional domain name services, including intelligent queries, one-stop registration, brand protection, and full lifecycle management, helping businesses build a digital brand image.
 EasyOperate B2C Cross-Border E-Commerce Platform & Independent WebsiteEasyStore B2C Cross-border E-commerce Independent Store is an intelligent website building and cross-border e-commerce integrated solution independently developed by EasyStore Information Technology (Beijing) Co., Ltd. The system is specially designed for small and medium-sized as well as large export enterprises, integrating 'website building, operation, marketing, advertising, and conversion' into one, helping enterprises quickly establish cross-border e-commerce independent stores to achieve brand globalization and global sales growth.
The platform supports multiple languages, multiple currencies, and multi-channel marketing, with built-in AI intelligent translation and SEO optimization systems, suitable for mainstream markets such as Southeast Asia, Europe and America, Latin America, and the Middle East, assisting Chinese manufacturing enterprises in efficiently deploying international e-commerce strategies. SSL证书易营宝提供专业SSL安全证书服务,包括单域名和泛域名证书,确保网站数据传输加密、身份验证和完整性保护,助力企业建立安全可信的在线业务环境。