

- Which customer acquisition channels will be affected by cross-border marketing trends in 2026?Sep 06, 2026View details
- Which homogenization risks should be considered in an analysis of the AI-powered website building industry?Aug 30, 2026View details
- How Will AI Marketing Trends 2026 Change Advertising Budget AllocationAug 28, 2026View details
- Is the EV SSL certificate market shrinking or upgrading? How should companies assess certificate procurement?Aug 11, 2026View details
- Why the old AMP SEO 2020 practices no longer work and what has changed in current optimization prioritiesAug 02, 2026View details
- How to Choose Topics for an Industry News Section to Attract More Organic Search TrafficJul 29, 2026View details
Germany’s New Audit Guidelines Include Independent Website SDK Disclosure in Supplier Qualification
A new audit criterion is sending a clear signal regarding digital compliance requirements within Germany’s industrial procurement chain. The timing of the event has not been clearly specified in the existing materials. What has been confirmed is that on August 5, 2026, TÜV Rheinland released the new 《B2B Digital Platform Data Sovereignty Audit Guidelines 2026》, incorporating the scope of data collection, cross-border transfer routes, and user authorization mechanisms of third-party SDKs on independent websites into the qualification assessment of B2B suppliers. At the same time, the guidelines have been listed by VDMA as a prerequisite for qualified supplier admission in the second half of 2026. This means that Chinese suppliers serving Germany’s industrial procurement system may subsequently need to provide not only information on products, delivery, and quality requirements, but also clearer disclosures and explanations regarding data processing on their websites.
Confirmed Regulatory Changes
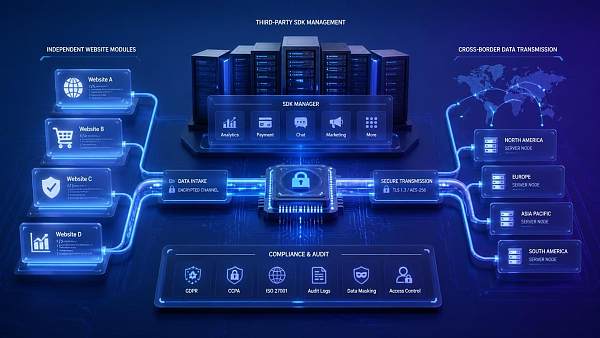
According to the available information, TÜV Rheinland released the 《B2B Digital Platform Data Sovereignty Audit Guidelines 2026》 on August 5, 2026. For the first time, the guidelines incorporate the processing of third-party SDKs on B2B independent websites into supplier qualification assessments, covering the scope of data collection, cross-border transfer routes, and user authorization mechanisms.
The existing materials also indicate that the third-party SDKs within the scope of attention include example tools such as Facebook Pixel, Hotjar, and CNZZ. Another confirmed change is that the German industrial procurement association VDMA has listed these guidelines as a prerequisite for qualified supplier admission in the second half of 2026. Apart from the information above, the input materials do not provide more detailed implementation criteria, review procedures, or supporting document details.
Beyond Procurement Admission, the Impact Extends Beyond Website Operations
Export Suppliers Seeking Customers in the German Market
Based on the analysis, these companies are likely to be affected most directly because their independent websites have already entered the scope of supplier qualification assessments. The impact is not limited to whether marketing pages operate normally; it also concerns whether companies can explain what data third-party SDKs collect, how the data flows, whether cross-border transfers are involved, and how user authorization mechanisms are configured. The main areas requiring attention are the preparation of supplier admission materials, information disclosure before customer factory audits, and consistency in external compliance statements.
Procurement and Supplier Management Processes
From an industry perspective, procurement departments and supplier management teams will also be affected. Since the guidelines have been listed as a prerequisite for qualified supplier admission, website data processing statements may become a new item for review during subsequent procurement screening, supplier prequalification, and qualification rechecks. For the relevant business processes, greater attention should be paid to whether tender documents, supplier questionnaires, prequalification checklists, or qualification attachments begin to include additional requirements concerning third-party SDKs, data flows, and authorization mechanisms.
Certification, Testing, and Compliance Service Partners
It appears that certification-related companies, testing service providers, and compliance consultants supporting supplier admission may also need to adjust their work. The reason is that audit preparation, which previously focused more on products, systems, or delivery capabilities, may need to include website-side data explanations, third-party tool lists, and an analysis of authorization logic. The impact is mainly reflected in audit consulting, document organization, and customer response support, rather than in isolated technical remediation itself.
Website Operations and Delivery Support Teams
For service teams responsible for independent website development, advertising tracking, user analytics, and technical integrations, the changes are concentrated in the scope of delivery responsibilities. SDK deployment methods that previously emphasized functional implementation and marketing conversion may subsequently need to address customer inquiries regarding the scope of data collection, transfer routes, and authorization mechanisms. The focus should not be placed solely on the names of individual tools, but on whether website-side technical integration documentation, version management, page disclosures, and cooperation with customer audits can be maintained in consistent records.
Which Practical Steps Should Be Prepared Now?
First, Review the Third-Party SDK List and Data Collection Scope
Based on the analysis, companies should first identify which third-party SDKs are actually integrated into their independent websites and what data collection activities each one involves. Since the available information explicitly refers to the scope of data collection, this area is more likely to serve as basic documentation for subsequent audits. If a company currently lacks a unified register of third-party code, analytics tools, and marketing tracking components used on its website, it may be placed in a relatively passive position during future qualification assessments or customer inquiries.
Pay Attention to the Ability to Explain Cross-Border Transfer Routes
From a practical perspective, the input materials explicitly mention cross-border transfer routes, so companies should focus on whether they can clearly explain the relevant routes. This should be understood more as an issue of documentation preparation and compliance explanation capabilities, rather than as a basis for directly deriving a uniform remediation conclusion. At this stage, companies should continue monitoring whether more specific review templates, attachment requirements, or wording standards are introduced.
Check Website Authorization Mechanisms and External Disclosures
The inclusion of user authorization mechanisms in the assessment means that companies cannot focus only on back-end deployment; they must also examine whether the authorization and disclosure arrangements on front-end pages match their actual data processing activities. At present, greater attention should be paid to whether website statements, pop-up mechanisms, privacy-related pages, and the actual SDK operating logic are consistent, and whether these elements can be clearly explained during supplier audits.
Incorporate Admission Requirements into Procurement Schedules and Customer Communications
As the guidelines have been listed as a prerequisite for qualified supplier admission in the second half of 2026, companies need to monitor their potential impact on project timelines. In particular, during supplier registration, qualification updates, customer prequalification, and tender coordination, it is worth continuing to observe whether website-side compliance materials will become a prerequisite for review. The available information is not yet sufficient to demonstrate that uniform implementation results have been established, so it is more appropriate to prepare in advance rather than make excessive projections based on a single judgment.
This Looks More Like an Implementation Signal Than a Simple Information Update
From the editor’s perspective, the key significance of this news is not the addition of an abstract data compliance concept, but the fact that third-party SDK management on independent websites has been placed within the context of supplier qualification assessments and directly linked to qualified supplier admission. For the industry, this is closer to an implementation signal than a general initiative or statement of principles.
At the same time, appropriate boundaries must be maintained. The existing materials do not provide more detailed audit standards, determination methods, exemption conditions, or remediation periods. Therefore, it is not yet appropriate to interpret the development as meaning that all companies will face exactly the same implementation approach. A more reasonable assessment is that the direction of the rules has become clear, while the specific implementation criteria, document details, and market feedback still require continued observation.
How Should the Industry Implications of This News Be Understood?
Overall, this change reflects the fact that when conducting international business within industrial procurement systems, supplier assessments are extending beyond traditional product, quality, and delivery capabilities to include the transparency of data processing at companies’ digital touchpoints. Its practical significance does not lie in immediately reaching a uniform conclusion, but in reminding relevant companies that the deployment of third-party SDKs on independent websites may already affect supplier admission, procurement coordination, and qualification review communications.
At present, it is more appropriate to understand this news as an admission signal that has entered the implementation stage while still requiring substantial follow-up observation. Companies should assess it rationally, neither exaggerating its impact nor overlooking its practical influence on supplier qualification preparation.
Basis of This Article and Key Areas for Further Verification
This article was generated based on the news title, event timing, and event summary provided by the user. The known information includes the release by TÜV Rheinland of the new 《B2B Digital Platform Data Sovereignty Audit Guidelines 2026》, the inclusion of data processing activities related to third-party SDKs in B2B supplier qualification assessments, and the listing of these guidelines by VDMA as a prerequisite for qualified supplier admission in the second half of 2026. No specific official source link was provided in the input, so the relevant original documents, announcement texts, and formal implementation explanations still require continued verification.
For events of this type, subsequent cross-checking would normally need to combine official announcements, industry association information, documents from standards organizations, information from regulatory or trade authorities, and reports from authoritative media. The areas that still require close observation include whether certification implementation criteria become more specific, whether tender documents or supplier questionnaires are adjusted, whether industry feedback becomes differentiated, and whether disclosure and cooperation requirements for companies during actual implementation become clearer.
Related Articles
Related Products
 Yiyingbao SaaS Intelligent Website Building and Marketing SystemYiyingbao SaaS Intelligent Website Building and Marketing System, AI-powered no-code website building, rapid creation of multilingual B2B international websites in 10 minutes, global server acceleration, AI-powered SEO optimization, helping businesses connect efficiently with global markets. The perfect integration of technology and operation makes building an international trade website remarkably simple
 AI+SEM Intelligent Advertising Marketing SystemAI+SEM drives intelligent ad creation, empowering full-funnel precision advertising marketing. The system automatically generates weekly/monthly reports, AI recommends keywords and target countries, monitors core metrics in real-time with intelligent alerts, and enables one-click high-conversion ad solutions to help quickly acquire customers and improve ROI.
 AI+SEO Dual-Engine System Optimization ServicesYiyingbao’s AI+SEO dual-engine optimization system helps foreign trade enterprises acquire high-quality organic traffic through AI-powered keyword research, content generation, and comprehensive technical optimization, significantly improving search rankings and conversion rates.
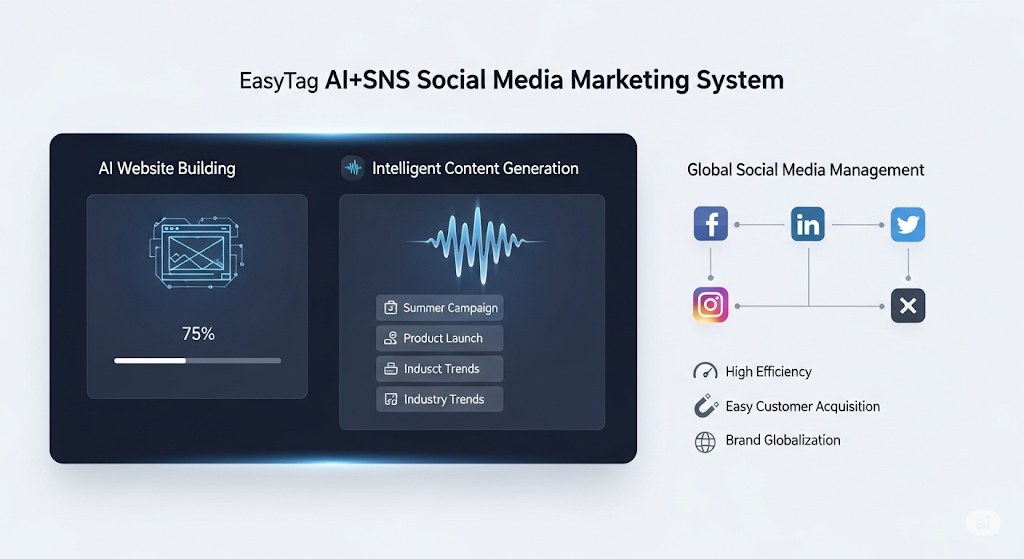
 AI+SNS Social Media Marketing SystemYingbao AI+SNS Social Media Marketing System - Precision social capture for the social media era. Supports one-click content synchronization across major platforms like Facebook and LinkedIn. AI intelligently rewrites posts for enhanced relevance. 24/7 AI customer service and user profiling analysis empower businesses to efficiently expand into global markets.
 AI+SEO营销解决方案易营宝AI+SEO营销解决方案,通过AI批量写作、智能生成TDK、精准关键词扩词等功能,全面优化网站SEO效果,提升流量与转化率。助力企业构建高效智能网站新生态。
 AI+SEM Advertising Marketing SolutionsAI+SEM Advertising Marketing Solution leverages AI technology to deeply empower SEM ad campaigns. It automatically generates weekly/monthly reports using AI, presenting account data across multiple dimensions for comprehensive insights into campaign performance and trends. The system precisely recommends keywords and target countries, intelligently generates high-conversion ad copy, and enables one-click activation of efficient campaign plans to help businesses rapidly acquire customers. Simultaneously, it monitors core metrics in real time, intelligently identifies abnormal fluctuations, and issues timely alerts to ensure stable, high-return advertising results.
 Domain Name ServicesEasyWin provides professional domain name services, including intelligent queries, one-stop registration, brand protection, and full lifecycle management, helping businesses build a digital brand image.
 EasyOperate B2C Cross-Border E-Commerce Platform & Independent WebsiteEasyStore B2C Cross-border E-commerce Independent Store is an intelligent website building and cross-border e-commerce integrated solution independently developed by EasyStore Information Technology (Beijing) Co., Ltd. The system is specially designed for small and medium-sized as well as large export enterprises, integrating 'website building, operation, marketing, advertising, and conversion' into one, helping enterprises quickly establish cross-border e-commerce independent stores to achieve brand globalization and global sales growth.
The platform supports multiple languages, multiple currencies, and multi-channel marketing, with built-in AI intelligent translation and SEO optimization systems, suitable for mainstream markets such as Southeast Asia, Europe and America, Latin America, and the Middle East, assisting Chinese manufacturing enterprises in efficiently deploying international e-commerce strategies. SSL证书易营宝提供专业SSL安全证书服务,包括单域名和泛域名证书,确保网站数据传输加密、身份验证和完整性保护,助力企业建立安全可信的在线业务环境。