- Amazon Raises Fulfillment Fees Twice, Yet the Median Platform Fee Remains Around 40%Oct 22, 2026View details
- AliExpress and YouTube Partner to Expand Marketing Opportunities for Chinese Brands Going GlobalOct 22, 2026View details
- Publicis says AI marketing is developing at two speeds, with agentic AI helping win clientsOct 21, 2026View details
- Salesforce Plans to Acquire Braze for $5.66 Billion to Enhance AI Marketing CapabilitiesOct 21, 2026View details
- Levanta’s Inaugural China Summit Held in Shenzhen, Focusing on AI and Cross-Border Brand GrowthOct 20, 2026View details
- The October Edition of the 2026 GGE Shenzhen Cross-Border E-Commerce Expo OpensOct 20, 2026View details
How Can You Prevent Duplicate Charges on Orders After Integrating Payments into a Cross-Border E-Commerce Platform?
After a buyer clicks to pay, the page keeps spinning. They refresh and try again, but the backend shows two successful transactions. In cross-border e-commerce platform payment integration, this kind of issue is often not caused by a faulty payment button, but by a lack of consistent controls for network timeouts, concurrent requests, and asynchronous notifications. Preventing duplicate charges requires idempotent payment requests, deduplication of callbacks, order status checks, and exception reconciliation—not just limiting clicks on the frontend.
First, distinguish duplicate notifications from two actual charges
Receiving the same payment success event multiple times from a gateway does not mean the buyer was charged more than once. Technical troubleshooting should distinguish among three situations: duplicate callbacks for the same transaction, multiple payment sessions created for the same order, and separate transaction IDs that each completed a funds capture. These require different handling.
You also need to distinguish pre-authorizations from actual charges. Some bank cards may first show a hold on funds, with the charge completed later; a screenshot of the buyer’s statement alone is not enough to determine that a duplicate payment occurred. Verify the payment service provider’s transaction ID, authorization and capture statuses, amount, currency, and settlement records. When evaluating a system, also clarify whether duplicate prevention covers payment creation, authorization, or final capture, so that only one of these interfaces is not protected.
Payment integration for cross-border e-commerce platforms: an idempotency key must correspond to the same business operation
A payment API timeout only means the platform did not receive a result in time; it does not prove that the gateway did not accept the request. If the program generates a new request identifier for every retry, the gateway may treat each request as a separate, valid payment.
A more reliable approach is to first save a payment attempt record to the database, then call the gateway, binding a stable idempotency key to that business operation. The same key should be reused after a connection interruption, page refresh, or task retry; parameters such as the amount and currency must also remain unchanged. Gateways differ in the scope and retention period of idempotency keys and in how they handle conflicting parameters, so check each API specification carefully.
- Order number: Identifies the buyer-seller transaction and should not be treated as equivalent to a single payment request.
- Payment attempt ID: Records one traceable payment process and links the channel, amount, currency, and gateway transaction ID.
- Operation idempotency key: Design separate keys for operations such as creation, capture, and refund; do not reuse the same key across different operations.
When the status of a previous payment is unknown, do not simply use a new key and charge again. Allow a new payment attempt only after confirming that the previous one failed, was canceled, or its session expired. For requests that have exceeded the gateway’s idempotency retention period, do not blindly replay them; first query the original transaction.
Controlling concurrent requests matters more than disabling the button
Disabling a button can reduce accidental actions, but it cannot prevent duplicate submissions from multiple tabs, repeated submissions on mobile devices, or direct API calls. The backend needs database constraints for key safeguards, such as unique payment attempt IDs, unique channel transaction IDs within the relevant merchant account, and rules preventing multiple active payment attempts from being created for the same order without control.
Before creating a payment, check within a transaction whether the order has already been paid and whether the amount has changed. Use row locks, version numbers, or conditional updates to control concurrent requests. Distributed locks can help control traffic, but cannot replace database constraints; persistent records are still needed as a fallback if a lock expires or a process crashes.
A recommended flow is: validate the order and create a payment attempt → call the gateway → save the response → wait for a notification or actively query for the result → conditionally update the order. External payment calls should generally not hold a database transaction open for a long time.
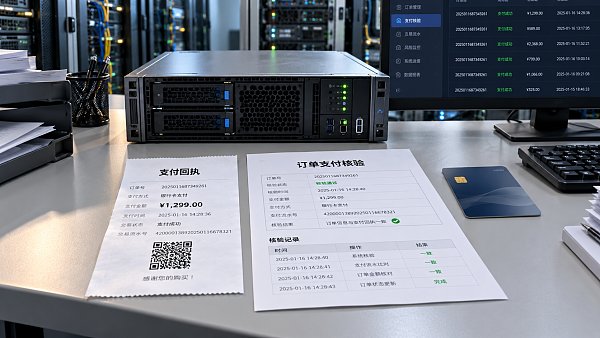
It is best to maintain separate statuses for orders and payment attempts. An order can remain pending payment while its payment attempt is processing or awaiting confirmation; do not mark it as failed just because an API call timed out. If an order allows split payments, validate against the total amount received and confirmed rather than simply limiting an order to “one transaction only.”
Callback handling should allow repeated receipt but take effect only once
Payment notifications may be duplicated, delayed, or arrive out of order. The receiving endpoint should first verify the signature according to the gateway’s rules, then check the merchant account, order association, amount, and currency. Do not proceed just because a “success” field is present, and never trust a success page to which the browser redirects.
Next, persist the event and enforce uniqueness using the channel event ID. If there is no stable event ID, design a deduplication identifier according to the channel’s specifications. Also validate against the transaction ID and business status to prevent multiple events describing the same charge from taking effect more than once. Trigger downstream business processes only after a conditional update has completed the status transition.
Where possible, commit the event deduplication record, order update, and pending business event in the same transaction, then use a reliable messaging mechanism to drive inventory updates, shipping, and notifications. Downstream consumers should also be idempotent to avoid “no duplicate charge, but duplicate shipment.” Before acknowledging receipt to the gateway, ensure the event has been reliably saved; if processing temporarily fails, retry as permitted by the protocol.
Timeouts, channel switching, and late success require separate handling
Cross-border payments may involve verification codes, redirects, and local payment methods, so results can arrive later than the frontend’s waiting period. The page should display “Confirming payment result” and provide a way to check the status, rather than immediately prompting the buyer to pay again. The backend should reconcile the status through active queries and compensation tasks, with query frequency kept within the channel’s limits.
When a buyer switches payment channels, close the old session where possible and make clear whether closing it actually prevents a subsequent charge. If an old transaction succeeds late and the new transaction has also succeeded, retain all transaction records, identify the overpayment, and send it for manual review or a controlled refund process. Refunds also need idempotency, and their settlement results must be tracked; “refund submitted” does not mean “funds returned.”
Technical acceptance testing should focus on behavior after failures
When evaluating a cross-border e-commerce payment solution, ask for demonstrations of the following scenarios, not just one successful payment:
- The gateway accepts a request, but the API times out. After a retry, is the request still associated with the original transaction?
- Two pages attempt payment at the same time. Can this result in uncontrolled duplicate payment attempts?
- A success notification arrives more than once or out of order. Is the payment recorded and the order shipped only once?
- The service crashes after the charge but before saving it to the database. Can the status be recovered through queries and reconciliation?
- An old transaction succeeds late after the buyer switches channels. Can the system identify and handle the overpayment?
For platforms such as Yiyingbao that provide an integrated website-building and overseas marketing service, payment acceptance testing should cover the full chain from e-commerce orders to channel transactions and after-sales handling, rather than stopping at “payment connected.” The key technical questions are whether requests can be safely retried, statuses can be tracked, and exceptions can be compensated for. Putting these rules into database constraints, API protocols, and acceptance tests can reduce the risk of duplicate charges and help buyers feel less anxious while waiting for payment confirmation.
Related Articles
 How Can You Prevent Duplicate Charges on Orders After Integrating Payments into a Cross-Border E-Commerce Platform?
 Why Are Website ICP Filings Usually Rejected?
 How to troubleshoot a website that won’t open after setting up a 301 redirect?
Related Products
 Yiyingbao SaaS Intelligent Website Building and Marketing SystemYiyingbao SaaS Intelligent Website Building and Marketing System, AI-powered no-code website building, rapid creation of multilingual B2B international websites in 10 minutes, global server acceleration, AI-powered SEO optimization, helping businesses connect efficiently with global markets. The perfect integration of technology and operation makes building an international trade website remarkably simple
 AI+SEM Intelligent Advertising Marketing SystemAI+SEM drives intelligent ad creation, empowering full-funnel precision advertising marketing. The system automatically generates weekly/monthly reports, AI recommends keywords and target countries, monitors core metrics in real-time with intelligent alerts, and enables one-click high-conversion ad solutions to help quickly acquire customers and improve ROI.
 AI+SEO Dual-Engine System Optimization ServicesYiyingbao’s AI+SEO dual-engine optimization system helps foreign trade enterprises acquire high-quality organic traffic through AI-powered keyword research, content generation, and comprehensive technical optimization, significantly improving search rankings and conversion rates.
 AI+SNS Social Media Marketing SystemYingbao AI+SNS Social Media Marketing System - Precision social capture for the social media era. Supports one-click content synchronization across major platforms like Facebook and LinkedIn. AI intelligently rewrites posts for enhanced relevance. 24/7 AI customer service and user profiling analysis empower businesses to efficiently expand into global markets.
 AI+SEO营销解决方案易营宝AI+SEO营销解决方案,通过AI批量写作、智能生成TDK、精准关键词扩词等功能,全面优化网站SEO效果,提升流量与转化率。助力企业构建高效智能网站新生态。
 AI+SEM Advertising Marketing SolutionsAI+SEM Advertising Marketing Solution leverages AI technology to deeply empower SEM ad campaigns. It automatically generates weekly/monthly reports using AI, presenting account data across multiple dimensions for comprehensive insights into campaign performance and trends. The system precisely recommends keywords and target countries, intelligently generates high-conversion ad copy, and enables one-click activation of efficient campaign plans to help businesses rapidly acquire customers. Simultaneously, it monitors core metrics in real time, intelligently identifies abnormal fluctuations, and issues timely alerts to ensure stable, high-return advertising results.
 Domain Name ServicesEasyWin provides professional domain name services, including intelligent queries, one-stop registration, brand protection, and full lifecycle management, helping businesses build a digital brand image.
 EasyOperate B2C Cross-Border E-Commerce Platform & Independent WebsiteEasyStore B2C Cross-border E-commerce Independent Store is an intelligent website building and cross-border e-commerce integrated solution independently developed by EasyStore Information Technology (Beijing) Co., Ltd. The system is specially designed for small and medium-sized as well as large export enterprises, integrating 'website building, operation, marketing, advertising, and conversion' into one, helping enterprises quickly establish cross-border e-commerce independent stores to achieve brand globalization and global sales growth.
The platform supports multiple languages, multiple currencies, and multi-channel marketing, with built-in AI intelligent translation and SEO optimization systems, suitable for mainstream markets such as Southeast Asia, Europe and America, Latin America, and the Middle East, assisting Chinese manufacturing enterprises in efficiently deploying international e-commerce strategies. SSL证书易营宝提供专业SSL安全证书服务,包括单域名和泛域名证书,确保网站数据传输加密、身份验证和完整性保护,助力企业建立安全可信的在线业务环境。