- CBP Finalizes Electronic Rail Export Manifest Rule, Effective October 26, 2026Oct 26, 2026View details
- Amazon’s 2026 peak season surcharge takes effect on October 25Oct 26, 2026View details
- AI Is Eating SaaS: Three Real-World Cases in One AfternoonOct 25, 2026View details
- Exiger CEO: The SaaS Apocalypse Is Real, but It Means Something DifferentOct 25, 2026View details
- Hengqin Cooperation Zone Shares Cross-Border E-Commerce Developments, Focusing on Macao-Hengqin Collaboration and International MarketsOct 24, 2026View details
- A Shenyang study highlights the development of the “cross-border e-commerce + industrial cluster” modelOct 24, 2026View details
How do you disable legacy TLS protocols in an HTTPS-compliant configuration?
A common way to configure HTTPS compliance is to disable legacy TLS versions by turning off TLS 1.0, TLS 1.1, and earlier SSL protocols, retaining TLS 1.2, and enabling TLS 1.3 when supported by the server. However, whether the configuration meets requirements also depends on the applicable security baseline, cipher suites, certificates, and the actual scope of enforcement; protocol versions alone are not enough to determine compliance.
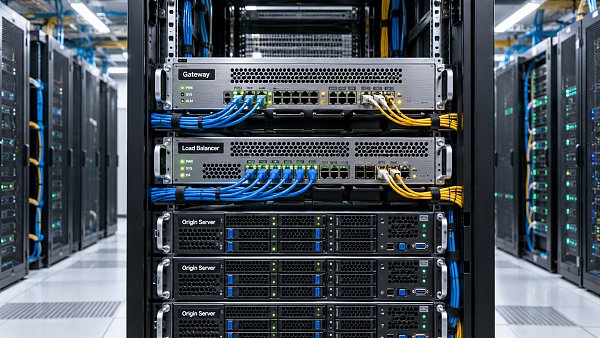
Before making changes, first confirm where the browser’s TLS connection terminates. If the website uses a CDN, WAF, or load balancer, changing only the origin server configuration may leave the public-facing endpoint accepting legacy protocols.
Identify all HTTPS endpoints that need to be updated
Corporate websites for international trade, cross-border stores, and advertising landing pages often use an access path such as “visitor—CDN/WAF—load balancer—origin server.” Each independently established TLS connection has its own protocol settings. If an intermediary only passes traffic through, the component that actually terminates TLS on the backend controls the settings.
We recommend mapping endpoints by domain name and listening port, rather than checking only by server count:
- Public-facing endpoints: primary domains, www subdomains, multilingual sites, stores, APIs, and advertising landing pages.
- Origin connections: HTTPS connections from the CDN to the load balancer, and from the reverse proxy to the application service.
- Alternative access points: directly accessible origin server addresses, backup domains, management endpoints, and other HTTPS ports.
The CDN’s “minimum TLS version” setting typically controls visitor connections; the protocol for origin connections must be configured separately. If the origin connection still uses HTTP, passing a public-facing test does not mean the entire connection path is encrypted.
Specify which protocols are allowed in the configuration
Rather than disabling older versions one by one, it is clearer to explicitly list the protocols that are allowed. Before configuring them, confirm that the web server and its linked TLS library support the target versions. Adding TLS 1.3 to a configuration file does not mean the current environment can provide it.
Nginx configuration example
Set the following in the appropriate configuration context:
ssl_protocols TLSv1.2 TLSv1.3;If all sites follow the same policy, manage it centrally at the http level and check whether any server blocks override the configuration. When multiple HTTPS virtual hosts share the same address and port, also check the default virtual host: protocol negotiation may be affected by the default server configuration, so it is not enough to modify only the configuration block for the target domain.
After saving, check the syntax before reloading the service:
nginx -t
nginx -s reload
Reload the service only after the syntax check succeeds. In containerized, clustered, or hosted environments, use the corresponding deployment mechanism to update the configuration and ensure that all instances use the same settings, so that some requests do not continue to reach outdated nodes.
Configuring Apache and hosted platforms
In Apache, the SSLProtocol directive can be used to restrict protocols. For example, in an environment that supports the relevant versions, use:
SSLProtocol -all +TLSv1.2 +TLSv1.3Also check global settings, virtual host configurations, and their inheritance relationships. When using a CDN, cloud load balancer, or SaaS website-building platform, adjust the minimum version in the console of the component that actually handles TLS, and verify visitor and origin connections separately.
In scenarios involving an integrated website-building and marketing service platform such as 易营宝, website pages, marketing domains, CDNs, and origin servers may be managed by different parties. Before implementation, clarify who is responsible for configuring each endpoint and how it will be verified. Do not assume that “the platform has deployed a certificate” means “legacy protocols have been disabled on all endpoints.”
Verification must confirm both that legacy versions are rejected and that newer versions work
Being able to open a website in a browser only shows that some protocol negotiation succeeded; it does not prove that older versions have been disabled. Initiate handshakes for specific versions against the same domain:
openssl s_client -connect example.com:443 -servername example.com -tls1
openssl s_client -connect example.com:443 -servername example.com -tls1_1
openssl s_client -connect example.com:443 -servername example.com -tls1_2
openssl s_client -connect example.com:443 -servername example.com -tls1_3
Replace the example domain with the actual domain. The expected result is that TLS 1.0 and TLS 1.1 cannot complete a handshake, while TLS 1.2 works normally. If TLS 1.3 is intended to be available, verify that it succeeds as well. -servername supplies SNI to prevent the request from reaching the wrong virtual host.
An error during a legacy protocol test does not necessarily mean the server rejected the protocol. The local OpenSSL installation may already prohibit older protocols or may not have any compatible legacy cipher suites available. If the client fails before sending a handshake, the result cannot be used as evidence that the server has disabled the protocol. Check the error message and cross-validate using a TLS scanning tool with the appropriate probing capabilities.
Check public domains and origin servers separately. To connect directly to an origin server, replace -connect with the origin server IP while continuing to specify the domain with -servername. Also test IPv4, IPv6, backup endpoints, and different deployment nodes. Record the test time, target address, and negotiation results for acceptance and subsequent troubleshooting.
Confirm compatibility across the business workflow
Older operating systems, embedded devices, or API clients that have not been updated for a long time may be unable to connect after the change. Before deployment, identify dependencies using connection logs, a list of callers, and business testing. Pay particular attention to inquiry submissions, payment redirects, order callbacks, marketing data interfaces, and third-party synchronization tasks.
Where possible, resolve compatibility issues by upgrading the client, runtime environment, or interface component. If a transition period is genuinely necessary, consider an isolated, dedicated endpoint and restrict its access scope with a clearly defined retirement date. Do not reopen the entire main website just for one legacy caller. During the rollout, monitor handshake errors, callback failures, and key form results; being able to open a page does not mean that transaction or lead-generation workflows are working properly.
Disabling legacy TLS is not the entirety of HTTPS security work. Cipher suites under TLS 1.2 still need to be reviewed, and certificate chains, domain matching, expiration management, and mixed content must also be handled separately. HTTP redirects and HSTS serve distinct purposes and cannot replace protocol restrictions. At handoff, retain an endpoint inventory, the effective configuration, and verification records. Check against the same baseline whenever marketing domains are added or the CDN is migrated.
Related Articles
 How do you disable legacy TLS protocols in an HTTPS-compliant configuration?
 How can a company website introduction page help visitors quickly understand the core business?
 How Can You Prevent a Video News Module from Slowing Down Page Loading?
Related Products
 Yiyingbao SaaS Intelligent Website Building and Marketing SystemYiyingbao SaaS Intelligent Website Building and Marketing System, AI-powered no-code website building, rapid creation of multilingual B2B international websites in 10 minutes, global server acceleration, AI-powered SEO optimization, helping businesses connect efficiently with global markets. The perfect integration of technology and operation makes building an international trade website remarkably simple
 AI+SEM Intelligent Advertising Marketing SystemAI+SEM drives intelligent ad creation, empowering full-funnel precision advertising marketing. The system automatically generates weekly/monthly reports, AI recommends keywords and target countries, monitors core metrics in real-time with intelligent alerts, and enables one-click high-conversion ad solutions to help quickly acquire customers and improve ROI.
 AI+SEO Dual-Engine System Optimization ServicesYiyingbao’s AI+SEO dual-engine optimization system helps foreign trade enterprises acquire high-quality organic traffic through AI-powered keyword research, content generation, and comprehensive technical optimization, significantly improving search rankings and conversion rates.
 AI+SNS Social Media Marketing SystemYingbao AI+SNS Social Media Marketing System - Precision social capture for the social media era. Supports one-click content synchronization across major platforms like Facebook and LinkedIn. AI intelligently rewrites posts for enhanced relevance. 24/7 AI customer service and user profiling analysis empower businesses to efficiently expand into global markets.
 AI+SEO营销解决方案易营宝AI+SEO营销解决方案,通过AI批量写作、智能生成TDK、精准关键词扩词等功能,全面优化网站SEO效果,提升流量与转化率。助力企业构建高效智能网站新生态。
 AI+SEM Advertising Marketing SolutionsAI+SEM Advertising Marketing Solution leverages AI technology to deeply empower SEM ad campaigns. It automatically generates weekly/monthly reports using AI, presenting account data across multiple dimensions for comprehensive insights into campaign performance and trends. The system precisely recommends keywords and target countries, intelligently generates high-conversion ad copy, and enables one-click activation of efficient campaign plans to help businesses rapidly acquire customers. Simultaneously, it monitors core metrics in real time, intelligently identifies abnormal fluctuations, and issues timely alerts to ensure stable, high-return advertising results.
 Domain Name ServicesEasyWin provides professional domain name services, including intelligent queries, one-stop registration, brand protection, and full lifecycle management, helping businesses build a digital brand image.
 EasyOperate B2C Cross-Border E-Commerce Platform & Independent WebsiteEasyStore B2C Cross-border E-commerce Independent Store is an intelligent website building and cross-border e-commerce integrated solution independently developed by EasyStore Information Technology (Beijing) Co., Ltd. The system is specially designed for small and medium-sized as well as large export enterprises, integrating 'website building, operation, marketing, advertising, and conversion' into one, helping enterprises quickly establish cross-border e-commerce independent stores to achieve brand globalization and global sales growth.
The platform supports multiple languages, multiple currencies, and multi-channel marketing, with built-in AI intelligent translation and SEO optimization systems, suitable for mainstream markets such as Southeast Asia, Europe and America, Latin America, and the Middle East, assisting Chinese manufacturing enterprises in efficiently deploying international e-commerce strategies. SSL证书易营宝提供专业SSL安全证书服务,包括单域名和泛域名证书,确保网站数据传输加密、身份验证和完整性保护,助力企业建立安全可信的在线业务环境。