- Which customer acquisition channels will be affected by cross-border marketing trends in 2026?Sep 06, 2026View details
- Which homogenization risks should be considered in an analysis of the AI-powered website building industry?Aug 30, 2026View details
- How Will AI Marketing Trends 2026 Change Advertising Budget AllocationAug 28, 2026View details
- Is the EV SSL certificate market shrinking or upgrading? How should companies assess certificate procurement?Aug 11, 2026View details
- Why the old AMP SEO 2020 practices no longer work and what has changed in current optimization prioritiesAug 02, 2026View details
- How to Choose Topics for an Industry News Section to Attract More Organic Search TrafficJul 29, 2026View details
How to Choose a Website Protection Solution Without Affecting Normal Access
When choosing a website anti-attack solution, many teams initially think, “The stricter the blocking, the safer it is.” However, after conducting an actual evaluation, the real problems are often not that attacks were left unblocked, but that legitimate users were mistakenly blocked, pages became slower, and form submissions failed, ultimately affecting inquiries, orders, and advertising performance. A qualified website anti-attack solution should not merely block traffic; it must also ensure uninterrupted legitimate access and continuous operation of core business functions.
This is especially true for marketing websites, overseas independent websites, and multilingual corporate websites, where security and accessibility are inherently connected. If you stop attacks but also block Google crawling, overseas visitor access, and advertising landing-page conversions, it is difficult to say that you have chosen the right solution.
For a Website Anti-Attack Solution, Don't Rush to Compare “Protection Capabilities”
A common mistake in technical evaluations is treating “protection strength” as the only criterion. In fact, the first thing to confirm is what your website can least afford to have affected.
For a corporate website, the biggest concerns are being inaccessible, loading slowly, or having an unavailable contact form. For a cross-border e-commerce store, the biggest concerns are delays in the checkout process, payment interface failures, and being overwhelmed by fraudulent traffic during promotional campaigns. For an advertising landing page, the biggest concern is that the system may misidentify real visitors as bots and block them during traffic peaks.
In other words, the core of a website anti-attack solution is not whether protection exists, but whether legitimate users can still access the website smoothly under different attack scenarios. This is the key criterion that should receive the most attention during selection.
A simple standard to remember is this: protection effectiveness, access speed, false-positive blocking rate, and operations and maintenance costs must all be considered together. Missing any one of these factors can lead to problems after launch.
What Usually Affects Legitimate Access Is Not the Attack Itself
Many people think an attack means bandwidth being fully consumed or a server going down. Those situations are certainly serious, but in day-to-day projects, it is more common for the website to “appear to be running while the business no longer works properly.”
For example:
- CC protection rules are too strict, causing overseas users to trigger verification frequently and reducing form conversion rates;
- WAF rules are not aligned with business paths, causing search, login, and inquiry interfaces to be mistakenly blocked;
- After high-defense protection is enabled, the origin-fetch path becomes longer and first-screen loading becomes noticeably slower;
- Static-resource caching policies are unreasonable, so the page is more secure but the access experience becomes worse;
- Search-engine crawlers are blocked by challenge mechanisms, causing fluctuations in indexing and rankings.
These problems have one thing in common: the security policies themselves are not necessarily wrong, but they have not been configured according to the business scenarios. If technical evaluators only review the provider's blocking reports, they can easily overlook this aspect.
How to Determine Whether a Solution Will Affect Legitimate Access
During evaluation, I recommend working backward from the “access path” rather than forward from the “security feature list.”
First, list your website's key paths: homepage access, core landing pages, search, login, registration, form submission, payment or inquiry, file uploads, and API calls. Then ask the solution provider, one by one: After implementation, what additional checks, redirects, and challenge mechanisms will be added to these paths? Does the solution support whitelists, regional policies, device policies, and interface-level allowlisting?
Here are several particularly practical points to consider.
First, assess false-positive handling capabilities, not just blocking capabilities.
A truly mature solution must support detailed rule configuration, rapid allowlisting, and log retention, as well as optimization based on URL, IP, country or region, UA, Cookie, request frequency, and other dimensions. Otherwise, once legitimate traffic is mistakenly blocked, you can only relax the rules globally, which means neither security nor availability is preserved.
Second, assess overseas access performance.
If your customers are located in North America, Europe, Southeast Asia, the Middle East, or other regions, coverage of protection nodes in your target markets is critical. Too few nodes, distant origin servers, and lengthy verification paths can all directly slow down access. This issue is particularly evident for websites targeting overseas markets: many solutions appear stable in China but provide only average experiences overseas.
Third, check whether layered protection is supported.
Not every type of attack should be blocked in the same way. DDoS attacks, CC attacks, malicious crawlers, vulnerability scanning, and brute-force attacks against backend systems are risks at different levels. Applying them all to one coarse-grained rule is the easiest way to harm legitimate traffic. Layered protection is generally more reliable: the network layer handles traffic, the application layer identifies requests, and the business layer processes abnormal behavior.
Fourth, assess observability after implementation.
If the backend only shows “how many times traffic was blocked,” the value of that information is limited. A technical evaluation also needs to determine which pages were attacked, which countries had abnormal traffic, which rules were triggered frequently, whether legitimate users were challenged, and whether peak latency changed. Without this data, subsequent optimization is essentially guesswork.
Different Websites Require Different Protection Strategies
This is another area where many companies can easily make the wrong choice during selection.
For a showcase-style corporate website, the priorities are usually stable access, basic WAF protection, CC protection, CDN acceleration, and backend login protection. Particularly extensive high-defense resources may not be necessary. The primary goal is not to withstand extreme business peaks, but to ensure that brand pages, product pages, and contact pages remain consistently available.
For a marketing-oriented independent website, the situation is more complex. You need to protect against malicious traffic without harming advertising campaigns, SEO crawling, or overseas organic traffic. This type of website is better suited to a combination of “security + acceleration + operational flexibility” rather than simply adding more high-defense resources. Many service providers specializing in global marketing design website architecture, CDN distribution, SEO accessibility, and security policies together, which is more efficient than piecing solutions together later. The value of platforms such as Yiyingbao, which provide smart website development, overseas marketing, and website growth services at the same time, lies here: they do not simply add a security layer, but incorporate the goals of indexability, promotion, and conversion into the overall solution evaluation. For evaluators, this kind of integrated capability is an advantage in cross-border business.
For an online store, membership system, or platform with frequent user interactions, page access alone is not enough. Login, shopping carts, inventory interfaces, payment callbacks, API rate limiting, and bot identification all need to be evaluated separately. The real problems usually do not occur on the homepage, but in the interfaces that generate the most revenue and are also the most vulnerable.
Don't Be Misled by Several “Professional-Looking” Metrics
When selecting a website anti-attack solution, technical teams are often influenced by terms such as “massive traffic scrubbing capacity,” “millisecond-level identification,” and “intelligent protection engine.” These terms are not irrelevant, but they are insufficient to support a decision.
The following questions are actually more useful:
- Does the solution support gradual rollout, allowing you to first verify its effectiveness for selected domains or paths?
- Can traffic be quickly switched back during an abnormal situation to prevent the entire website from being overwhelmed by a new policy?
- Does it support identifying and allowing search-engine crawlers, advertising review visits, and third-party monitoring tools?
- After a legitimate user is mistakenly blocked, can rules be adjusted within minutes, or is a support ticket required?
- Can logs be exported and integrated with existing monitoring or SIEM systems?
- Are different protection policies available for static pages, dynamic interfaces, and backend administration entrances?
These questions are highly practical and make it easier to determine whether a provider truly understands website operations rather than merely knowing how to use security terminology.
A Practical Selection Process
If you are conducting an internal evaluation, you can proceed in the following order:
First, define your business baselines. For example, homepage availability, overseas loading speed, form submission success rate, and search-engine crawlability should be clarified first. Otherwise, it will be difficult to determine whether the solution is worth implementing.
Then confirm the types of attacks and historical problems. Have you experienced traffic abuse, malicious crawling, backend attacks, or credential stuffing against interfaces, or are you simply concerned about future risks? Depending on the current situation, the budget and depth of the solution can vary significantly.
Next, conduct a limited-scope validation. Do not switch the entire website at once. Start with a second-level domain, a group of landing pages, or a non-payment-critical path. Observe access speed, error rates, false-positive blocking, and log quality.
Finally, discuss long-term operations and maintenance. Many solutions encounter no problems on the day they go live. The real difference emerges over the following three months: whether the provider can continuously optimize the system or can only rely on manual firefighting becomes clear with actual use.
When Is a “Heavy-Duty” Solution Not Suitable?
If the website has limited traffic, simple business paths, and no history of significant attacks, adopting a complex and costly solution from the outset may not be worthwhile. You may need basic WAF protection, CDN, backend security hardening, rate limiting, and monitoring alerts rather than a complete heavy-duty protection architecture.
There is another situation that also requires caution: the website's underlying performance is already poor, with slow interface responses, disorganized caching policies, or insufficient server resources. In this case, attributing all slow access to attacks can lead to an incorrect assessment. The security layer can mitigate risks, but it cannot replace website performance optimization. If the basic architecture has not been properly organized, even the best website anti-attack solution can only provide limited relief.
How to Make the Final Decision
Website anti-attack solutions worth choosing usually share several characteristics: they can handle risks in layers, identify false positives clearly, support global access, and work with your website development, SEO, advertising, and conversion processes instead of conflicting with them.
If your website is responsible for lead generation, especially for overseas markets, do not ask only, “How many Gbps of attacks can it defend against?” You should also ask, “Will it affect advertising traffic entering the website, organic indexing, form conversions, or the access experience in different regions?” Once these questions are answered clearly, the solution will be closer to the actual needs of the business.
Ultimately, a website anti-attack solution is not simply an “insurance shell.” It is about finding a stable balance between security and growth. Protection that preserves legitimate access is the protection that delivers real value.
Frequently Asked Questions
Is a more expensive website anti-attack solution always better?
No. Website type, attack risks, visitor locations, and business paths vary, so the appropriate solution can differ significantly. An oversized solution wastes budget, while an undersized one may not withstand the risks.
Is it normal for pages to become slower after protection is enabled?
It is possible, but the slowdown should not be significant. If latency increases noticeably, you should generally check node coverage, the origin-fetch path, caching configuration, and whether the challenge mechanisms are too intensive.
What types of false positives are marketing websites most concerned about?
The most common are failed form submissions, blocked access to advertising landing pages, and search-engine crawlers being blocked. These issues directly affect lead generation and are often not discovered immediately.
Does using only a CDN count as complete protection?
Not necessarily. A CDN can help accelerate access and relieve some traffic pressure, but whether it provides sufficient application-layer protection depends on the capabilities and configuration of the specific product.
Image Placeholder List
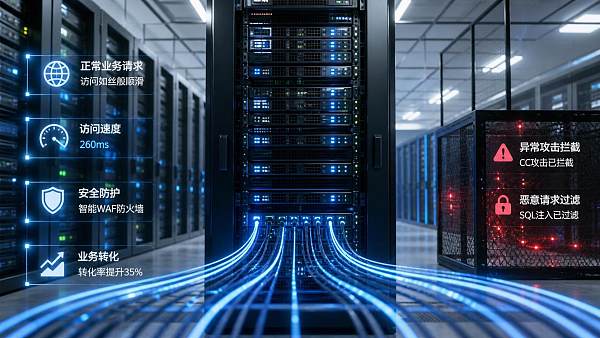
: Recommended placement: after “What Usually Affects Legitimate Access Is Not the Attack Itself”; image content: “Illustration of legitimate access and false-positive blocking risks after website protection is enabled”; alt text: “Illustration of common scenarios in which legitimate access is mistakenly blocked by a website anti-attack solution”
Recommended Internal-Link Anchor Text
- How to combine security and acceleration for an overseas independent website: link to the website development and basic infrastructure solution page
- How to balance SEO and access speed on a multilingual website: link to the multilingual website development or SEO topic page
- How to optimize advertising landing-page loading speed: link to the conversion-rate optimization or landing-page service page
- How to select CDN nodes for an overseas website: link to the overseas deployment or global access optimization page
- What to do when a corporate website is crawled by malicious bots: link to the website operations and maintenance or security protection knowledge page
Recommended Authoritative External Sources
- Official technical documentation from cloud security providers
- Official webmaster platform documentation from search engines
- Reports from cybersecurity research institutions or incident response organizations
Related Articles
Related Products
 Yiyingbao SaaS Intelligent Website Building and Marketing SystemYiyingbao SaaS Intelligent Website Building and Marketing System, AI-powered no-code website building, rapid creation of multilingual B2B international websites in 10 minutes, global server acceleration, AI-powered SEO optimization, helping businesses connect efficiently with global markets. The perfect integration of technology and operation makes building an international trade website remarkably simple
 AI+SEM Intelligent Advertising Marketing SystemAI+SEM drives intelligent ad creation, empowering full-funnel precision advertising marketing. The system automatically generates weekly/monthly reports, AI recommends keywords and target countries, monitors core metrics in real-time with intelligent alerts, and enables one-click high-conversion ad solutions to help quickly acquire customers and improve ROI.
 AI+SEO Dual-Engine System Optimization ServicesYiyingbao’s AI+SEO dual-engine optimization system helps foreign trade enterprises acquire high-quality organic traffic through AI-powered keyword research, content generation, and comprehensive technical optimization, significantly improving search rankings and conversion rates.
 AI+SNS Social Media Marketing SystemYingbao AI+SNS Social Media Marketing System - Precision social capture for the social media era. Supports one-click content synchronization across major platforms like Facebook and LinkedIn. AI intelligently rewrites posts for enhanced relevance. 24/7 AI customer service and user profiling analysis empower businesses to efficiently expand into global markets.
 AI+SEO营销解决方案易营宝AI+SEO营销解决方案,通过AI批量写作、智能生成TDK、精准关键词扩词等功能,全面优化网站SEO效果,提升流量与转化率。助力企业构建高效智能网站新生态。
 AI+SEM Advertising Marketing SolutionsAI+SEM Advertising Marketing Solution leverages AI technology to deeply empower SEM ad campaigns. It automatically generates weekly/monthly reports using AI, presenting account data across multiple dimensions for comprehensive insights into campaign performance and trends. The system precisely recommends keywords and target countries, intelligently generates high-conversion ad copy, and enables one-click activation of efficient campaign plans to help businesses rapidly acquire customers. Simultaneously, it monitors core metrics in real time, intelligently identifies abnormal fluctuations, and issues timely alerts to ensure stable, high-return advertising results.
 Domain Name ServicesEasyWin provides professional domain name services, including intelligent queries, one-stop registration, brand protection, and full lifecycle management, helping businesses build a digital brand image.
 EasyOperate B2C Cross-Border E-Commerce Platform & Independent WebsiteEasyStore B2C Cross-border E-commerce Independent Store is an intelligent website building and cross-border e-commerce integrated solution independently developed by EasyStore Information Technology (Beijing) Co., Ltd. The system is specially designed for small and medium-sized as well as large export enterprises, integrating 'website building, operation, marketing, advertising, and conversion' into one, helping enterprises quickly establish cross-border e-commerce independent stores to achieve brand globalization and global sales growth.
The platform supports multiple languages, multiple currencies, and multi-channel marketing, with built-in AI intelligent translation and SEO optimization systems, suitable for mainstream markets such as Southeast Asia, Europe and America, Latin America, and the Middle East, assisting Chinese manufacturing enterprises in efficiently deploying international e-commerce strategies. SSL证书易营宝提供专业SSL安全证书服务,包括单域名和泛域名证书,确保网站数据传输加密、身份验证和完整性保护,助力企业建立安全可信的在线业务环境。