









- China’s Ministry of Commerce Responds to Additional Charges on Low-Value Imports Imposed by the EUNov 06, 2026View details
- Two Internet Development Reports Released at the 2026 World Internet ConferenceNov 05, 2026View details
- Internet Business Revenue of Enterprises Above the Designated Size Reached RMB 1.716 Trillion in the First Three Quarters, with Profits Up 17.6%Nov 05, 2026View details
- Shopify's Third-Quarter Revenue and GMV Fall Short of Expectations, Sending Shares Tumbling Before the Market OpensNov 04, 2026View details
- Temu Sellers See a Decline in Traffic as the Platform’s Traffic Allocation ShiftsNov 04, 2026View details
- UK Regulator Requires E-Commerce Businesses to Clearly Display Total Prices Including Mandatory Delivery ChargesNov 04, 2026View details
Is Your Website Platform for Export Businesses Secure? How to Check Access Permissions
Is the data on an export website platform secure? You need to look beyond whether the site uses an encrypted connection. You should also consider who can log in to the back end, view customer information, export data, and whether these actions can be traced. For businesses evaluating platforms, security is not a promise from a supplier; it is a set of conditions that can be checked through permission settings, live demonstrations, and contractual terms.
An export website may store more than page content. It may also contain inquiries, customer contact details, orders, quotation files, and marketing account information. When website development, SEO, advertising, and social media services share the same workflow, more people and third-party tools are involved, making it even more important to define permission boundaries in advance.
Inventory the data first, then decide who can access it
Before reviewing permissions, find out what data the platform will handle, where it comes from, and where it goes. For example, information submitted by visitors through a form may be stored in the website back end or synchronized with a customer management system, email, or third-party marketing tool. Even if back-end permissions are configured appropriately, a shared inbox that receives inquiries or an external system could still become a point of exposure.
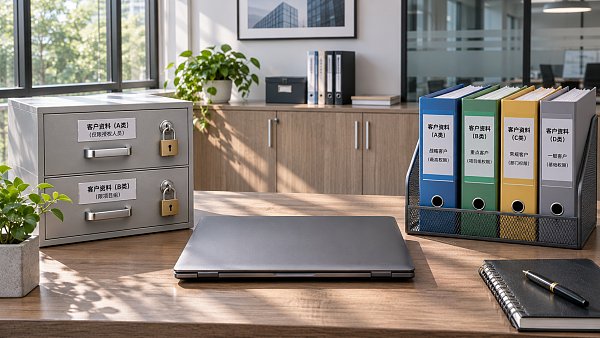
You can define common permissions according to work requirements. Content editors need to update pages, but typically do not need to export all inquiries. Sales staff need to handle customer information, but may not need to change website security settings. An advertising agency may need to manage landing pages or advertising accounts, but should not automatically have access to all customer and order data.
For quotations, customer lists, orders, and other sensitive information, check not only whether users can view the data, but also whether they can search, download, export in bulk, delete, and forward it. The fact that data is not visible on a page does not necessarily mean an account cannot access it through an export interface or connected tool.
Test permissions with real accounts, not just role names
The fact that a platform offers roles such as “administrator,” “editor,” and “sales” only indicates that role categories exist; it does not mean the permissions meet your business needs. During a platform demonstration, ask the supplier to log in with different roles and verify permissions against real work tasks.
- Check whether accounts are individual. Each employee and external service provider should use their own account. Sharing an administrator account makes it harder to manage handovers when someone leaves, trace responsibility, and revoke access promptly.
- Check the scope of access. See whether access can be restricted by website, language version, business area, or data type. For example, does an outsourced English-language content editor have to see inquiries from every market?
- Check sensitive actions. Test whether a standard account can export customer lists, delete inquiries, change the form recipient email address, add users, or adjust administrator permissions. Viewing, exporting, and deleting should ideally be controlled separately.
- Check account deactivation. Simulate an employee leaving or a partnership ending. After deactivating the account, check whether it can still log in, and make sure associated permissions, API credentials, and shared files have also been addressed.
Not every platform supports permissions as granular as individual fields or pages. For a small team with relatively low data sensitivity, clear role assignments and strict control of administrator accounts may be sufficient. When multiple departments, regions, or external agencies work together, overly broad permissions can force businesses to choose between efficiency and data exposure.
What can administrators and service providers see?
In addition to company-owned accounts, find out how platform operations, technical support, and outsourced teams access the system. Service personnel may need to troubleshoot problems, but that does not mean they should have unrestricted, ongoing access to the back end. Ask the supplier to explain under what circumstances support staff can access the system, how access is restricted, whether company authorization is required, and how access is revoked when the work is complete.
Integrated website and marketing services may also involve advertising accounts, traffic analytics tools, social media accounts, and form plugins. When connecting these services, distinguish between platform account permissions and third-party account permissions. Revoking a website back-end account does not necessarily revoke advertising account access or API tokens. Before work begins, prepare a list of authorizations that records account ownership, who is authorized, the purpose, and how access can be revoked.
When evaluating platforms that provide both website development and overseas marketing services, such as 易营宝, you can review the website back end and marketing collaboration together in a single permissions checklist. The available role granularity, third-party authorization methods, and service personnel access procedures should be confirmed through product demonstrations and service agreements. Do not assume permissions are sufficiently granular simply because a service is “integrated.”
Operation logs should support traceability
Having a logging feature does not guarantee that an incident can be investigated. Check whether logs record the person performing an action, the time, the type of action, and the relevant object, and whether they cover logins, permission changes, data exports and deletions, and changes to form recipient addresses or third-party authorizations.
Also find out how long logs are retained, who can view them, whether they can be exported, and whether standard administrators can delete or modify records. Log retention should meet the company's internal audit and investigation needs. If high-risk actions are not recorded or multiple people use the same account, it may be impossible to determine responsibility even after a data leak is discovered.
Ask the supplier to change a permission or export data in a demonstration environment, then review the corresponding log entry. For repeated failed logins, logins from unusual locations, or large-volume exports, also find out whether the platform provides alerts and who receives them. If the platform has no automatic alerts, the company should assess whether it can compensate with regular checks.
Include offboarding, backups, and responsibilities in your evaluation criteria
In addition to access management, the ability to retrieve data also affects security. Ask what data the platform supports exporting, such as inquiries, orders, page assets, and database content; whether exports use common formats; and whether attachments and field relationships can be preserved. Being able to download website pages does not mean that form data and customer records can also be migrated in full.
For backups, find out what is included, how often backups are made, how long they are retained, and how recovery works. Distinguish between having a backup and being able to restore the system to a usable state. For businesses that cannot tolerate extended interruptions to inquiries or orders, recovery time and the cooperation required from both parties should also be part of the evaluation.
Contracts or service documents should also specify data ownership, arrangements for exporting and deleting data after service termination, the scope of third-party processing, and each party's notification and cooperation responsibilities in the event of a security incident. For personal information from overseas visitors, relevant internal personnel should assess the collection, storage, and cross-border processing arrangements based on the markets served, data flows, and applicable requirements.
When making a final selection, include the following as demonstration acceptance criteria: whether access can be assigned by job role, whether data exports can be traced, whether all access can be revoked when the partnership ends, and whether data can be retrieved. If a platform that handles customer lists and orders can meet these conditions only through verbal assurances, or cannot meet the company's management requirements, do not rush to launch, even if its website development and marketing features are comprehensive.
Related Articles
 Is Your Website Platform for Export Businesses Secure? How to Check Access Permissions
 The EU Will Require Product Identification Codes for Low-Value Cross-Border Parcels Starting November 1
 How Can You Prevent Admin Account Takeovers on a SaaS Website Platform?
Related Products
 Yiyingbao SaaS Intelligent Website Building and Marketing SystemYiyingbao SaaS Intelligent Website Building and Marketing System, AI-powered no-code website building, rapid creation of multilingual B2B international websites in 10 minutes, global server acceleration, AI-powered SEO optimization, helping businesses connect efficiently with global markets. The perfect integration of technology and operation makes building an international trade website remarkably simple
 AI+SEM Intelligent Advertising Marketing SystemAI+SEM drives intelligent ad creation, empowering full-funnel precision advertising marketing. The system automatically generates weekly/monthly reports, AI recommends keywords and target countries, monitors core metrics in real-time with intelligent alerts, and enables one-click high-conversion ad solutions to help quickly acquire customers and improve ROI.
 AI+SEO Dual-Engine System Optimization ServicesYiyingbao’s AI+SEO dual-engine optimization system helps foreign trade enterprises acquire high-quality organic traffic through AI-powered keyword research, content generation, and comprehensive technical optimization, significantly improving search rankings and conversion rates.
 AI+SNS Social Media Marketing SystemYingbao AI+SNS Social Media Marketing System - Precision social capture for the social media era. Supports one-click content synchronization across major platforms like Facebook and LinkedIn. AI intelligently rewrites posts for enhanced relevance. 24/7 AI customer service and user profiling analysis empower businesses to efficiently expand into global markets.
 AI+SEO营销解决方案易营宝AI+SEO营销解决方案,通过AI批量写作、智能生成TDK、精准关键词扩词等功能,全面优化网站SEO效果,提升流量与转化率。助力企业构建高效智能网站新生态。
 AI+SEM Advertising Marketing SolutionsAI+SEM Advertising Marketing Solution leverages AI technology to deeply empower SEM ad campaigns. It automatically generates weekly/monthly reports using AI, presenting account data across multiple dimensions for comprehensive insights into campaign performance and trends. The system precisely recommends keywords and target countries, intelligently generates high-conversion ad copy, and enables one-click activation of efficient campaign plans to help businesses rapidly acquire customers. Simultaneously, it monitors core metrics in real time, intelligently identifies abnormal fluctuations, and issues timely alerts to ensure stable, high-return advertising results.
 Domain Name ServicesEasyWin provides professional domain name services, including intelligent queries, one-stop registration, brand protection, and full lifecycle management, helping businesses build a digital brand image.
 EasyOperate B2C Cross-Border E-Commerce Platform & Independent WebsiteEasyStore B2C Cross-border E-commerce Independent Store is an intelligent website building and cross-border e-commerce integrated solution independently developed by EasyStore Information Technology (Beijing) Co., Ltd. The system is specially designed for small and medium-sized as well as large export enterprises, integrating 'website building, operation, marketing, advertising, and conversion' into one, helping enterprises quickly establish cross-border e-commerce independent stores to achieve brand globalization and global sales growth.
The platform supports multiple languages, multiple currencies, and multi-channel marketing, with built-in AI intelligent translation and SEO optimization systems, suitable for mainstream markets such as Southeast Asia, Europe and America, Latin America, and the Middle East, assisting Chinese manufacturing enterprises in efficiently deploying international e-commerce strategies. SSL证书易营宝提供专业SSL安全证书服务,包括单域名和泛域名证书,确保网站数据传输加密、身份验证和完整性保护,助力企业建立安全可信的在线业务环境。









