- Can the average annual growth rate reflect real opportunities in overseas markets?Oct 07, 2026View details
- Which customer acquisition channels will be affected by cross-border marketing trends in 2026?Sep 06, 2026View details
- Which homogenization risks should be considered in an analysis of the AI-powered website building industry?Aug 30, 2026View details
- How Will AI Marketing Trends 2026 Change Advertising Budget AllocationAug 28, 2026View details
- Is the EV SSL certificate market shrinking or upgrading? How should companies assess certificate procurement?Aug 11, 2026View details
- Why the old AMP SEO 2020 practices no longer work and what has changed in current optimization prioritiesAug 02, 2026View details
How to Choose an SSL Certificate: Application Scenarios for DV, OV, and EV Certificates
Many companies only address SSL certificates at the last minute before a website goes live, often judging them by whether a small lock icon is displayed. From a technical standpoint, this approach may not cause immediate issues; however, for websites that handle inquiries, member logins, order payments, file downloads, or backend administration, certificate selection also involves identity verification, domain asset management, renewal responsibilities, and customer trust. This is especially true for multilingual websites targeting overseas markets, cross-border online stores, and advertising landing pages, where certificate configuration errors often directly result in browser warnings, interrupted redirects, or lost conversions.
DV, OV, and EV are not three different encryption technologies, but three levels of applicant identity verification. Many procurement discussions become repetitive because encryption strength and corporate identity endorsement are confused with one another. When selecting a certificate, security managers should first consider these two dimensions separately.
First Clarify: What SSL Certificates Protect and What They Do Not
What is commonly referred to as an SSL certificate primarily uses the TLS protocol in actual deployment. Its core function is to establish an encrypted connection between the browser and the server, and to enable the browser to verify whether the domain being accessed matches the domain in the certificate. When users submit forms, log in to accounts, or enter contact details, the data is less likely to be directly read or tampered with during transmission.
However, certificates cannot replace website security governance. They cannot fix vulnerable plugins, prevent logins with weak passwords, or address server intrusions, overly broad database permissions, or phishing page impersonation. Quality control processes should particularly avoid one misconception: normal HTTPS operation does not mean that a website meets security requirements. A certificate is only the most basic layer, and one that must be continuously maintained.
From a browser perspective, DV, OV, and EV can use similar algorithms and key capabilities at the transmission encryption level. The real difference lies in the depth of the certificate authority's review of the applicant and the entity information that can be displayed in the certificate. Therefore, choosing a higher validation level should not be understood as meaning that a website is inherently more resistant to attacks, but rather that visitors can obtain stronger grounds for confirming the organization's identity.
DV, OV, and EV: The Main Difference Is Validation, Not the “Lock” Icon
A DV certificate, or Domain Validation certificate, requires the applicant only to prove control over the domain name. Common validation methods include DNS records, a designated email address, or website file verification. It is issued relatively quickly and is suitable for projects that require frequent page publishing, bulk management of sub-sites, or are in the testing stage. DV is generally practical enough for content-oriented corporate websites, event pages, advertising landing pages, and blogs or help centers where corporate identity verification is not the priority.
Its limitations are also clear: DV only demonstrates control of a domain name and does not prove that the operator is a verified company. If the website name differs substantially from the brand or group name, or if customers need to confirm the identity of the transaction counterparty, DV alone provides limited assurance. In B2B foreign trade scenarios, overseas buyers often review the company's website information, email domain, privacy policy, and contact details at the same time. In this case, DV can be used, but it should not be regarded as the entirety of trust building.
An OV certificate, or Organization Validation certificate, verifies the basic identity information of the applying organization in addition to domain control. It is suitable for official corporate websites, manufacturer catalog sites, customer portals, supplier collaboration platforms, and B2B websites that need to build long-term brand credibility. It is not necessarily “more suitable for all websites” than DV, but when a website handles quotations, sample requests, customer logins, after-sales service tickets, and similar business activities, the verifiable information provided through organization validation better aligns with the review practices of corporate customers.
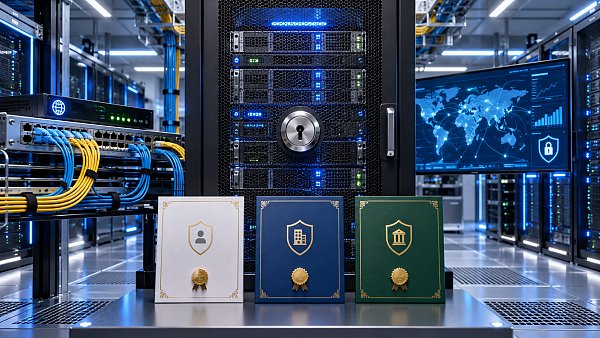
An EV certificate, or Extended Validation certificate, generally involves more stringent organization verification. It is suitable for financial services, payment-related pages, high-value transactions, public service portals, or platforms with clear internal requirements for entity credibility. It should be noted that modern browsers have changed how EV identity information is displayed. The prominent “green address bar” widely known in the past is no longer a universal experience. Purchasing EV does not mean that ordinary users will necessarily perceive its difference clearly in the address bar.
Therefore, the value of EV is better assessed in terms of compliance documentation, organization review, and high-risk business processes, rather than simply pursuing visual effects. If a website is only a standard product display page, increasing the review cycle and management costs merely for the “highest level” may not match the actual risk.
What Is Most Easily Overlooked Is Domain Coverage and the Certificate Lifecycle
When selecting a certificate, the validation level is only the first step. Many failures occur in domain coverage: example.com and www.example.com are different names; subdomains such as shop.example.com and en.example.com must also be explicitly covered. Multi-domain certificates are suitable for centrally managing multiple independent domain names; wildcard certificates can cover multiple subdomains at the same level, but they generally do not automatically cover the root domain and cannot extend indefinitely to multi-level subdomains. Specific coverage rules should be verified against the certificate application parameters and deployment plan.
Cross-border operations often involve a main website, regional sites, an online store, a CDN origin server, and marketing short links at the same time. If a certificate is purchased only for the primary domain and ad clicks are directed to an uncovered secondary domain, a browser warning will directly interrupt access. When using intelligent website-building or cross-border online store systems, the publishing process should include a four-part joint check of “domain name—certificate—redirect—page resources,” rather than leaving certificate configuration to post-launch troubleshooting.
A register should also be established for certificate validity periods and renewals. If the domain registrant, DNS management permissions, certificate account, and private key custodian are distributed among different employees or service providers, personnel changes can easily create renewal blind spots. For organizational restructuring, asset acquisition, or system migration projects, the digital asset inventory should be reviewed in parallel with other risk inventories. Similar to the due diligence approach emphasized in Financial Risks in State-Owned Enterprise Mergers and Acquisitions and Countermeasures, the same principle applies to website governance: beyond visible website assets, domain control, the certificate applicant entity, and renewal responsibilities must also be traceable.
Assess Based on Website Operations, Not Certificate Price Alone
For product display and inquiry websites of foreign trade manufacturers, OV is often a more balanced choice if company information is stable and customers conduct preliminary reviews of entity authenticity. For campaign pages aimed at search and social media advertising, where domains are published frequently, DV combined with standardized website information disclosure is usually more efficient. When a cross-border online store involves registration, addresses, orders, and payment redirects, in addition to considering OV or EV, it is also necessary to verify whether payment service providers, order systems, third-party scripts, and privacy pages use HTTPS throughout.
When Yiyingbao provides integrated services such as website building, SEO, advertising, and social media operations for foreign trade companies, multilingual official websites, and independent cross-border websites, certificates should not be treated as standalone technical plugins. A website that can be promoted must go through domain resolution, page publishing, resource loading, form transmission, redirect paths, and indexing checks. As long as any one of these steps still calls HTTP resources, mixed-content warnings may occur, affecting page integrity and user judgment.
Finally, here is a practical assessment sequence for security managers: first, confirm whether the website handles logins, transactions, or sensitive information; then determine whether customers need to verify the corporate entity; next, check the coverage relationship among the primary domain, subdomains, and regional websites; and finally, assign responsible parties for renewals, private keys, domain DNS permissions, and abnormal alerts. There is no absolute higher or lower configuration among DV, OV, and EV. A certificate is selected correctly only when it corresponds to business risks, identity requirements, and operational capabilities.
Related Articles
Related Products
 Yiyingbao SaaS Intelligent Website Building and Marketing SystemYiyingbao SaaS Intelligent Website Building and Marketing System, AI-powered no-code website building, rapid creation of multilingual B2B international websites in 10 minutes, global server acceleration, AI-powered SEO optimization, helping businesses connect efficiently with global markets. The perfect integration of technology and operation makes building an international trade website remarkably simple
 AI+SEM Intelligent Advertising Marketing SystemAI+SEM drives intelligent ad creation, empowering full-funnel precision advertising marketing. The system automatically generates weekly/monthly reports, AI recommends keywords and target countries, monitors core metrics in real-time with intelligent alerts, and enables one-click high-conversion ad solutions to help quickly acquire customers and improve ROI.
 AI+SEO Dual-Engine System Optimization ServicesYiyingbao’s AI+SEO dual-engine optimization system helps foreign trade enterprises acquire high-quality organic traffic through AI-powered keyword research, content generation, and comprehensive technical optimization, significantly improving search rankings and conversion rates.
 AI+SNS Social Media Marketing SystemYingbao AI+SNS Social Media Marketing System - Precision social capture for the social media era. Supports one-click content synchronization across major platforms like Facebook and LinkedIn. AI intelligently rewrites posts for enhanced relevance. 24/7 AI customer service and user profiling analysis empower businesses to efficiently expand into global markets.
 AI+SEO营销解决方案易营宝AI+SEO营销解决方案,通过AI批量写作、智能生成TDK、精准关键词扩词等功能,全面优化网站SEO效果,提升流量与转化率。助力企业构建高效智能网站新生态。
 AI+SEM Advertising Marketing SolutionsAI+SEM Advertising Marketing Solution leverages AI technology to deeply empower SEM ad campaigns. It automatically generates weekly/monthly reports using AI, presenting account data across multiple dimensions for comprehensive insights into campaign performance and trends. The system precisely recommends keywords and target countries, intelligently generates high-conversion ad copy, and enables one-click activation of efficient campaign plans to help businesses rapidly acquire customers. Simultaneously, it monitors core metrics in real time, intelligently identifies abnormal fluctuations, and issues timely alerts to ensure stable, high-return advertising results.
 Domain Name ServicesEasyWin provides professional domain name services, including intelligent queries, one-stop registration, brand protection, and full lifecycle management, helping businesses build a digital brand image.
 EasyOperate B2C Cross-Border E-Commerce Platform & Independent WebsiteEasyStore B2C Cross-border E-commerce Independent Store is an intelligent website building and cross-border e-commerce integrated solution independently developed by EasyStore Information Technology (Beijing) Co., Ltd. The system is specially designed for small and medium-sized as well as large export enterprises, integrating 'website building, operation, marketing, advertising, and conversion' into one, helping enterprises quickly establish cross-border e-commerce independent stores to achieve brand globalization and global sales growth.
The platform supports multiple languages, multiple currencies, and multi-channel marketing, with built-in AI intelligent translation and SEO optimization systems, suitable for mainstream markets such as Southeast Asia, Europe and America, Latin America, and the Middle East, assisting Chinese manufacturing enterprises in efficiently deploying international e-commerce strategies. SSL证书易营宝提供专业SSL安全证书服务,包括单域名和泛域名证书,确保网站数据传输加密、身份验证和完整性保护,助力企业建立安全可信的在线业务环境。