









- 21st Century Business Herald: AI and CTV Become Core Growth Engines for Digital Marketing in Overseas MarketsNov 18, 2026View details
- China Presents 25 Cooperation Outcomes in Areas Including Cross-Border E-Commerce During APECNov 18, 2026View details
- AI Products Drive Hong Kong Exports Up 64.9% in September, Fastest Growth in Over 40 YearsNov 17, 2026View details
- National Bureau of Statistics: Foreign trade grew rapidly in October, providing stable support for global tradeNov 17, 2026View details
- The U.S. has ended the $800 de minimis exemption for non-postal shipments; express courier packages must be formally declared.Nov 16, 2026View details
- ASEAN Signs Digital Economy Framework Agreement, Moving Toward Harmonized Cross-Border E-Commerce RulesNov 15, 2026View details
To ensure an international website complies with both GDPR and CCPA, which modules must be restructured?
GDPR and CCPA dual compliance cannot be achieved simply by “adding a pop-up”
When quality control or security teams receive a request to “take the website global,” their first reaction is often: build a multilingual site first, then add a CDN, and finally implement SSL—but what actually delays launch is often the seemingly simplest “privacy pop-up.” Recently, we assisted three manufacturing clients in deploying sites across both the EU and California. Two of them were rejected during third-party compliance audits, with all issues stemming from unsegregated Cookie collection flows, continued backend tracking after users withdrew consent, and misalignment between IP geolocation logic and actual legal jurisdictions. This demonstrates that GDPR/CCPA compliance in international website development is not a frontend UI styling adjustment, but a systematic reconstruction at the data-flow level.
Three high-risk modules that must be restructured
The key to determining whether restructuring is required is whether the current architecture treats “user behavioral data collection” as an unconditional default. Without specialized design, the following modules will almost inevitably trigger regulatory risks:
- Cookie and local storage management module: Article 5 of the GDPR clearly requires that non-essential Cookies may be set only after obtaining explicit, specific, informed, and freely given consent. However, most website-building systems load analytics scripts (such as GA4 and Hotjar) and advertising pixels (Meta Pixel and LinkedIn Insight Tag) by default, without managing them by functional category—meaning that even after a user selects “analytics,” advertising tracking may continue running silently. A more concealed risk is that some CMS platforms hard-code Cookie categorization logic in JS, making it impossible for the server side to identify that a user has withdrawn consent, while subsequent API requests still carry device fingerprint identifiers.
- User consent status synchronization mechanism: The CCPA requires that the “Do Not Sell or Share My Personal Information” option be visible upon the user’s first visit and support persistence across devices and sessions. A common error is storing consent status only in the browser (localStorage/sessionStorage). Once users clear their cache or switch devices, the system automatically resets to “default consent,” effectively circumventing legal obligations. True synchronization requires a server-side identity anchor (such as an anonymized user ID), encrypted status storage, and a real-time policy engine.
- Data collection and transmission paths: Article 44 of the GDPR prohibits transferring personal data to third countries that have not received an EU adequacy decision. Yet many website-building systems send user form submissions, chat records, and behavioral logs to overseas cloud service providers in a unified manner (such as AWS us-east-1 and Google Cloud us-central1), without geographically routing and isolating EU user traffic. An even more easily overlooked issue is that if a frontend tracking SDK calls CDN nodes that are not locally deployed (for example, Cloudflare without EU-only PoP enabled), the X-Forwarded-For field in its request headers may expose the user’s real IP address, constituting an implicit cross-border transfer.
Under what circumstances can restructuring be temporarily deferred?
Not all international websites need to immediately invest in compliance transformation. The following situations may be handled later, but the basis for the risk assessment must be documented in writing:
- A purely informational corporate website (with no forms, no login, and no user interaction), where server logs do not record IP addresses or where IP addresses have been anonymized (such as by truncating the final segment);
- The target market explicitly excludes the EU and California (for example, serving only B2B buyers in Southeast Asia), with access points strictly restricted through a GeoIP database and EU/US IP ranges blocked at the DNS level;
- The existing site has obtained ISO/IEC 27001 certification, and its information security management system documentation explicitly includes provisions for cross-border data transfer controls—in this case, the focus of restructuring should shift to completing the audit evidence chain rather than rewriting code.
It should be noted that skipping compliance design on the grounds of “not collecting user data for now” often results in higher costs when marketing functions are expanded. We once saw a machinery manufacturer add an online inquiry function six months after launch. Because the original architecture had not reserved an interface for consent status validation, the company was forced to suspend operations for two weeks to restructure its core form component.
Restructuring does not mean starting over; it means anchoring on three technical pillars
A truly effective compliance transformation should focus on technical pillars that are verifiable, auditable, and capable of phased rollout, rather than vague “system upgrades”:
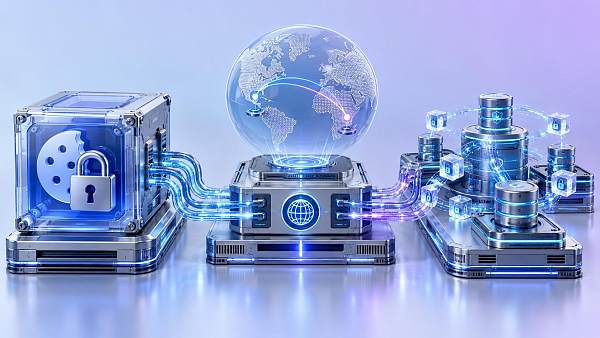
First, a declarative Cookie policy engine: Decouple Cookie categorization (essential/analytics/advertising/preferences) from HTML templates and instead use JSON Schema definitions plus server-side dynamic injection. When a user’s consent status changes, refresh only the JS loader for the corresponding policy group, preventing performance degradation caused by reloading all scripts. This design enables third-party auditors to directly verify consistency between policy configurations and frontend behavior.
Second, a geographically aware data routing gateway: Embed the GeoIP2 database at the reverse proxy layer (such as Nginx or a proprietary gateway) to automatically inject HTTP headers for requests from the EU/CA (such as X-GDPR-Jurisdiction: EU). Backend services then select data storage clusters accordingly (for example, EU user data is written to Frankfurt nodes, while California user data is written to Los Angeles nodes). This solution requires no changes to business code and can be seamlessly integrated with existing CDNs.
Third, a distributed consistency protocol for consent status: Abandon client-side storage and use a lightweight Redis Cluster plus Lua scripts to synchronize status across services. Each user ID generates a unique encrypted Token, whose validity period is tied to the consent validity period (for example, the GDPR requires a maximum of 24 months). Before each read, the server validates the Token signature and timestamp. This mechanism eliminates the risk of browser-side tampering and also meets the CCPA requirement to delete data within 15 days after consent is withdrawn.
Beware of the hidden costs behind “out-of-the-box” solutions
Some SaaS website-building platforms claim to offer “built-in GDPR compliance templates,” but in reality provide only basic pop-up UI and static policy pages. What truly determines compliance effectiveness is whether the underlying data flow supports the three pillars above. For example, although one platform provides multilingual privacy policies, its form submission API does not validate the X-GDPR-Jurisdiction header, causing EU user data to continue flowing into U.S. data centers—this design flaw cannot be remedied through frontend configuration and requires the platform provider to upgrade its API gateway layer.
For clients already using AI website-building systems, it is recommended to first verify whether Cookie policy configuration APIs are available, whether GeoIP routing toggles are supported, and whether consent status Webhook callbacks are provided. The absence of these capabilities means middleware will still need to be developed independently later, which instead increases maintenance complexity. It is worth noting that some professional service providers have consolidated compliance capabilities into independent microservices (such as the Privacy Gateway module of Yiyingbao), enabling clients to integrate with their existing architecture through configuration without modifying their primary website code.
It is noteworthy that the boundaries of compliance restructuring are expanding. The Guidelines on Personalized Advertising recently released by the EU EDPB clearly require that, even if users consent to advertising tracking, platforms must provide an “immediate opt-out” button, and the opt-out action must block all downstream data-sharing flows. This means that merely meeting the basic GDPR/CCPA requirements is only a starting point; genuine risk control requires continuous monitoring of regulatory developments. For example, the “dynamic budget flexibility mechanism” mentioned in Research on Measures to Improve Fiscal Budget Execution Rates for Public Institutions is also applicable to compliance investments—divide a fixed annual budget into baseline compliance (GDPR/CCPA) and dynamic tracking (regulatory updates + judicial precedents) to prevent long-term ineffectiveness after a one-time investment.
The final decision should not depend on “whether compliance has been achieved,” but on “whether compliance can be demonstrated.” When auditors request a complete data destruction log following a particular user’s withdrawal of consent, the ability to quickly produce an audit report with timestamps, operators, and scope of impact is the ultimate manifestation of the value of restructuring.
Related Articles
 New SWIFT rules take effect on November 14: payment messages with fully unstructured addresses will be rejected
 1Password Launches Secure Agent Access Feature: 1Password for Agents
 DebugBear confirms service has been restored following a DNS hijacking incident

Related Products
 Yiyingbao SaaS Intelligent Website Building and Marketing SystemYiyingbao SaaS Intelligent Website Building and Marketing System, AI-powered no-code website building, rapid creation of multilingual B2B international websites in 10 minutes, global server acceleration, AI-powered SEO optimization, helping businesses connect efficiently with global markets. The perfect integration of technology and operation makes building an international trade website remarkably simple
 AI+SEM Intelligent Advertising Marketing SystemAI+SEM drives intelligent ad creation, empowering full-funnel precision advertising marketing. The system automatically generates weekly/monthly reports, AI recommends keywords and target countries, monitors core metrics in real-time with intelligent alerts, and enables one-click high-conversion ad solutions to help quickly acquire customers and improve ROI.
 AI+SEO Dual-Engine System Optimization ServicesYiyingbao’s AI+SEO dual-engine optimization system helps foreign trade enterprises acquire high-quality organic traffic through AI-powered keyword research, content generation, and comprehensive technical optimization, significantly improving search rankings and conversion rates.
 AI+SNS Social Media Marketing SystemYingbao AI+SNS Social Media Marketing System - Precision social capture for the social media era. Supports one-click content synchronization across major platforms like Facebook and LinkedIn. AI intelligently rewrites posts for enhanced relevance. 24/7 AI customer service and user profiling analysis empower businesses to efficiently expand into global markets.
 AI+SEO营销解决方案易营宝AI+SEO营销解决方案,通过AI批量写作、智能生成TDK、精准关键词扩词等功能,全面优化网站SEO效果,提升流量与转化率。助力企业构建高效智能网站新生态。
 AI+SEM Advertising Marketing SolutionsAI+SEM Advertising Marketing Solution leverages AI technology to deeply empower SEM ad campaigns. It automatically generates weekly/monthly reports using AI, presenting account data across multiple dimensions for comprehensive insights into campaign performance and trends. The system precisely recommends keywords and target countries, intelligently generates high-conversion ad copy, and enables one-click activation of efficient campaign plans to help businesses rapidly acquire customers. Simultaneously, it monitors core metrics in real time, intelligently identifies abnormal fluctuations, and issues timely alerts to ensure stable, high-return advertising results.
 Domain Name ServicesEasyWin provides professional domain name services, including intelligent queries, one-stop registration, brand protection, and full lifecycle management, helping businesses build a digital brand image.
 EasyOperate B2C Cross-Border E-Commerce Platform & Independent WebsiteEasyStore B2C Cross-border E-commerce Independent Store is an intelligent website building and cross-border e-commerce integrated solution independently developed by EasyStore Information Technology (Beijing) Co., Ltd. The system is specially designed for small and medium-sized as well as large export enterprises, integrating 'website building, operation, marketing, advertising, and conversion' into one, helping enterprises quickly establish cross-border e-commerce independent stores to achieve brand globalization and global sales growth.
The platform supports multiple languages, multiple currencies, and multi-channel marketing, with built-in AI intelligent translation and SEO optimization systems, suitable for mainstream markets such as Southeast Asia, Europe and America, Latin America, and the Middle East, assisting Chinese manufacturing enterprises in efficiently deploying international e-commerce strategies. SSL证书易营宝提供专业SSL安全证书服务,包括单域名和泛域名证书,确保网站数据传输加密、身份验证和完整性保护,助力企业建立安全可信的在线业务环境。









