









Related recommendations
- The U.S. has ended the $800 de minimis exemption for non-postal shipments; express courier packages must be formally declared.Nov 16, 2026View details
- ASEAN Signs Digital Economy Framework Agreement, Moving Toward Harmonized Cross-Border E-Commerce RulesNov 15, 2026View details
- Shenzhen Becomes the First City in Mainland China to Exceed RMB 5 Trillion in Foreign TradeNov 15, 2026View details
- Fujian Announces the First Batch of Provincial-Level Cross-Border E-Commerce Industrial Parks and Key Brands for CultivationNov 14, 2026View details
- Amazon Global Store Announces the Launch of the 2026 Black Friday Global Shopping SeasonNov 14, 2026View details
- CCTV.com Examines APEC’s Role in China’s Foreign TradeNov 12, 2026View details
In B2C standalone website development, how significant is the difference in payment compliance costs between Shopify and self-built websites?
Publish date:Sep 26, 2026
Author:Easy Yingbao (Eyingbao)
Page views:
In B2C standalone website development, differences in payment compliance costs far exceed the apparent fees! Shopify involves numerous hidden expenses, while self-built websites provide greater risk control, reduce chargebacks, and enable faster settlement—an in-depth breakdown of the actual cost structure.
Inquire now : 4006552477
In B2C standalone website development, payment compliance costs are often underestimated—Shopify may seem hassle-free, but hidden fees and regional restrictions occur frequently; while self-built websites require technical investment, they make it easier to achieve localized acquiring and GDPR/PCI DSS compliance. How should procurement professionals balance short-term costs against long-term risk control? This article does not discuss concepts; it only breaks down the actual cost structure: from integration thresholds, annual fee allocation, exchange-rate losses, and chargeback response, to audit response speed and cross-border fund repatriation cycles.
You may have just received an email from the finance department: “Last quarter, Shopify payment processing fees + currency conversion fees + chargeback handling fees exceeded the budget by 37%.” Or perhaps you have been staring late at night at a back-end notification stating, “Stripe has suspended registration for new merchants in Germany.” These are not coincidences; they are the most silent yet most painful cost gaps in the payment chain during the global expansion of B2C standalone websites.
Shopify’s “out-of-the-box” approach is essentially a closed ecosystem governed by preset rules. It packages major global payment gateways (PayPal, Stripe, Adyen) into its back end, but when it comes to actual implementation, you will find that Stripe does not support local credit card BIN ranges in Brazil; Shopify Payments cannot connect directly to local bank clearing systems in France; and Japanese consumers using Konbini convenience-store payments require an additional contract with a third-party service provider, with an extra 1.8% service fee charged per transaction. These are not bugs; they are the real reflection of the platform’s capability boundaries.
The payment architecture of a self-built website, on the other hand, is more like a vascular system tailored to a brand. You can choose to connect with locally licensed acquiring institutions (such as direct JCB integration in Japan or STC Pay in the Middle East), or integrate redundant multi-channel options as needed—using Stripe as the primary channel, Adyen as a backup, and automatically switching high-risk countries to local wallets (such as ShopeePay in Southeast Asia and Mercado Pago in Latin America). This is not technical showmanship; it ensures that every order is already aligned with the local regulatory context before entering the risk-control engine: Has PSD2 strong authentication been completed? Does it meet Brazil’s PIX real-time settlement requirements? Has it passed Singapore MAS anti-money-laundering look-through testing?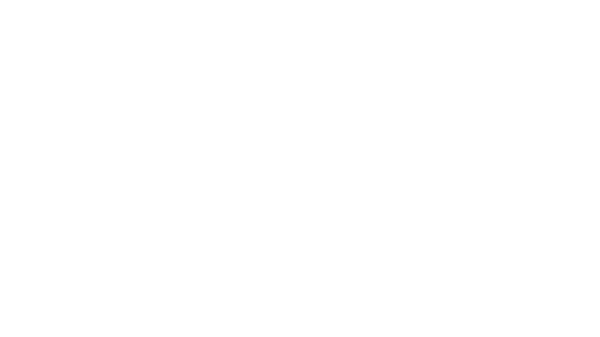 Compliance costs have never been simply about “whether you have a certificate.” They are reflected in three categories of explicit expenses:
The first category is annual licensing and certification fees. Shopify merchants share its PCI DSS Level 1 qualification by default, but if you sell medical-grade beauty devices or lithium-battery products, EU MDR or UN38.3 compliance must be declared separately. This portion is borne by merchants themselves; Shopify neither manages nor guarantees it. A self-built website, however, can embed compliance documents at the payment SDK layer, allowing a single configuration to be reused across all regions.
The second category is chargeback management costs. Shopify provides basic chargeback dispute templates, but when European and U.S. consumers initiate chargebacks, local-language legal documents, original bank statements, and proof of delivery acceptance are often required. A self-built website can connect ERP and logistics APIs to automatically consolidate the evidence chain, reducing the average response time by 62%—which is crucial for lowering secondary chargeback rates.
The third category is fund retention and payment collection delays. Shopify has a standard settlement cycle of 14 days (up to 21 days in some countries), during which funds are frozen in the platform account and cannot be used for local tax payments or reinvestment in marketing. A self-built website can instead define multi-currency split-settlement logic: euro orders are paid directly into a local German account, while U.S. dollar orders are routed through a U.S. subsidiary, avoiding foreign-exchange controls while reducing funds-in-transit time.
Of course, a self-built website does not have a zero threshold. It requires the procurement team to assess three points: first, technical delivery capability—whether it can continuously maintain SSL certificates, regularly update PCI compliance scans, and respond to payment gateway API changes; second, a localized service network—whether it can quickly connect with licensed institutions in target markets and complete KYC reviews; third, long-term ROI measurement dimensions—whether it incorporates “a 5% reduction in payment failure rate,” “reducing the chargeback rate to below 0.8%,” and “shortening the collection cycle from 14 days to 3 days” into procurement KPIs.
A Zhejiang small-appliance brand served by Yiyingbao increased its payment success rate in the German market from 81% to 94% after shifting to a self-built website payment architecture, reduced its chargeback rate from 2.3% to 0.7%, and saved hidden costs each month equivalent to funding two additional Google Shopping ad campaigns. This was not achieved by simply adding manpower, but through the GEO generation engine built into its cloud intelligent website-building system, which automatically identifies a visitor’s IP location and dynamically loads payment components matching that country’s regulatory requirements—for example, prioritizing Satispay for Italian users and enabling the Mada card channel by default for users in the UAE.
It is worth noting that payment compliance is not a static, one-time action. Starting in 2024, the EU will mandate secondary verification under SCA (Strong Customer Authentication), the Bank of Thailand requires all cross-border payment recipients to complete BOT registration, and new SAMA regulations in Saudi Arabia explicitly prohibit unlicensed institutions from processing local bank card transactions. Shopify will push these changes as “back-end update notifications,” but the implementation timeline depends on the platform’s schedule; under a self-built website architecture, your technical team or service provider can complete adaptation 30 days before the regulation takes effect.
The essence of procurement decisions is finding a balance between certainty and flexibility. Shopify is like a mass-produced car with navigation and a sound system preinstalled, suitable for getting on the road quickly; a self-built website is more like a customized off-road vehicle with a modifiable chassis, replaceable engine, and optional off-road kit—its initial investment is slightly higher, but when traversing complex terrain, chassis strength, fuel compatibility, and maintenance response speed all directly determine whether you can reach the destination.
Finally, here is an easily overlooked detail: when your B2C standalone website begins accepting government procurement orders (for example, educational equipment sold to public schools or security systems delivered for local government projects), the payment chain must also meet public financial fund supervision requirements. At this point, a back-end split-settlement module that can connect with the financial and accounting supervision system for administrative institutions is no longer an advantage, but an entry requirement. Research on Optimization Strategies for the Financial and Accounting Supervision System of Administrative Institutions points out that visualized fund flows, traceable voucher chains, and standardized audit interfaces are becoming new compliance baselines for cross-border B2G/B2C hybrid scenarios.
So, back to the original question: How significant is the difference in payment compliance costs between Shopify and self-built websites? The answer lies not in the figures themselves, but in how much premium you are willing to pay for certainty and how much room for flexibility you are willing to reserve for control. After all, the real cost is never the number on the invoice, but the portion of risk-related loss you cannot see.
Related Articles
 How Should New Energy Companies Choose Target Markets for Overseas Promotion?
 Which businesses are suited to Easysite’s Creative Factory model?
 JD Logistics Launches an Integrated Supply Chain Solution for Overseas Independent Websites
{item.title}
Related Products
 Yiyingbao SaaS Intelligent Website Building and Marketing SystemYiyingbao SaaS Intelligent Website Building and Marketing System, AI-powered no-code website building, rapid creation of multilingual B2B international websites in 10 minutes, global server acceleration, AI-powered SEO optimization, helping businesses connect efficiently with global markets. The perfect integration of technology and operation makes building an international trade website remarkably simple
 AI+SEM Intelligent Advertising Marketing SystemAI+SEM drives intelligent ad creation, empowering full-funnel precision advertising marketing. The system automatically generates weekly/monthly reports, AI recommends keywords and target countries, monitors core metrics in real-time with intelligent alerts, and enables one-click high-conversion ad solutions to help quickly acquire customers and improve ROI.
 AI+SEO Dual-Engine System Optimization ServicesYiyingbao’s AI+SEO dual-engine optimization system helps foreign trade enterprises acquire high-quality organic traffic through AI-powered keyword research, content generation, and comprehensive technical optimization, significantly improving search rankings and conversion rates.
 AI+SNS Social Media Marketing SystemYingbao AI+SNS Social Media Marketing System - Precision social capture for the social media era. Supports one-click content synchronization across major platforms like Facebook and LinkedIn. AI intelligently rewrites posts for enhanced relevance. 24/7 AI customer service and user profiling analysis empower businesses to efficiently expand into global markets.
 AI+SEO营销解决方案易营宝AI+SEO营销解决方案,通过AI批量写作、智能生成TDK、精准关键词扩词等功能,全面优化网站SEO效果,提升流量与转化率。助力企业构建高效智能网站新生态。
 AI+SEM Advertising Marketing SolutionsAI+SEM Advertising Marketing Solution leverages AI technology to deeply empower SEM ad campaigns. It automatically generates weekly/monthly reports using AI, presenting account data across multiple dimensions for comprehensive insights into campaign performance and trends. The system precisely recommends keywords and target countries, intelligently generates high-conversion ad copy, and enables one-click activation of efficient campaign plans to help businesses rapidly acquire customers. Simultaneously, it monitors core metrics in real time, intelligently identifies abnormal fluctuations, and issues timely alerts to ensure stable, high-return advertising results.
 Domain Name ServicesEasyWin provides professional domain name services, including intelligent queries, one-stop registration, brand protection, and full lifecycle management, helping businesses build a digital brand image.
 EasyOperate B2C Cross-Border E-Commerce Platform & Independent WebsiteEasyStore B2C Cross-border E-commerce Independent Store is an intelligent website building and cross-border e-commerce integrated solution independently developed by EasyStore Information Technology (Beijing) Co., Ltd. The system is specially designed for small and medium-sized as well as large export enterprises, integrating 'website building, operation, marketing, advertising, and conversion' into one, helping enterprises quickly establish cross-border e-commerce independent stores to achieve brand globalization and global sales growth.
The platform supports multiple languages, multiple currencies, and multi-channel marketing, with built-in AI intelligent translation and SEO optimization systems, suitable for mainstream markets such as Southeast Asia, Europe and America, Latin America, and the Middle East, assisting Chinese manufacturing enterprises in efficiently deploying international e-commerce strategies. SSL证书易营宝提供专业SSL安全证书服务,包括单域名和泛域名证书,确保网站数据传输加密、身份验证和完整性保护,助力企业建立安全可信的在线业务环境。









