- EU Plans to Raise Tax on Incoming Small Parcels to €5Oct 31, 2026View details
- Maersk Adjusts Middle East Emergency Operating Cost Recovery Surcharge to USD 2,000 per ContainerOct 30, 2026View details
- Ministry of Commerce: Online retail sales grew 4.4% in the first three quarters, while cross-border e-commerce maintained relatively rapid growthOct 29, 2026View details
- CCTV reports: AI-powered smart hardware is expanding overseas at a faster pace, with orders for some best-selling products booked through next yearOct 29, 2026View details
- Alphabet Q3 Earnings: Google Search Advertising Revenue Rises 10.5% to $82 BillionOct 29, 2026View details
- AliExpress Announces New Service Rules for Russia, Linked to Wildberries Product IntegrationOct 28, 2026View details
Is a paid SSL certificate worth the extra cost compared with a free one?
When evaluating the cost of an SSL certificate (SSL certificate cost), don’t look only at the price on the purchase order. If both free and paid certificates enable a website to use HTTPS, why are some free while others require ongoing payment? For business professionals responsible for website development and overseas marketing budgets, the real question is: What does the extra money buy, and can it reduce business risk?
The conclusion: A paid certificate does not necessarily provide stronger encryption, but it may offer organization identity validation, technical support, and clearer service responsibilities. Whether it is worth buying depends on the website’s purpose, customer requirements, and who is responsible for ongoing maintenance.
First, distinguish between encryption and commercial services: they are two separate considerations
What is commonly called an SSL certificate is actually used for modern TLS connections. When the algorithms, keys, and server configuration are comparable, both browser-trusted free certificates and paid certificates can protect data in transit. It is not accurate to assume that “the higher the price, the safer the information.”
There are three main types of certificate validation. When making a purchase, check the scope of validation first, then the price.
Browsers generally do not prominently display a company name in the address bar just because a website uses an OV or EV certificate. Therefore, “buying a higher-level certificate will noticeably increase inquiries” is not a reliable basis for budgeting.
SSL certificate cost: What is easy to overlook in the total cost?
The certificate quote is only the starting point. Business evaluations should consider the certificate fee, deployment fee, renewal and maintenance fees, and troubleshooting costs together. If a website platform automatically issues and renews a free certificate, the day-to-day management burden may be low. Conversely, even a paid certificate can lead to access warnings if it expires because it was not deployed and monitored properly.
At a minimum, verify these four items on the purchase order:
- Coverage: Are the main domain, www address, online store, and other subdomains included? How are additional domains charged?
- Deployment location: Does coverage apply only to the CDN entry point, or does it also include the origin server, load balancers, and other links that need encryption?
- Maintenance responsibilities: Who is responsible for renewals, installation, validation, and alerts? Does support continue after a domain or server migration?
- Service terms: Are response times, support languages, reissuance policies, and paid renewal terms specified in the contract?
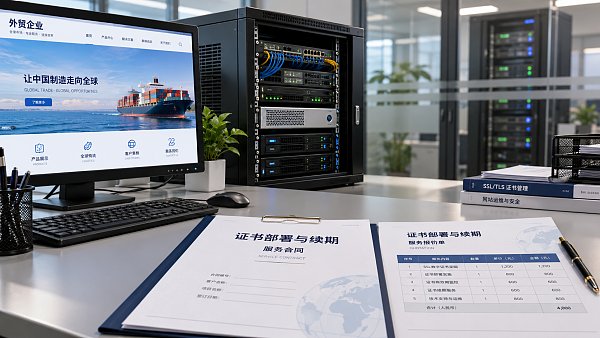
Do not equate “a certificate is valid” with “someone will maintain it throughout its validity period.” Some paid plans provide liability coverage, but the covered parties, triggering conditions, exclusions, and claims procedures vary. This does not mean you will be compensated if your website is attacked or orders are affected.
When is a paid option worth it, and when can you start with a free one?
If a company is building an export-focused showcase website that mainly receives traffic from Google search, advertising, and social media, and the platform provides reliable automatic renewal and alerts with no additional identity verification requirements, a trusted free DV certificate will usually meet its data encryption needs. The savings can be prioritized for website speed, multilingual content, and inquiry workflows.
For companies operating multiple websites, subject to organizational identity verification requirements, or without technical staff, paid options are more worth considering. In these cases, however, the main purchase may not be the certificate itself, but the assurance that “someone is responsible”: post-deployment verification, handling failed renewals, and responding to incidents across time zones.
An online store serving cross-border customers does not need to choose the most expensive certificate just because it processes payments. The decision should be based on the rules of payment providers, data processing practices, and applicable compliance requirements. A certificate cannot replace payment security, backend access controls, vulnerability remediation, or data protection.
Another common misconception among corporate websites is upgrading certificate levels for SEO. HTTPS is a basic website configuration, but there is no reliable evidence that a paid certificate or a higher validation level by itself provides an additional ranking advantage. What really needs to be avoided is an expired certificate, faulty HTTPS redirects, or mixed content that creates obstacles when users visit the website or submit a form.
Instead of asking “How much does the certificate cost?”, ask “What does this quote include?”
When choosing an integrated website and marketing service, evaluate the certificate alongside website development and maintenance. For example, when discussing EasyYingbao’s smart website development, multilingual websites, and overseas marketing services, confirm whether the quote includes a certificate, which domains it covers, who is responsible for renewals, and how things will be adjusted if the website is migrated or an online store is added. Do not assume that every service is included just because a provider calls its offering “one-stop.”
Budget management can also draw on the performance-based approach outlined in Strategies for Applying Budget Performance Management in Financial Management at Public Institutions: link expenditure to results that can be verified. For SSL procurement, this means moving beyond “we bought a certificate” and checking that “HTTPS is correctly enabled on the specified domains, renewal responsibilities are clear, and someone will handle issues.”
Ask suppliers to list the basic plan and paid upgrade separately, and explain what additional validation, support, or management capabilities the upgrade provides. If the difference amounts only to a brand name or a vague claim of being “more secure,” that is not enough to justify the extra cost.
The extra cost of a paid SSL certificate should correspond to genuine needs and clearly defined deliverables. If a free option runs reliably, there is no need to upgrade just because of its price tag. Pay for additional services when identity verification, contractual requirements, or maintenance responsibilities genuinely call for them. For a business, choosing the right certificate matters—but keeping the website secure and reliably accessible matters more.
Related Articles
 How Can Cross-Border E-Commerce Analytics Tools Track Orders Generated by Ads?
 How Can You Compare the Stability of Global Acceleration Networks for Cross-Border E-Commerce Platforms?
 What Should Guangdong Businesses Look for in an Export-Focused Independent Website Provider?
Related Products
 Yiyingbao SaaS Intelligent Website Building and Marketing SystemYiyingbao SaaS Intelligent Website Building and Marketing System, AI-powered no-code website building, rapid creation of multilingual B2B international websites in 10 minutes, global server acceleration, AI-powered SEO optimization, helping businesses connect efficiently with global markets. The perfect integration of technology and operation makes building an international trade website remarkably simple
 AI+SEM Intelligent Advertising Marketing SystemAI+SEM drives intelligent ad creation, empowering full-funnel precision advertising marketing. The system automatically generates weekly/monthly reports, AI recommends keywords and target countries, monitors core metrics in real-time with intelligent alerts, and enables one-click high-conversion ad solutions to help quickly acquire customers and improve ROI.
 AI+SEO Dual-Engine System Optimization ServicesYiyingbao’s AI+SEO dual-engine optimization system helps foreign trade enterprises acquire high-quality organic traffic through AI-powered keyword research, content generation, and comprehensive technical optimization, significantly improving search rankings and conversion rates.
 AI+SNS Social Media Marketing SystemYingbao AI+SNS Social Media Marketing System - Precision social capture for the social media era. Supports one-click content synchronization across major platforms like Facebook and LinkedIn. AI intelligently rewrites posts for enhanced relevance. 24/7 AI customer service and user profiling analysis empower businesses to efficiently expand into global markets.
 AI+SEO营销解决方案易营宝AI+SEO营销解决方案,通过AI批量写作、智能生成TDK、精准关键词扩词等功能,全面优化网站SEO效果,提升流量与转化率。助力企业构建高效智能网站新生态。
 AI+SEM Advertising Marketing SolutionsAI+SEM Advertising Marketing Solution leverages AI technology to deeply empower SEM ad campaigns. It automatically generates weekly/monthly reports using AI, presenting account data across multiple dimensions for comprehensive insights into campaign performance and trends. The system precisely recommends keywords and target countries, intelligently generates high-conversion ad copy, and enables one-click activation of efficient campaign plans to help businesses rapidly acquire customers. Simultaneously, it monitors core metrics in real time, intelligently identifies abnormal fluctuations, and issues timely alerts to ensure stable, high-return advertising results.
 Domain Name ServicesEasyWin provides professional domain name services, including intelligent queries, one-stop registration, brand protection, and full lifecycle management, helping businesses build a digital brand image.
 EasyOperate B2C Cross-Border E-Commerce Platform & Independent WebsiteEasyStore B2C Cross-border E-commerce Independent Store is an intelligent website building and cross-border e-commerce integrated solution independently developed by EasyStore Information Technology (Beijing) Co., Ltd. The system is specially designed for small and medium-sized as well as large export enterprises, integrating 'website building, operation, marketing, advertising, and conversion' into one, helping enterprises quickly establish cross-border e-commerce independent stores to achieve brand globalization and global sales growth.
The platform supports multiple languages, multiple currencies, and multi-channel marketing, with built-in AI intelligent translation and SEO optimization systems, suitable for mainstream markets such as Southeast Asia, Europe and America, Latin America, and the Middle East, assisting Chinese manufacturing enterprises in efficiently deploying international e-commerce strategies. SSL证书易营宝提供专业SSL安全证书服务,包括单域名和泛域名证书,确保网站数据传输加密、身份验证和完整性保护,助力企业建立安全可信的在线业务环境。