









- AliExpress Global Double 11: Brand Sales Grow Nearly 50% in the First Week, U.S. GMV Rises 70%Nov 21, 2026View details
- Ministry of Commerce Reports E-commerce Development from January to October 2026, with Cross-Border Imports Performing StronglyNov 21, 2026View details
- Amazon Black Friday Orders Sluggish on Day One; NRF Forecasts 4.2 Million Fewer ParticipantsNov 21, 2026View details
- 21st Century Business Herald: AI and CTV Become Core Growth Engines for Digital Marketing in Overseas MarketsNov 18, 2026View details
- China Presents 25 Cooperation Outcomes in Areas Including Cross-Border E-Commerce During APECNov 18, 2026View details
- AI Products Drive Hong Kong Exports Up 64.9% in September, Fastest Growth in Over 40 YearsNov 17, 2026View details
How do you evaluate payment integration capabilities in B2C online store development services?
When evaluating the payment integration capabilities of b2c online store development services, don’t focus solely on how many payment methods a provider lists. Technical evaluators need to verify whether customers in the target markets can pay smoothly, whether payment results are reliably synchronized with orders, and whether refunds, chargebacks, and reconciliation can be incorporated into day-to-day operations. A payment page that opens does not necessarily mean the store can process transactions end to end.
Define the transaction scenario first, then verify the payment methods
Ask the provider to propose payment options based on the target sales regions, merchant entity, transaction currencies, and product types. During evaluation, distinguish three questions that are often conflated: which payment methods customers use, which currencies are displayed on the page, and which currencies the merchant ultimately receives in settlement. A website’s ability to display multiple currencies does not mean the payment provider supports accepting or settling payments in those currencies.
Payment methods should also be assessed in light of customer preferences and the merchant’s actual eligibility to access them. For example, when selling in multiple regions, businesses may need locally popular wallets or other payment methods in addition to international bank cards. But if a business sells in only one region, enabling the main local payment methods is usually more valuable than pursuing a long list of options. For subscriptions, presales, or installment payments, confirm separately that both the payment provider and the store support the relevant transaction flows.
Ask the provider to clarify who applies for and holds the payment account, what merchant documentation is required for integration, and what alternatives are available if the account application is rejected. A development provider’s ability to call an API does not mean the merchant is necessarily eligible to use the payment service.
Check the integration across the order lifecycle, not just a successful payment demo
The key to payment integration is ensuring that the store, payment provider, and operations backend agree on the same transaction. During evaluation, ask the provider to demonstrate the complete flow—from order creation and payment initiation through receipt of the payment result, refunds, and reconciliation—and explain which system is responsible for the data at each step.
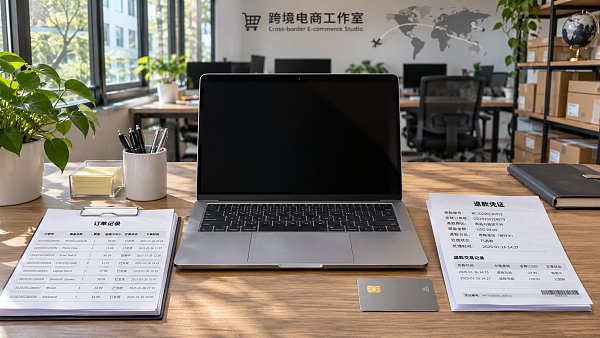
Pay particular attention to asynchronous result handling. If a customer closes the page, the network connection is interrupted, or a payment notification is delayed, the store must not rely solely on a browser redirect to determine that an order has been paid. The system needs to update the order status based on notifications from the payment provider and transaction query results, and handle duplicate notifications to prevent duplicate shipments or other business actions from being executed more than once.
For statuses such as pending payment, payment failed, paid, partially refunded, and fully refunded, the provider should explain how each status changes and who handles exceptional orders. This is especially important for payment methods such as bank transfers, where confirmation may be delayed. If only payment methods with instant confirmation are supported, the process can be simpler, but it should still cover timeouts and duplicate submissions.
A refund demonstration should go beyond clicking a button in the backend. Technical staff should verify that the refund request is sent to the payment provider, the result is reflected in the order, how partial refunds are recorded, and how failed refunds can be retried or handled manually. If the business supports split shipments or multiple partial refunds, test those scenarios as well.
Assess whether the solution can be operated by clarifying security responsibilities
Ask the provider to map the payment data flow: where customers enter their payment details, which systems communicate with the browser, what data the store server retains, and whether logs could capture sensitive information. Using a payment page or component hosted by the payment provider can reduce the store’s direct exposure to sensitive payment information, but it does not eliminate the store’s own responsibilities for access control, data protection, and configuration.
The security assessment should also cover the storage and rotation of API credentials, backend access permissions, verification of payment notification sources, encryption in transit, and records of unusual activity. The parties should clearly define their respective responsibilities and the evidence to be delivered for applicable payment security standards and data protection requirements in the target markets. If the solution requires the store to handle sensitive card data itself, the technical and operational responsibilities are typically greater, so assess whether the team has the necessary capabilities.
Risk management also depends on clearly defined responsibilities: what risk signals the payment provider can supply, whether the store can pause fulfillment based on business rules, and how manual review decisions are recorded. Overly strict blocking can affect legitimate orders, while relying entirely on manual review is unsuitable for high-volume operations. Set up a process that reflects the risks associated with the products and the resources available for operations.
When comparing providers, consider demos, deliverables, and responsibilities together
Reconciliation must link store orders, payment transactions, and settlement records. In particular, ask how fees, refunds, and chargebacks appear in the records, and whether discrepancies can be traced to specific transactions. Data fields and statement cycles may differ between systems, and being able to export reports does not mean reconciliation has been completed.
If a cross-border store also relies on website development, traffic acquisition, and operational services, confirm how payment issues are reported to the team responsible for conversion analysis. This helps prevent payment failures from being misattributed to advertising or landing-page issues. 易营宝 provides cross-border commerce and overseas marketing services; when considering this type of platform, payment channels, transaction flows, and specific deliverables should still be assessed individually for each project.
Complete acceptance testing with exception scenarios before launch
Select an order that represents a primary sales path and, in a test environment, complete a payment, verify status updates, and check refund and reconciliation records. Then test exceptions such as interrupted payments, duplicate notifications, delayed notifications, and failed refunds. For steps that cannot be fully simulated in the test environment, agree on post-launch monitoring methods and the people responsible for handling them.
The final choice should be based on whether the provider can propose payment options that can be integrated in the target markets, demonstrate that transaction statuses remain traceable under exceptional conditions, and clearly define post-launch maintenance responsibilities. Payment integration has actionable evaluation criteria only when these items are included in the scope of delivery and acceptance.
Related Articles
 How do you evaluate payment integration capabilities in B2C online store development services?
 How can you tell whether a landing page development company has the expertise to optimize conversions?
 How Can a Digital Marketing Service Company Evaluate Inquiry Conversion Performance?
Related Products
 Yiyingbao SaaS Intelligent Website Building and Marketing SystemYiyingbao SaaS Intelligent Website Building and Marketing System, AI-powered no-code website building, rapid creation of multilingual B2B international websites in 10 minutes, global server acceleration, AI-powered SEO optimization, helping businesses connect efficiently with global markets. The perfect integration of technology and operation makes building an international trade website remarkably simple
 AI+SEM Intelligent Advertising Marketing SystemAI+SEM drives intelligent ad creation, empowering full-funnel precision advertising marketing. The system automatically generates weekly/monthly reports, AI recommends keywords and target countries, monitors core metrics in real-time with intelligent alerts, and enables one-click high-conversion ad solutions to help quickly acquire customers and improve ROI.
 AI+SEO Dual-Engine System Optimization ServicesYiyingbao’s AI+SEO dual-engine optimization system helps foreign trade enterprises acquire high-quality organic traffic through AI-powered keyword research, content generation, and comprehensive technical optimization, significantly improving search rankings and conversion rates.
 AI+SNS Social Media Marketing SystemYingbao AI+SNS Social Media Marketing System - Precision social capture for the social media era. Supports one-click content synchronization across major platforms like Facebook and LinkedIn. AI intelligently rewrites posts for enhanced relevance. 24/7 AI customer service and user profiling analysis empower businesses to efficiently expand into global markets.
 AI+SEO营销解决方案易营宝AI+SEO营销解决方案,通过AI批量写作、智能生成TDK、精准关键词扩词等功能,全面优化网站SEO效果,提升流量与转化率。助力企业构建高效智能网站新生态。
 AI+SEM Advertising Marketing SolutionsAI+SEM Advertising Marketing Solution leverages AI technology to deeply empower SEM ad campaigns. It automatically generates weekly/monthly reports using AI, presenting account data across multiple dimensions for comprehensive insights into campaign performance and trends. The system precisely recommends keywords and target countries, intelligently generates high-conversion ad copy, and enables one-click activation of efficient campaign plans to help businesses rapidly acquire customers. Simultaneously, it monitors core metrics in real time, intelligently identifies abnormal fluctuations, and issues timely alerts to ensure stable, high-return advertising results.
 Domain Name ServicesEasyWin provides professional domain name services, including intelligent queries, one-stop registration, brand protection, and full lifecycle management, helping businesses build a digital brand image.
 EasyOperate B2C Cross-Border E-Commerce Platform & Independent WebsiteEasyStore B2C Cross-border E-commerce Independent Store is an intelligent website building and cross-border e-commerce integrated solution independently developed by EasyStore Information Technology (Beijing) Co., Ltd. The system is specially designed for small and medium-sized as well as large export enterprises, integrating 'website building, operation, marketing, advertising, and conversion' into one, helping enterprises quickly establish cross-border e-commerce independent stores to achieve brand globalization and global sales growth.
The platform supports multiple languages, multiple currencies, and multi-channel marketing, with built-in AI intelligent translation and SEO optimization systems, suitable for mainstream markets such as Southeast Asia, Europe and America, Latin America, and the Middle East, assisting Chinese manufacturing enterprises in efficiently deploying international e-commerce strategies. SSL证书易营宝提供专业SSL安全证书服务,包括单域名和泛域名证书,确保网站数据传输加密、身份验证和完整性保护,助力企业建立安全可信的在线业务环境。









