









- 21st Century Business Herald: AI and CTV Become Core Growth Engines for Digital Marketing in Overseas MarketsNov 18, 2026View details
- China Presents 25 Cooperation Outcomes in Areas Including Cross-Border E-Commerce During APECNov 18, 2026View details
- AI Products Drive Hong Kong Exports Up 64.9% in September, Fastest Growth in Over 40 YearsNov 17, 2026View details
- National Bureau of Statistics: Foreign trade grew rapidly in October, providing stable support for global tradeNov 17, 2026View details
- The U.S. has ended the $800 de minimis exemption for non-postal shipments; express courier packages must be formally declared.Nov 16, 2026View details
- ASEAN Signs Digital Economy Framework Agreement, Moving Toward Harmonized Cross-Border E-Commerce RulesNov 15, 2026View details
How Can Corporate International Website Development Meet Overseas Privacy Compliance Requirements?
How Can International Corporate Website Development Meet Overseas Privacy Compliance Requirements
International corporate website development may appear to be a matter of multilingual pages, product displays, and overseas customer acquisition. However, once a website goes live, another often-overlooked risk frequently emerges: whether user data is collected, used, shared, and transferred in compliance with applicable requirements. Particularly for websites targeting markets such as Europe and North America, Cookie pop-ups, inquiry forms, advertising pixels, email subscriptions, and online customer service may all involve the processing of personal information. For quality control and security management personnel, a corporate website should not be merely a “display asset” of the marketing department, but should also be incorporated into an auditable and traceable scope of data processing.
Many companies only review their websites after their advertising accounts are restricted, customers request supplementary explanations of data processing, or they receive data deletion requests. At that point, they often find that their forms collect too many fields, third-party scripts are unmanaged, privacy policies do not match actual functions, and even different language versions of the website use the same set of unsuitable notice texts. Overseas privacy compliance is not completed simply by adding a statement at the bottom of a website; page functions, technical configurations, and internal processes must align with one another.
First Define the Boundaries: What Data Does the Website Actually Process?
Companies should first prepare a lightweight yet complete data inventory. Do not focus only on names, email addresses, and phone numbers. IP addresses, device identifiers, Cookie identifiers, browsing paths, form submission times, and marketing source parameters may all constitute personal data or data related to individuals under specific legal frameworks and usage scenarios. When a website uses Google Analytics, ad conversion tracking, remarketing tags, map components, online videos, or live chat tools, data flows are often more complex than website administrators may expect.
During an actual review, records can be made according to four items: “entry point—purpose—recipient—retention period.” For example, an inquiry form may collect the contact's name, company, email address, and description of needs for the purpose of responding to business inquiries. If the data is synchronized with a CRM, email marketing system, or sales personnel's email inbox, the recipients and processing methods should also be specified. This does not increase documentation burdens, but rather provides a basis for subsequent privacy policies, consent mechanisms, and the handling of deletion requests.
The Key to Cookie Management Is Not the “Pop-up,” but Whether Scripts Are Truly Controlled
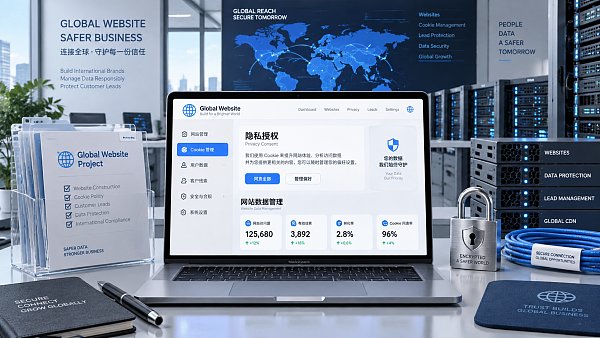
Common requirements in the European market stem from the General Data Protection Regulation (GDPR) and local rules on storing and accessing information on terminal devices. Companies should not treat “continued browsing constitutes consent” as a universal solution, nor should they provide only “Accept” without an option to reject or make granular selections. The more practical challenge is whether advertising, analytics, or social media tracking scripts have already loaded before the user has made a choice.
Quality control personnel should have the technical team conduct a script verification: what is loaded during a browser's first visit; whether tracking requests remain after a user rejects non-essential Cookies; whether subsequent tracking can be stopped after consent is withdrawn; and whether landing pages in different languages and regions use the same set of control rules. Cookie categories displayed on the page must correspond to the actual scripts; otherwise, even the most sophisticated pop-up will not withstand an audit. The categorization of necessary Cookies, statistical Cookies, and marketing Cookies can serve as a management starting point, but specific classifications must still be confirmed based on vendor documentation and the website's actual deployment.
Form Design Should Follow the Principles of “Collect Less, Explain Clearly, and Enable Deletion”
A common misunderstanding on overseas B2B websites is to directly apply domestic sales practices to international websites: requiring users to provide mobile numbers, job titles, countries, purchasing budgets, detailed addresses, or even upload identification or qualification documents. For an initial inquiry, these fields may not all be directly relevant to responding to the request. Instead, they may reduce willingness to submit and increase the company's responsibility for safeguarding data.
A more prudent approach is to limit the information required for initial communication to a reasonable scope, and use concise language near the submit button to explain the processing purpose, privacy policy access point, and contact channels. If a company wishes to send product catalogs, industry updates, or promotional emails, it should avoid hiding “consent to receive marketing information” in a pre-selected checkbox. Downloading materials, responding to quotations, and long-term marketing are different processing purposes, and internal systems should also be able to distinguish between them.
Taking an agricultural product export website as an example, a customized packaging application form may need to collect purchasing specifications, the target market, and contact information. The page may use natural storytelling and large images, but visual presentation must not obscure data notices. For website solutions such as agriculture, agricultural products, and food, which emphasize product texture, service commitments, and customized applications, particular attention should be given to where data goes after form submission and whether the newsletter subscription module is mixed with inquiry data.
Cross-Border Transfers Are Not a Technical Term, but a Chain of Responsibility
Data from international websites generally does not remain solely on the website server. Website hosting platforms, CDNs, analytics tools, customer service systems, CRMs, email service providers, and advertising platforms may all participate in processing. For businesses serving EU users, data transfer arrangements need to be assessed in conjunction with the location from which data is exported, the recipient's location, the services used, and contractual documents. Simply because a service provider is “overseas” or uses cloud services does not automatically mean that transfer arrangements are appropriate.
Security management personnel should at least understand three issues: in which regions data is stored; which vendors can access or process the data; and whether data can be located and acted upon across all systems when a data subject submits an access, correction, or deletion request. If website operations involve the marketing team, website development service providers, and external advertising agencies, companies must also avoid a situation where “anyone can export leads, while no one can clearly explain how long the data is retained.” Role-based permissions, operation logs, recovery of accounts belonging to departing employees, and export restrictions often reduce actual risks more effectively than a general policy.
Multilingual Content Must Not Only Be Translated; Regional Rules Must Also Be Implemented
International corporate website development often adopts a “single backend, multilingual frontend” approach. There is nothing inherently wrong with this, but privacy content cannot simply be machine-translated and reused across the entire website. Requirements for notices, consent, protection of minors, marketing contacts, and consumer rights are not entirely the same across different markets. For the U.S. market, companies should also pay attention to privacy rules in applicable states and the specific meanings of concepts such as “sale” and “sharing” in advertising technology. For markets in Japan, South Korea, the Middle East, or Latin America, further assessments are required based on local laws, business entities, and user sources.
The most common discrepancy here is that the English privacy policy is comprehensive, while the actual Chinese backend lacks corresponding operational capabilities; or European pages allow users to manage preferences, but advertising landing pages, campaign pages, and social media redirect pages bypass the same mechanisms. Therefore, privacy compliance should cover the main website, subdomains, online stores, standalone advertising pages, and embedded forms, rather than only the homepage.
Incorporate Compliance into Website Acceptance, Rather Than Treating It as a Post-Launch Patch
For mature integrated website and marketing service projects, target markets, data types, and marketing tools should be confirmed during the requirements stage, rather than adding a privacy pop-up after the website visual design has been approved. Website acceptance can include several clear checks: whether privacy policy links are accessible in forms and the footer; whether Cookie selections affect the relevant scripts; whether third-party components are included in the inventory; whether test leads can be fully traced through their deletion and export paths; and whether records are retained for permission changes.
Yiyingbao has long served foreign trade companies, manufacturing plants, cross-border sellers, and brand globalization projects. Its intelligent website development, SEO, advertising placement, and social media operations often form part of the same customer acquisition chain. For companies using such end-to-end services, what truly needs to be clarified are the responsibility boundaries among the website development platform, marketing systems, and the company's internal CRM: who configures tags, who safeguards leads, who responds to user requests, and who is responsible for periodic reviews. Technical capabilities can enable multilingual websites and marketing touchpoints to go live more quickly, but compliance responsibilities still need to be jointly confirmed by business, technical, and security teams.
There is no “universal template” for overseas privacy compliance that remains applicable forever. Each time a website adds a new form, plug-in, advertising platform, or AI tool, its data processing methods may change. Rather than carrying out urgent rectification after a complaint, audit, or platform restriction, it is better to make data inventories, script management, and acceptance records a fixed part of international website operations. Being able to clearly explain where data comes from, why it is collected, where it flows, and when it is deleted is the more reliable baseline for a corporate website facing overseas markets.
Related Articles
 China's Ministry of Commerce Updates the Export Control List for Dual-Use Items; Related Adjustments Take Effect on the 18th
 New Cross-Border E-Commerce Rules Take Effect in Quick Succession in November as Multiple Countries Tighten Oversight
 New SWIFT rules take effect on November 14: payment messages with fully unstructured addresses will be rejected

Related Products
 Yiyingbao SaaS Intelligent Website Building and Marketing SystemYiyingbao SaaS Intelligent Website Building and Marketing System, AI-powered no-code website building, rapid creation of multilingual B2B international websites in 10 minutes, global server acceleration, AI-powered SEO optimization, helping businesses connect efficiently with global markets. The perfect integration of technology and operation makes building an international trade website remarkably simple
 AI+SEM Intelligent Advertising Marketing SystemAI+SEM drives intelligent ad creation, empowering full-funnel precision advertising marketing. The system automatically generates weekly/monthly reports, AI recommends keywords and target countries, monitors core metrics in real-time with intelligent alerts, and enables one-click high-conversion ad solutions to help quickly acquire customers and improve ROI.
 AI+SEO Dual-Engine System Optimization ServicesYiyingbao’s AI+SEO dual-engine optimization system helps foreign trade enterprises acquire high-quality organic traffic through AI-powered keyword research, content generation, and comprehensive technical optimization, significantly improving search rankings and conversion rates.
 AI+SNS Social Media Marketing SystemYingbao AI+SNS Social Media Marketing System - Precision social capture for the social media era. Supports one-click content synchronization across major platforms like Facebook and LinkedIn. AI intelligently rewrites posts for enhanced relevance. 24/7 AI customer service and user profiling analysis empower businesses to efficiently expand into global markets.
 AI+SEO营销解决方案易营宝AI+SEO营销解决方案,通过AI批量写作、智能生成TDK、精准关键词扩词等功能,全面优化网站SEO效果,提升流量与转化率。助力企业构建高效智能网站新生态。
 AI+SEM Advertising Marketing SolutionsAI+SEM Advertising Marketing Solution leverages AI technology to deeply empower SEM ad campaigns. It automatically generates weekly/monthly reports using AI, presenting account data across multiple dimensions for comprehensive insights into campaign performance and trends. The system precisely recommends keywords and target countries, intelligently generates high-conversion ad copy, and enables one-click activation of efficient campaign plans to help businesses rapidly acquire customers. Simultaneously, it monitors core metrics in real time, intelligently identifies abnormal fluctuations, and issues timely alerts to ensure stable, high-return advertising results.
 Domain Name ServicesEasyWin provides professional domain name services, including intelligent queries, one-stop registration, brand protection, and full lifecycle management, helping businesses build a digital brand image.
 EasyOperate B2C Cross-Border E-Commerce Platform & Independent WebsiteEasyStore B2C Cross-border E-commerce Independent Store is an intelligent website building and cross-border e-commerce integrated solution independently developed by EasyStore Information Technology (Beijing) Co., Ltd. The system is specially designed for small and medium-sized as well as large export enterprises, integrating 'website building, operation, marketing, advertising, and conversion' into one, helping enterprises quickly establish cross-border e-commerce independent stores to achieve brand globalization and global sales growth.
The platform supports multiple languages, multiple currencies, and multi-channel marketing, with built-in AI intelligent translation and SEO optimization systems, suitable for mainstream markets such as Southeast Asia, Europe and America, Latin America, and the Middle East, assisting Chinese manufacturing enterprises in efficiently deploying international e-commerce strategies. SSL证书易营宝提供专业SSL安全证书服务,包括单域名和泛域名证书,确保网站数据传输加密、身份验证和完整性保护,助力企业建立安全可信的在线业务环境。









